Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

DOP-C02 Exam Dumps and Practice Questions

Preview page 1 of 90 with real questions 1 to 5 from the full 449-question Amazon set.

Amazon DOP-C02 Dumps - Pass the AWS Certified DevOps Engineer - Professional Exam in 2026

The Amazon DOP-C02 - AWS Certified DevOps Engineer - Professional Exam is part of the Amazon Professional certification track. It is designed for professionals who work with DevOps practices, cloud operations, automation, and secure delivery in AWS environments. This exam matters because it validates the ability to build, operate, and manage reliable cloud solutions at a professional level. It is a strong credential for candidates who want to prove advanced, hands-on DevOps skills.

# Exam Topics Sub-Topics Approximate Weightage (%)
1 SDLC Automation CI/CD pipelines, deployment automation, release strategies 18%
2 Configuration Management and IaC Infrastructure as Code, configuration templates, version-controlled environments 18%
3 Resilient Cloud Solutions High availability, fault tolerance, scaling strategies 18%
4 Monitoring and Logging Metrics, centralized logging, alerting and dashboards 16%
5 Incident and Event Response Event handling, troubleshooting workflows, recovery actions 15%
6 Security and Compliance Access control, policy enforcement, audit and compliance checks 15%

The exam tests practical DevOps knowledge, not just theory. Candidates are expected to understand how to automate delivery, manage infrastructure with code, monitor cloud systems, respond to incidents, and apply security controls in real-world AWS environments. It also checks decision-making skills, so you need to choose the best solution based on reliability, efficiency, and operational needs.

Actual Amazon DOP-C02 Exam Questions

Question 1

A company is running a custom-built application that processes records. All the components run on Amazon EC2 instances that run in an Auto Scaling group. Each record's processing is a multistep sequential action that is compute-intensive. Each step is always completed in 5 minutes or less.

A limitation of the current system is that if any steps fail, the application has to reprocess the record from the beginning The company wants to update the architecture so that the application must reprocess only the failed steps.

What is the MOST operationally efficient solution that meets these requirements?

Correct answer: D

* Use AWS Step Functions to Orchestrate Processing:

AWS Step Functions allow you to build distributed applications by combining AWS Lambda functions or other AWS services into workflows.

Decoupling the processing into Step Functions tasks enables you to retry individual steps without reprocessing the entire record.

* Architectural Steps:

Create a web application to pass records to AWS Step Functions:

The web application can be a simple frontend that receives input and triggers the Step Functions workflow.

Define a Step Functions state machine:

Each step in the state machine represents a processing stage. If a step fails, Step Functions can retry the step based on defined conditions.

Use AWS Lambda functions:

Lambda functions can be used to handle each processing step. These functions can be stateless and handle specific tasks, reducing the complexity of error handling and reprocessing logic.

* Operational Efficiency:

Using Step Functions and Lambda improves operational efficiency by providing built-in error handling, retries, and state management.

This architecture scales automatically and isolates failures to individual steps, ensuring only failed steps are retried.

References:

AWS Step Functions

Building Workflows with Step Functions

Question 2

A company's application teams use AWS CodeCommit repositories for their applications. The application teams have repositories in multiple AWS

accounts. All accounts are in an organization in AWS Organizations.

Each application team uses AWS IAM Identity Center (AWS Single Sign-On) configured with an external IdP to assume a developer IAM role. The developer role allows the application teams to use Git to work with the code in the repositories.

A security audit reveals that the application teams can modify the main branch in any repository. A DevOps engineer must implement a solution that

allows the application teams to modify the main branch of only the repositories that they manage.

Which combination of steps will meet these requirements? (Select THREE.)

Correct answer: A, D, F

Short To meet the requirements, the DevOps engineer should update the SAML assertion to pass the user's team name, update the IAM role's trust policy to add an access-team session tag that has the team name, create an IAM permissions boundary in each account, and for each CodeCommit repository, add an access-team tag that has the value set to the name of the associated team.

:

Updating the SAML assertion to pass the user's team name allows the DevOps engineer to use IAM tags to identify which team a user belongs to. This can help enforce fine-grained access control based on the user's team membership1.

Updating the IAM role's trust policy to add an access-team session tag that has the team name allows the DevOps engineer to use IAM condition keys to restrict access based on the session tag value2. For example, the DevOps engineer can use the aws:PrincipalTag condition key to match the access-team tag of the user with the access-team tag of the repository3.

Creating an IAM permissions boundary in each account allows the DevOps engineer to set the maximum permissions that an identity-based policy can grant to an IAM entity. An entity's permissions boundary allows it to perform only the actions that are allowed by both its identity-based policies and its permissions boundaries4. For example, the DevOps engineer can use a permissions boundary policy to limit the actions that a user can perform on CodeCommit repositories based on their access-team tag5.

For each CodeCommit repository, adding an access-team tag that has the value set to the name of the associated team allows the DevOps engineer to use resource tags to identify which team manages a repository. This can help enforce fine-grained access control based on the resource tag value6.

The other options are incorrect because:

Creating an approval rule template for each team in the Organizations management account is not a valid option, as approval rule templates are not supported by AWS Organizations. Approval rule templates are specific to CodeCommit and can only be associated with one or more repositories in the same AWS Region where they are created7.

Creating an approval rule template for each account is not a valid option, as approval rule templates are not designed to restrict access to modify branches. Approval rule templates are designed to require approvals from specified users or groups before merging pull requests8.

Attaching an SCP to the accounts is not a valid option, as SCPs are not designed to restrict access based on tags. SCPs are designed to restrict access based on service actions and resources across all users and roles in an organization's account9.


Question 3

A company manages a web application that runs on Amazon EC2 instances behind an Application Load Balancer (ALB). The EC2 instances run in an Auto Scaling group across multiple Availability Zones. The application uses an Amazon RDS for MySQL DB instance to store the dat

a. The company has configured Amazon Route 53 with an alias record that points to the ALB.

A new company guideline requires a geographically isolated disaster recovery (DR> site with an RTO of 4 hours and an RPO of 15 minutes.

Which DR strategy will meet these requirements with the LEAST change to the application stack?

Correct answer: D

Question 4

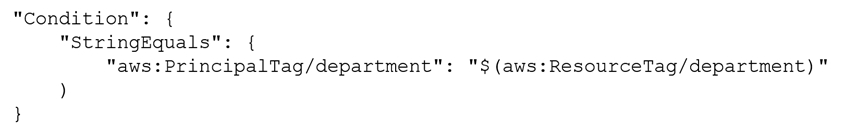
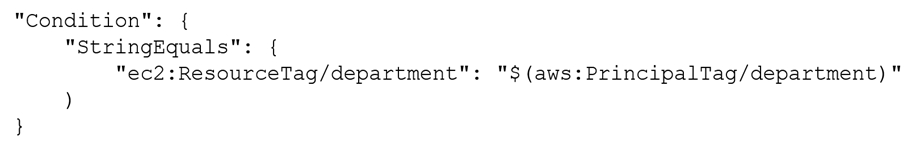
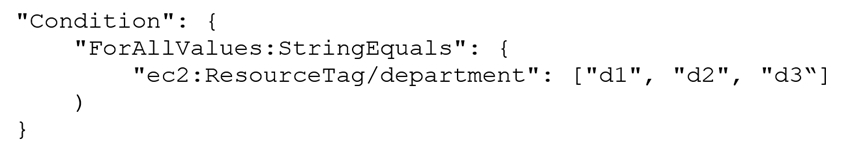
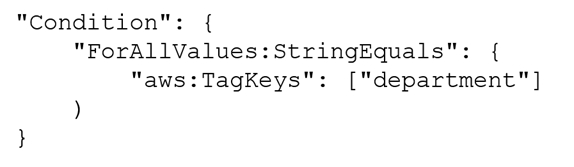
A company has multiple AWS accounts. The company uses AWS IAM Identity Center (AWS Single Sign-On) that is integrated with AWS Toolkit for Microsoft Azure DevOps. The attributes for access control feature is enabled in IAM Identity Center.

The attribute mapping list contains two entries. The department key is mapped to ${path:enterprise.department}. The costCenter key is mapped to ${path:enterprise.costCenter}.

All existing Amazon EC2 instances have a department tag that corresponds to three company departments (d1, d2, d3). A DevOps engineer must create policies based on the matching attributes. The policies must minimize administrative effort and must grant each Azure AD user access to only the EC2 instances that are tagged with the user's respective department name.

Which condition key should the DevOps engineer include in the custom permissions policies to meet these requirements?

A.

B.

C.

D.

Correct answer: C

https://docs.aws.amazon.com/singlesignon/latest/userguide/configure-abac.html


Question 5

A developer is creating a proof of concept for a new software as a service (SaaS) application. The application is in a shared development AWS account that is part of an organization in AWS Organizations.

The developer needs to create service-linked IAM roles for the AWS services that are being considered for the proof of concept. The solution needs to give the developer the ability to create and configure the service-linked roles only.

Which solution will meet these requirements?

Correct answer: D

To allow only creation/configuration of service-linked roles, you need a way to tightly scope what IAM actions the developer can perform. The most AWS-appropriate mechanism for ''delegate limited IAM admin'' is a role with a permissions boundary:

A permissions boundary sets the maximum permissions the role (and any roles it creates, depending on design) can ever have. This is a standard pattern to safely delegate IAM tasks without granting broad IAM administration.

You can define the role's policy + boundary so the developer can call only the APIs required for service-linked roles (for example actions like creating service-linked roles and passing only allowed AWS service principals), while preventing general role/policy creation outside that scope.

Why the others don't meet ''service-linked roles only'':

A is vague (''common services'') and cross-account access doesn't inherently restrict to only service-linked roles. It's also more operational overhead than needed for a single dev account use case.

B PowerUserAccess is far too broad and does not restrict to service-linked roles.

C An SCP with Deny iam:* would block IAM entirely (including what the developer needs). Even if refined, SCPs set account-wide guardrails and are not the right tool to grant a single developer the precise ability to create only service-linked roles.


Unlock all Amazon DOP-C02 questions

Full exam access, validated answers, and unlimited practice with no download limits.

How QA4Exam.com Helps You Pass

QA4Exam.com offers Exam PDF and Online Practice Test materials that are built to help you prepare for the Amazon DOP-C02 exam with confidence. The Exam PDF gives you actual questions and answers in a simple study format, while the Online Practice Test helps you experience real exam simulation before test day. Both resources are designed to provide up-to-date questions, verified answers, and focused practice on the exam topics. You can also improve time management by practicing under exam-like conditions, which is important for passing on the first attempt.

Frequently Asked Questions

Who should take the Amazon AWS Certified DevOps Engineer - Professional Exam?

This exam is for professionals who work with DevOps, cloud operations, automation, and AWS-based delivery workflows. It fits candidates who want to validate advanced skills as part of the Amazon Professional certification path.

Is the DOP-C02 exam considered difficult?

Yes, it is generally considered a professional-level exam because it focuses on practical decisions, not just memorization. You need strong understanding of automation, resilience, monitoring, incident response, and security.

Can I pass the exam with only braindumps?

Braindumps alone are not the best approach. You should use them as a study aid along with hands-on knowledge and practice to understand the concepts behind the answers.

Do I need hands-on experience to pass DOP-C02?

Hands-on experience is very helpful because the exam tests practical DevOps and AWS skills. Real-world practice makes it easier to understand scenario-based questions and choose the correct solution.

How can QA4Exam.com help me pass on the first attempt?

QA4Exam.com helps by giving you actual questions and answers in the Exam PDF and realistic exam practice in the Online Practice Test. This combination supports faster revision, better accuracy, and stronger time management.

What is included in the QA4Exam.com practice test format?

The practice test format is designed to simulate the exam experience and help you check your readiness. It focuses on exam-style questions, verified answers, and timed practice for better preparation.

Are the QA4Exam.com questions up to date for DOP-C02?

The materials are presented as up-to-date study resources for the exam. They are intended to help you stay aligned with the current DOP-C02 exam preparation needs.