Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

S90.20 Exam Dumps and Practice Questions

Preview page 1 of 6 with real questions 1 to 5 from the full 30-question Arcitura Education set.

Arcitura Education S90.20 Dumps - Pass SOA Security Lab Exam in 2026

The Arcitura Education S90.20 - SOA Security Lab exam is part of the Certified SOA Security Specialist certification path. It is designed for candidates who want to prove their knowledge of securing services, microservices, and SOA environments. This exam matters for professionals who need a strong understanding of both security concepts and practical lab-based application. It helps validate the skills needed to work with modern service architectures in real-world security scenarios.

Exam Topics and Approximate Weightage

# Exam Topics Sub-Topics Approximate Weightage (%)
1 Fundamental SOA, Services & Microservices SOA principles, service orientation, microservices basics, service interaction models 18%
2 Microservice Technology Concepts Container concepts, deployment patterns, service communication, scalability considerations 18%
3 Fundamental Security for Services, Microservices & SOA Authentication basics, authorization basics, message protection, identity and access concepts 20%
4 Advanced Security for Services, Microservices & SOA Security design strategies, policy enforcement, secure communication, advanced protection controls 22%
5 Security Lab for Services, Microservices & SOA Lab-based scenario analysis, security configuration, problem solving, practical validation of controls 22%

Actual Arcitura Education S90.20 Exam Questions

Question 1

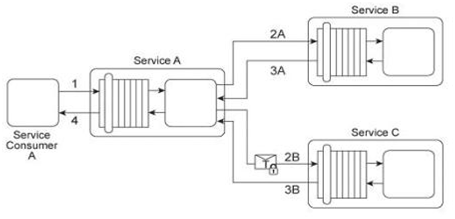
Service A is a publically accessible service that provides free multimedia retrieval capabilities to a range of service consumers. To carry out this functionality, Service A is first invoked by Service Consumer A (1). Based on the nature of the request message received from Service Consumer A, Service A either invokes Service B or Service C .When Service B is invoked by Service A (2A) it retrieves data from publicly available sources (not shown) and responds with the requested data (3A). When Service C is invoked by Service A (2B) it retrieves data from proprietary sources within the IT enterprise (not shown) and responds with the requested data (3B). After receiving a response from Service B or Service C, Service A sends the retrieved data to Service Consumer A (4). Service B does not require service consumers to be authenticated, but Service C does require authentication of service consumers. The service contract for Service A therefore uses WS-Policy alternative policies in order to express the two different authentication requirements to Service Consumer A .When Service Consumer A sends a request message (1), Service A determines whether the request requires the involvement of Service C and then checks to ensure that the necessary security credentials were received as part of the message. If the credentials provided by Service Consumer A are verified. Service A creates a signed SAML assertion and sends it with the request message to Service C (2B) This authentication information is protected by public key encryption However, responses to Service Consumer A's request message (3B, 4) are not encrypted for performance reasons. Recently, the usage of Service C has noticeably declined. An investigation has revealed response messages issued by Service C (3B) have been repeatedly intercepted and accessed by unauthorized and malicious intermediaries. As a result, Service Consumer A has lost confidence in the use of Service A for the retrieval of proprietary data because it is being viewed as a security risk. This is especially troubling, because the owner of Service A had planned to start charging a fee for Service A's ability to provide proprietary data via the use of Service C .How can this service composition architecture be changed to address the security problem with minimal impact on runtime performance?
Correct answer: C

Question 2

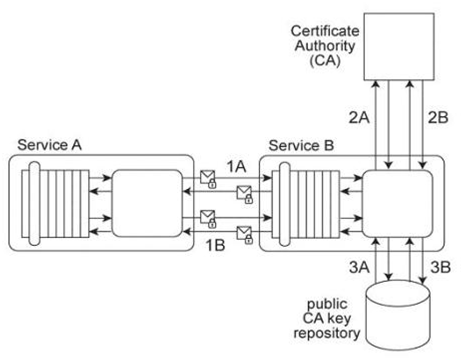
Service A exchanges messages with Service B multiple times during the same runtime service activity. Communication between Services A and B has been secured using transport-layer security. With each service request message sent to Service B (1A .IB), Service A includes an X.509 certificate, signed by an external Certificate Authority (CA). Service B validates the certificate by retrieving the public key of the CA (2A .2B) and verifying the digital signature of the X.509 certificate. Service B then performs a certificate revocation check against a separate external CA repository (3A, 3B). No intermediary service agents reside between Service A and Service B .Service B has recently suffered from poor runtime performance plus it has been the victim of an access-oriented attack. As a result, its security architecture must be changed to fulfill the following new requirements:

1. The performance of security-related processing carried out by Service B when communicating with Service A must be improved.

2. All request messages sent from Service A to Service B must be screened to ensure that they do not contain malicious content. Which of the following statements describes a solution that fulfills these requirements?

Correct answer: B

Question 3

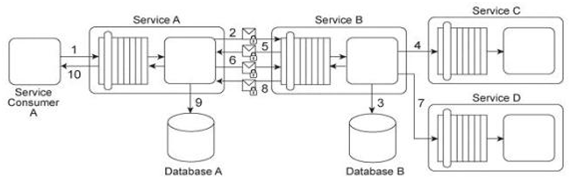
Service Consumer A sends a request message to Service A (1), after which Service A sends a request message with security credentials to Service B (2). Service B authenticates the request and, if the authentication is successful, writes data from the request message into Database B (3). Service B then sends a request message to Service C (4), which is not required to issue a response message. Service B then sends a response message back to Service A (5). After processing Service B's response, Service A sends another request message with security credentials to Service B (6). After successfully authenticating this second request message from Service A, Service B sends a request message to Service D (7). Service D is also not required to issue a response message. Finally, Service B sends a response message to Service A (8), after which Service A records the response message contents in Database A (9) before sending its own response message to Service Consumer A (10). To use Service A, Service Consumer A is charged a per usage fee. The owner of Service Consumer A has filed a complaint with the owner of Service A, stating that the bills that have been issued are for more usage of Service A than Service Consumer A actually used. Additionally, it has been discovered that malicious intermediaries are intercepting and modifying messages being sent from Service B to Services C and D .Because Services C and D do not issue response messages, the resulting errors and problems were not reported back to Service B .Which of the following statements describes a solution that correctly addresses these problems?

Correct answer: A

Question 4

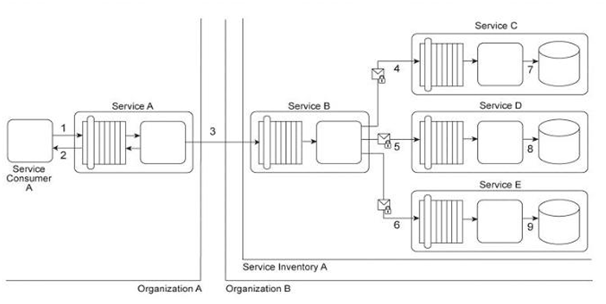
Service Consumer A sends a request to Service A (1). Service A replies with an acknowledgement message (2) and then processes the request and sends a request message to Service B (3). This message contains confidential financial data. Service B sends three different request messages together with its security credentials to Services C, D, and E (4, 5, 6). Upon successful authentication, Services C, D, and E store the data from the message in separate databases (7, 8, 9) Services B, C, D, and E belong to Service Inventory A, which further belongs to Organization B .Service Consumer A and Service A belong to Organization A .The service contracts of Services A and B both comply with the same XML schema. However, each organization employs different security technologies for their service architectures. To protect the confidential financial data sent by Service A to Service B, each organization decides to independently apply the Data Confidentiality and the Data Origin Authentication patterns to establish message-layer security for external message exchanges. However, when an encrypted and digitally signed test message is sent by Service A to Service B, Service B was unable to decrypt the message. Which of the following statements describes a solution that solves this problem?

Correct answer: A

Question 5

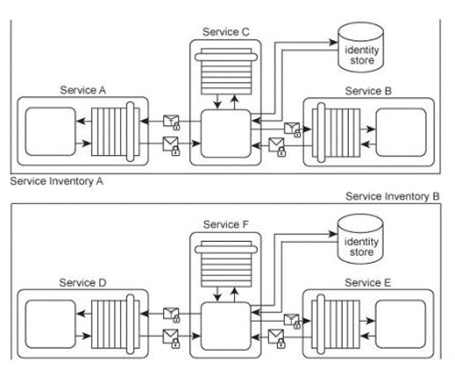
Services A, B and C belong to Service Inventory A .Services D, E and F belong to Service Inventory B .Service C acts as an authentication broker for Service Inventory A .Service F acts as an authentication broker for Service Inventory B .Both of the authentication brokers use Kerberos-based authentication technologies. Upon receiving a request message from a service consumer, Services C and F authenticate the request using a local identity store and then use a separate Ticket Granting Service (not shown) to issue the Kerberos ticket to the service consumer. Currently, tickets issued in one service inventory are not valid in the other. For example, if Service A wants to communicate with Services D or E, it must request a ticket from the Service Inventory B authentication broker (Service F). Because Service Inventory A and B trust each other, the current cross-inventory authentication is considered unnecessarily redundant. How can these service inventory architectures be improved to avoid redundant authentication?

Correct answer: C

Unlock all Arcitura Education S90.20 questions

Full exam access, validated answers, and unlimited practice with no download limits.

The exam tests more than memorization. Candidates must understand core concepts, recognize how security applies across services and microservices, and handle practical lab-style scenarios with confidence. It also checks whether you can apply knowledge to realistic situations, making hands-on understanding and careful exam preparation important.

Frequently Asked Questions

1. Who should take the Arcitura Education S90.20 SOA Security Lab exam?

This exam is for candidates pursuing the Certified SOA Security Specialist certification and for professionals who want to validate their knowledge of securing services, microservices, and SOA environments.

2. Is the SOA Security Lab exam difficult?

It can be challenging because it covers both concepts and practical security application. Candidates who understand the topics and practice with realistic questions usually feel more prepared.

3. Can I pass with only braindumps?

Relying on dumps alone is not a smart strategy. You should use them as a study aid alongside topic review and practice so you understand the exam instead of just memorizing answers.

4. Do I need hands-on experience for this exam?

Hands-on understanding is very helpful because the exam includes lab-oriented security topics. Practical familiarity with service and microservice security can improve your confidence and performance.

5. Are the QA4Exam.com dumps and practice test enough to prepare?

They are very useful study tools because they provide actual questions and answers, verified content, and exam simulation. For best results, use them with topic review so you cover both knowledge and test strategy.

6. How do QA4Exam.com dumps help with first-attempt success?

They help you focus on likely exam areas, understand question style, and practice answering under time pressure. That combination can improve readiness and increase your chances of passing on the first attempt.

7. What format do the QA4Exam.com study materials come in?

QA4Exam.com provides an Exam PDF and an Online Practice Test. The PDF is convenient for focused study, while the practice test is designed to simulate the real exam environment.