
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

200-201 Exam Dumps and Practice Questions

Preview page 1 of 95 with real questions 1 to 5 from the full 476-question Cisco set.

Cisco 200-201 Dumps - Pass Understanding Cisco Cybersecurity Operations Fundamentals in 2026

The Cisco 200-201 exam, "Understanding Cisco Cybersecurity Operations Fundamentals," is part of the Cisco Certified CyberOps Associate certification track. It is designed for candidates who want to build a strong foundation in cybersecurity operations and understand how security teams monitor, analyze, and respond to threats. This exam matters because it validates core knowledge that supports entry-level cyber operations roles and practical security workflows.

Exam Topics Overview

# Exam Topics Sub-Topics Approximate Weightage (%)
1 Security Concepts Threat types and attack vectors; security principles; CIA triad; basic risk concepts 20%
2 Security Monitoring Alert review; log analysis; event correlation; monitoring tools and workflows 22%
3 Host-Based Analysis Endpoint indicators; process and file review; malware signs; host log investigation 18%
4 Network Intrusion Analysis Traffic inspection; intrusion indicators; packet and flow analysis; suspicious communication patterns 24%
5 Security Policies and Procedures Incident response steps; documentation practices; escalation procedures; policy awareness 16%

The Cisco 200-201 exam tests whether candidates can understand cybersecurity operations fundamentals and apply them in practical monitoring and analysis scenarios. It focuses on recognizing security events, interpreting host and network evidence, and following policies and procedures used in a security operations environment. Candidates need both conceptual knowledge and the ability to evaluate situations quickly and accurately.

Actual Cisco 200-201 Exam Questions

Question 1

What is the name of the technology that searches for and reports on known weaknesses and flaws present in an organization's IT infrastructure?

Correct answer: A

A vulnerability scanner is a core security technology used to identify known weaknesses, misconfigurations, and exploitable flaws within an organization's IT infrastructure. These tools systematically scan systems, networks, applications, and devices to compare them against databases of known vulnerabilities, such as missing patches, insecure services, outdated software versions, and weak configurations.

Vulnerability scanners operate by probing systems using signatures, checks, and authenticated or unauthenticated methods to determine exposure to threats. The results are typically presented in detailed reports that include severity ratings, affected assets, and remediation guidance. This makes vulnerability scanning an essential foundational activity in cybersecurity operations, risk management, and compliance programs.

The other options do not fulfill this function. Identity and access management focuses on user authentication, authorization, and access control, not weakness detection. Configuration management ensures systems remain in a desired state but does not actively discover vulnerabilities. Mobile device management is limited to controlling and securing mobile endpoints rather than assessing infrastructure-wide weaknesses.
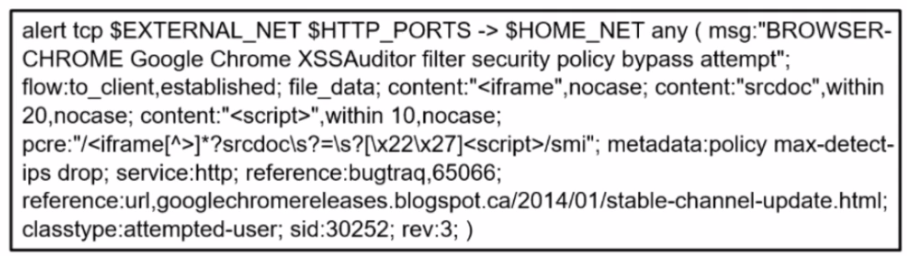

Question 2

Refer to the exhibit.

A company's user HTTP connection to a malicious site was blocked according to configured policy What is the source technology used for this measure'?

Correct answer: D

A web proxy is the technology used to block a user's HTTP connection to a malicious site according to configured policy. It acts as an intermediary between users and the internet, enforcing security policies and preventing access to harmful sites by inspecting and managing web traffic.


Question 3
Question 4

Which security model assumes an attacker within and outside of the network and enforces strict verification before connecting to any system or resource within the organization?

Correct answer: D

The Zero Trust security model operates on the principle that no one is trusted by default from inside or outside the network, and verification is required from everyone trying to gain access to resources on the network. It emphasizes continuous monitoring, validation, and least-privilege access to minimize exposure to sensitive parts of the network.


Question 5

An employee of a company receives an email with an attachment. They notice that this email is from a suspicious source, and they decide not to open the attached file. After further investigation, a security analyst concludes that this file is malware. To which category of the Cyber Kill Chain model does this event belong?

Correct answer: D

This event belongs to the Weaponization</strong phase of the Cyber Kill Chain model. In the Weaponization phase, threat actors prepare malicious tools and payloads (in this case, the malware-laden email attachment). The employee's action of not opening the file prevented progression to the next phase (Delivery). The Cyber Kill Chain phases are: Reconnaissance, Weaponization, Delivery, Exploitation, Installation, Command and Control, and Actions on Objectives.

Unlock all Cisco 200-201 questions

Full exam access, validated answers, and unlimited practice with no download limits.

How QA4Exam.com Helps You Pass

QA4Exam.com offers Exam PDF material with actual questions and answers, plus an Online Practice Test designed for the Cisco 200-201 exam. These resources help you study with up-to-date questions, verified answers, and a format that mirrors real exam conditions. The practice test also helps you build time management skills so you can answer questions faster and stay calm under pressure. With focused preparation and realistic exam simulation, you can improve your readiness and aim to pass on your first attempt.

Frequently Asked Questions

Who should take the Cisco 200-201 exam?

This exam is for candidates pursuing the Cisco Certified CyberOps Associate certification and for those who want to validate foundational cybersecurity operations knowledge.

Is the Cisco Understanding Cisco Cybersecurity Operations Fundamentals exam difficult?

It can be challenging if you are new to security operations because it covers monitoring, analysis, and procedures, but focused preparation makes it manageable.

Can I pass Cisco 200-201 with only braindumps?

Using dumps alone is not the best approach. They are useful for understanding question style and checking readiness, but you should also review the exam topics and concepts.

Do I need hands-on experience for this exam?

Hands-on exposure is helpful because the exam includes practical security monitoring and analysis concepts, but solid study materials can still help you prepare effectively.

How do QA4Exam.com dumps help me pass on the first attempt?

They provide actual questions and answers, verified content, and a realistic practice environment so you can study efficiently and improve your confidence before exam day.

What is the difference between the Exam PDF and the Online Practice Test?

The Exam PDF is ideal for review and memorization of questions and answers, while the Online Practice Test gives you interactive exam simulation and time management practice.

Are the QA4Exam.com questions and answers up to date?

QA4Exam.com provides updated exam content with verified answers to help you stay aligned with the Cisco 200-201 exam format and topic coverage.