Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

300-215 Exam Dumps and Practice Questions

Questions 1 to 5 of the 184-question 300-215 bank, each with its correct answer and an explanation. This is page 1 of 37.

1 / 37

Actual Cisco 300-215 Exam Questions

Question 1

Refer to the exhibit.

A security analyst is reviewing alerts from the SIEM system that was just implemented and notices a possible indication of an attack because the SSHD system just went live and there should be nobody using it. Which action should the analyst take to respond to the alert?

Correct answer: A

The log entry shows a failed SSH login attempt for an invalid user ''admin'' from IP 192.168.1.100. As the system has just gone live and no legitimate use is expected, this could be an early reconnaissance or brute-force attempt. However, blocking IPs or resetting passwords without fully understanding the context could lead to incomplete remediation or false positives.

According to Cisco CyberOps best practices, the first step is to thoroughly investigate the alert by correlating it with other logs (e.g., authentication logs, IDS/IPS logs) to determine the intent and scope of activity.

---

Question 2

Refer to the exhibit.

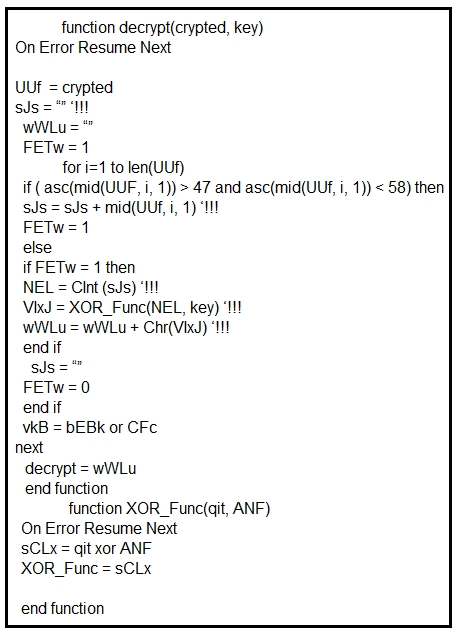
Which type of code created the snippet?

Correct answer: A

The syntax in the code snippet includes:

On Error Resume Next -- a classic VBScript error-handling directive.

function ... end function structure.

Use of Mid(), Chr(), and Asc() functions -- all commonly used in VBScript for string manipulation.

CInt() for conversion -- typical in VBScript.

These characteristics align exactly with VBScript, which is frequently used in malicious macros and obfuscated payloads for malware distribution, as covered in the Cisco CyberOps Associate curriculum when analyzing scripts and encoded threats.


Question 3

Refer to the exhibit.

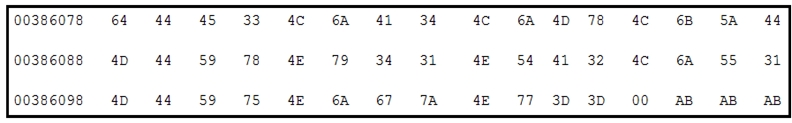
Which encoding technique is represented by this HEX string?

Correct answer: D

The hexadecimal representation in the exhibit does not match the Base64 encoding format, which uses ASCII characters (A-Z, a-z, 0-9, +, /) and often includes padding with =. This string is clearly hex and is more aligned with Charcode, where hexadecimal values represent individual characters based on ASCII values.

The Cisco CyberOps Associate guide refers to such encodings during forensic analysis and emphasizes identifying patterns in memory dumps, payloads, or logs. 'Security professionals often decode hexadecimal strings to reveal ASCII representations, particularly when inspecting encoded payloads or character obfuscation techniques used in malware'.


Question 4

A network host is infected with malware by an attacker who uses the host to make calls for files and shuttle traffic to bots. This attack went undetected and resulted in a significant loss. The organization wants to ensure this does not happen in the future and needs a security solution that will generate alerts when command and control communication from an infected device is detected. Which network security solution should be recommended?

Correct answer: B

The Cisco Secure Firewall Threat Defense (Firepower) includes advanced capabilities such as intrusion prevention, URL filtering, and deep packet inspection. According to the CyberOps guide, it can detect and block C2 communications by analyzing traffic patterns and comparing them to threat intelligence data. The guide specifically states: 'Advanced solutions such as Firepower provide detection capabilities for command and control (C2) traffic by identifying unusual outbound connections and behavioral anomalies'.


Question 5

Refer to the exhibit.

What is occurring?

Correct answer: D

The command in the image uses schtasks /create with the ONLOGON schedule and System user context to execute test.exe. This is a well-documented persistence technique, where an attacker ensures that a malicious executable is launched automatically at each system logon. This kind of scheduled task creation aligns with persistence techniques in the MITRE ATT&CK framework (T1053).

---


Unlock all Cisco 300-215 questions

Full exam access, validated answers, and unlimited practice with no download limits.