Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

300-220 Exam Dumps and Practice Questions

Questions 1 to 5 of the 60-question 300-220 bank, each with its correct answer and an explanation. 1 of 5 ask for more than one answer. This is page 1 of 12.

1 / 12

Actual Cisco 300-220 Exam Questions

Question 1

Refer to the exhibit.
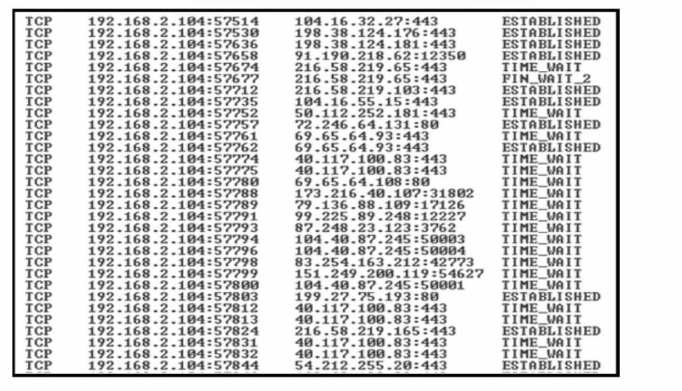
A security team detects a spike in traffic from the company web server. After further investigation, the team discovered that multiple connections have been established from the server to different IP addresses, but the web server logs contain both expected traffic and DDoS traffic. Which attribute must the team use to further filter the logs?

Correct answer: A

The correct answer is Connection status. In this scenario, the key challenge for the security team is differentiating legitimate outbound traffic from malicious or DDoS-related traffic originating from the same web server. Since both types of traffic coexist in the logs, analysts must rely on an attribute that meaningfully distinguishes normal behavior from abnormal patterns.

The exhibit shows numerous TCP connections from the web server to many different external IP addresses, with varying TCP states such as ESTABLISHED, TIME_WAIT, and FIN_WAIT. These connection states are highly valuable for threat hunting and network analysis. During DDoS activity---especially reflected or amplification-style attacks, or when a server is abused as part of an attack---connections often remain half-open, rapidly transition to TIME_WAIT, or fail to fully establish. In contrast, legitimate web traffic typically results in stable, short-lived ESTABLISHED sessions that follow predictable patterns.

Option B (destination port) is not useful here because most web traffic---both legitimate and malicious---commonly uses ports 80 or 443. Option C (IP address of the web server) provides no filtering value because all traffic already originates from that server. Option D (protocol) is also ineffective, as both normal and DDoS traffic in this case use TCP.

From a professional SOC and threat hunting standpoint, connection state analysis is a foundational technique for detecting volumetric attacks, beaconing behavior, and abnormal session churn. By filtering logs based on connection status, analysts can quickly isolate suspicious patterns such as excessive short-lived connections, abnormal teardown behavior, or asymmetric session states that are characteristic of DDoS-related activity.

This approach aligns with mature threat hunting practices: when indicators overlap, pivot to behavioral attributes. Connection status provides the necessary behavioral signal to separate expected traffic from attack traffic and supports faster, more accurate incident response.

Question 2

After completing a threat hunt that uncovered previously undetected credential abuse, the SOC wants to ensure long-term improvement in detection and response capabilities. Which action BEST represents the final and most critical phase of the threat hunting lifecycle?

Correct answer: B

The correct answer is documenting findings and updating detection logic. This represents the post-hunt operationalization phase, which is critical for long-term security improvement.

While options A and C are necessary response actions, they address only the current incident. Threat hunting's strategic value comes from transforming discoveries into repeatable detections, playbooks, and controls.

Professional threat hunting programs ensure that:

Successful hunts produce new SIEM rules

Detection gaps are closed

Findings are documented for future analysts

Lessons learned inform security architecture decisions

Option D continues exploration but fails to institutionalize knowledge. Without operationalizing results, organizations repeatedly rediscover the same threats.

This phase directly increases maturity in the Threat Hunting Maturity Model, shifting organizations from hero-driven hunting to scalable, resilient detection. It also moves defenders up the Pyramid of Pain, forcing adversaries to change tactics rather than indicators.

Therefore, option B is the correct and most strategically important answer.


Question 3

A threat hunter is using Cisco Secure Network Analytics (Stealthwatch) to investigate possible lateral movement inside the network. Which behavior would MOST strongly indicate lateral movement using valid credentials?

Correct answer: B

The correct answer is internal systems authenticating to multiple hosts using SMB in a short time. This behavior is a classic indicator of credential-based lateral movement.

When attackers obtain valid credentials, they often move laterally by:

Accessing administrative shares (e.g., C$, ADMIN$)

Using SMB, WMI, WinRM, or RDP

Authenticating to multiple systems rapidly

Cisco Secure Network Analytics excels at identifying east-west traffic anomalies, which are central to lateral movement detection. A single host authenticating to many internal systems over SMB in a short time deviates strongly from normal user behavior.

Option A relates to external traffic, not lateral movement. Option C may indicate command-and-control or staging but not lateral movement. Option D aligns more with beaconing behavior.

This technique aligns with MITRE ATT&CK -- Lateral Movement and is explicitly covered in the CBRTHD blueprint under network-based threat hunting.

Thus, Option B is the correct answer.


Question 4

A SOC team using Cisco security technologies wants to distinguish Indicators of Attack (IOAs) from Indicators of Compromise (IOCs) during threat hunting. Which scenario BEST represents an IOA rather than an IOC?

Correct answer: C

The correct answer is Observation of repeated failed logins followed by a successful login from a new location. This scenario represents an Indicator of Attack (IOA) because it reflects attacker behavior in progress, not confirmed compromise.

IOAs focus on patterns of malicious intent, such as credential abuse, reconnaissance, or lateral movement, even when no malware or known indicators are present. In this case, the sequence of failed authentication attempts followed by a successful login from an unusual location strongly suggests password spraying or credential stuffing, both common initial access techniques.

Options A, B, and D are classic Indicators of Compromise (IOCs). Hashes, domains, and IP addresses are static artifacts that indicate a system has already been compromised. These indicators sit low on the Pyramid of Pain and are easy for attackers to change.

Cisco's CBRTHD blueprint emphasizes hunting for IOAs because they enable:

Earlier detection

Reduced dwell time

Higher attacker cost

Cisco tools such as Secure Network Analytics, Secure Endpoint, and SIEM platforms are designed to correlate behavioral signals like authentication anomalies rather than relying solely on known bad indicators.

Therefore, Option C is the correct and Cisco-aligned answer.


Question 5

Refer to the exhibit.

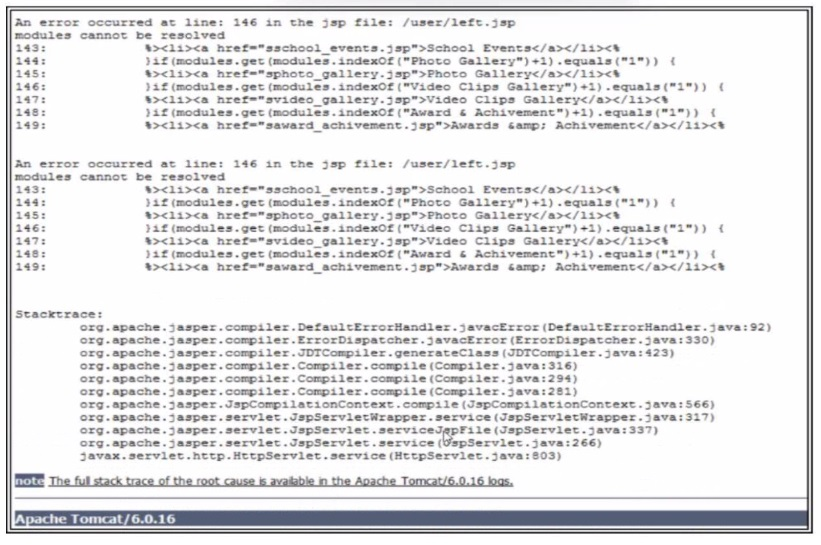
Refer to the exhibit. A penetration test performed against a web application generates the error message. Which two pieces of information are exposed? (Choose two.) Q Internal paths of the web server

Correct answer: A, C

The correct answers are A. Service and version of the web server and C. Technology used by the application. The error message shown in the exhibit is a classic example of verbose error handling, which unintentionally discloses sensitive internal details about the web application stack.

First, the error page explicitly references Apache Tomcat/6.0.16 at the bottom. This directly exposes the web server/service and its exact version, making Option A correct. From an attacker's perspective, this is valuable intelligence because it allows them to search for known vulnerabilities, exploits, or misconfigurations specific to that version of Tomcat. Older versions of Tomcat, in particular, have a long history of publicly documented security flaws.

Second, the stack trace references components such as:

org.apache.jasper.compiler.*

.jsp files (e.g., /user/left.jsp)

javax.servlet.http.HttpServlet

These details clearly reveal the technology stack used by the application, namely Java Server Pages (JSP) running on Apache Tomcat with Apache Jasper. This confirms Option C as correct. Exposing application technology helps attackers tailor attacks such as deserialization exploits, JSP injection attempts, or framework-specific vulnerabilities.

Option B is incorrect because the error message does not state or imply that Apache Jasper is vulnerable to path injection; it merely shows a compilation/runtime error. Option D is incorrect because the error page provides no information about the client-side browser version---all disclosed details relate to server-side processing.

From a professional security and threat hunting perspective, verbose error messages significantly increase attack surface visibility. Best practices dictate that production systems should return generic error messages to users while logging detailed stack traces internally. This scenario reinforces why proper error handling and information disclosure controls are critical defensive measures.

In summary, the penetration test error message exposes:

The web server service and version

The application technology stack

Therefore, the correct answers are A and C.


Unlock all Cisco 300-220 questions

Full exam access, validated answers, and unlimited practice with no download limits.