
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

CAS-004 Exam Dumps and Practice Questions

Preview page 1 of 122 with real questions 1 to 5 from the full 611-question CompTIA set.

Most Recent CompTIA CAS-004 Exam Dumps


Prepare for the CompTIA Advanced Security Practitioner (CASP+) Exam exam with our extensive collection of questions and answers. These practice Q&A are updated according to the latest syllabus, providing you with the tools needed to review and test your knowledge.

QA4Exam focus on the latest syllabus and exam objectives, our practice Q&A are designed to help you identify key topics and solidify your understanding. By focusing on the core curriculum, These Questions & Answers helps you cover all the essential topics, ensuring you're well-prepared for every section of the exam. Each question comes with a detailed explanation, offering valuable insights and helping you to learn from your mistakes. Whether you're looking to assess your progress or dive deeper into complex topics, our updated Q&A will provide the support you need to confidently approach the CompTIA CAS-004 exam and achieve success.

Actual CompTIA CAS-004 Exam Questions

Question 1

In support of disaster recovery objectives, a third party agreed to provide 99.999% uptime. Recently, a hardware failure impacted a firewall without service degradation. Which of the following resiliency concepts was most likely in place?

Correct answer: B

High availability ensures continuous operation despite hardware failures by leveraging redundant components like clustered firewalls or failover systems. This aligns with CASP+ objective 3.1, which focuses on implementing availability and redundancy mechanisms in disaster recovery planning.

________________________________________

Question 2

A company's product site recently had failed API calls, resulting in customers being unable to check out and purchase products. This type of failure could lead to the loss of customers and damage to the company's reputation in the market.

Which of the following should the company implement to address the risk of system unavailability?

Correct answer: D

Question 3

A security administrator is assessing the risk associated with using a software tool built by a small start-up company to provide product pricing updates. Which of the following risks would most likely be a factor?

Correct answer: B

Comprehensive and Detailed Step by Step

A startup may have limited resources, which could impact the security, reliability, and availability of its products.

Privacy concernsandregulatory complianceare possible risks but less relevant unless the tool deals directly with sensitive data or operates in a regulated industry.

Geographic locationis unlikely to directly affect the risk unless there are jurisdictional data transfer laws involved.


CompTIA CASP+ Exam Objective 1.2: Analyze the security risks and impacts of integrating diverse third-party products.

CASP+ Study Guide, 5th Edition, Chapter 2, Third-Party Risk Assessment.

Question 4

Which of the following BEST sets expectation between the security team and business units within an organization?

Correct answer: E

A service level agreement (SLA) is the best option to set expectations between the security team and business units within an organization. An SLA is a document that defines the scope, quality, roles, responsibilities, and metrics of a service provided by one party to another. An SLA can help align the security team's objectives and activities with the business units' needs andexpectations, as well as establish accountability and communication channels. Verified Reference: https://www.comptia.org/training/books/casp-cas-004-study-guide , https://searchitchannel.techtarget.com/definition/service-level-agreement


Question 5

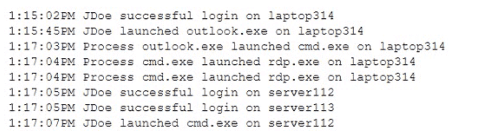
A SOC analyst received an alert about a potential compromise and is reviewing the following SIEM logs:

Which of the following is the most appropriate action for the SOC analyst to recommend?

Correct answer: B

The SIEM logs indicate suspicious behavior that could be a sign of a compromise, such as the launching of cmd.exe after Outlook.exe, which is atypical user behavior and could indicate that a machine has been compromised to perform lateral movement within the network. Isolating laptop314 from the network would contain the threat and prevent any potential spread to other systems while further investigation takes place.


Unlock all CompTIA CAS-004 questions

Full exam access, validated answers, and unlimited practice with no download limits.