A security operations center (SOC) analyst investigates the results of a password spray test conducted by the vulnerability management team.
The analyst must:
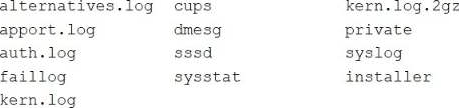
Identify Linux systems that have successful and unsuccessful logins with username "User1".
Create an output report named "linux-events" of all the events to a flat file.
The analyst issues the following console command:
ls /var/log/
The shortened output of the command is below:
Which of the following commands should the analyst use to meet the report output requirements?
/var/log/auth.log is the appropriate source because it records authentication and authorization activity on Debian/Ubuntu-style Linux systems, including password-related events, SSH logins, PAM authentication, and other authorization events. Canonical's Ubuntu documentation specifically identifies /var/log/auth.log as the authorization log used for password prompts, sudo, and remote logins.
The command performs three operations. cat /var/log/auth.log sends the log contents to standard output. The pipe forwards that data to grep 'User1', which selects records containing the required username. Finally, > linux-events.txt redirects the resulting matching records into the requested flat-file report. Because auth.log can contain both accepted and rejected authentication activity, the command can capture successful and unsuccessful events associated with User1.
sssd is not the general authentication log path shown in the scenario and may contain only SSSD-specific events. A faillog-oriented source emphasizes failed logins and therefore does not satisfy the requirement to collect both successful and failed activity. /var/log/syslog contains broad system messages but is less precise than the dedicated authentication log.
Study Guide Reference: Security Operations Linux Log Analysis /var/log/auth.log cat grep Output Redirection Authentication Investigation.