
Trusted Worldwide Questions & Answers
F5 Networks F5CAB1 Dumps - Pass BIG-IP Administration Install, Initial Configuration, and Upgrade Exam in 2026
The F5 Networks F5CAB1 exam, "BIG-IP Administration Install, Initial Configuration, and Upgrade," is part of the F5 Certified Administrator, BIG-IP Certification. It is designed for candidates who want to validate their ability to work with BIG-IP administration tasks across installation, configuration, upgrades, and day-to-day operations. This exam matters because it confirms practical knowledge needed to support and maintain F5 BIG-IP environments with confidence.
| # | Exam Topics | Sub-Topics | Approximate Weightage (%) |
|---|---|---|---|
| 1 | BIG IP Administration Data Plane Concepts | Traffic flow basics; virtual servers and pools; nodes and monitors | 18% |
| 2 | BIG IP Administration Data Plane Configuration | Profiles and policies; pool member settings; traffic handling configuration | 20% |
| 3 | BIG IP Administration Control Plane Administration | System settings; users and roles; device management basics | 18% |
| 4 | BIG IP Administration Support and Troubleshooting | Log review; common errors; basic diagnostics and issue isolation | 16% |
| 5 | BIG IP Administration Install Initial Configuration and Upgrade | Installation steps; initial setup; upgrade planning and validation | 28% |
The exam tests both foundational BIG-IP administration knowledge and the practical ability to apply it in real environments. Candidates should be ready to interpret core concepts, perform configuration tasks, support troubleshooting, and understand installation and upgrade workflows. A strong grasp of day-to-day administration and system behavior is important for success.
How QA4Exam.com Helps You Pass
QA4Exam.com provides Exam PDF material with actual questions and answers and an Online Practice Test that helps you prepare for the F5 Networks F5CAB1 exam efficiently. The practice test gives you a real exam simulation so you can get familiar with the question style, timing, and pressure before test day. With up-to-date questions and verified answers, you can focus on the most relevant content and reduce guesswork. It also helps you improve time management by practicing under exam-like conditions. These resources are designed to support first-attempt success with focused and practical preparation.
Frequently Asked Questions
1. What is the F5 Networks F5CAB1 exam about?
It is the BIG-IP Administration Install, Initial Configuration, and Upgrade exam for the F5 Certified Administrator, BIG-IP Certification. It focuses on core administration tasks for F5 BIG-IP environments.
2. Who should take the F5CAB1 exam?
It is suitable for candidates preparing for F5 BIG-IP administration roles and anyone who wants to validate skills in installation, configuration, upgrades, and troubleshooting.
3. Is the F5CAB1 exam difficult?
It can be challenging if you are not familiar with BIG-IP administration concepts and workflows. Candidates who study the exam topics and practice with realistic questions are better prepared.
4. Can I pass with only braindumps?
Braindumps alone are not the best approach. You should use them with exam preparation and hands-on understanding so you can answer questions confidently and apply the concepts correctly.
5. Do I need hands-on experience for F5CAB1?
Hands-on experience is very helpful because the exam covers practical BIG-IP administration tasks. Real usage of the platform improves understanding of concepts, configuration, and troubleshooting.
6. Are QA4Exam.com dumps and practice tests enough to prepare?
They are strong preparation tools because they provide actual questions and answers plus an online practice test format. Many candidates also review the exam topics carefully to strengthen understanding.
7. How do these materials help me pass on the first attempt?
They help you study the relevant questions, verify answers, and practice under exam-like timing. This builds confidence and improves your ability to manage the real test effectively.
8. What format do the QA4Exam.com materials use?
QA4Exam.com offers an Exam PDF with questions and answers and an Online Practice Test that simulates the exam experience. This combination supports both review and timed practice.
The questions for F5CAB1 were last updated on Sep 28, 2026.
- Viewing page 1 out of 10 pages.
- Viewing questions 1-5 out of 49 questions
How should a BIG-IP Administrator check the provisioned CPU percent for a module?
(Choose two.)
BIG-IP allocates CPU and memory resources based on module provisioning levels.
To view how much CPU a module is assigned, administrators must check provisioning information from:
C . GUI --- System Resource Provisioning
This page visually displays CPU allocation via color-coded bars.
Hovering over the CPU bar shows:
CPU usage percent per module
Which modules share CPU cycles
The system's total resource allocation
This is the primary GUI method.
D . tmsh show /sys provision
This command displays detailed module provisioning information including:
Provisioned modules
Their provisioning level
CPU and memory allocation data
It is the authoritative CLI method for resource provisioning status.
Why the other options are incorrect:
A . top
Shows real-time process usage, not provisioned CPU allocation.
B . tmsh show /sys cpu
Displays CPU runtime utilization, not per-module provisioning.
E . Statistics Dashboard
Only shows traffic / system runtime metrics, not provisioning resource allocations.
Therefore, C and D are correct.
What are the two options for securing a BIG-IP's management interface?
(Choose two.)
Securing the BIG-IP management interface is a fundamental administrative responsibility. F5 best practices emphasize restricting who can reach the management port and ensuring that only authorized systems are allowed access.
A . Limiting management access to trusted network segments
F5 recommends placing the management interface on a dedicated, isolated, and secured management network or VLAN, rather than exposing it to production or untrusted networks.
This reduces the attack surface by ensuring only trusted segments have visibility to administrative interfaces.
D . Restricting management access by IP or subnet
F5 BIG-IP uses the /sys httpd allow list (for HTTPS) and configuration options in sshd (for SSH) to control which IP addresses or subnets can access the device.
By specifying only known administrative IPs or ranges, unauthorized users cannot reach the login services.
Why the other options are incorrect
B . Blocking all management HTTPS/SSH ports
This would prevent any administrative access and is not a viable security practice.
C . Using Self-IP addresses for administrative access
F5 explicitly warns against using Self-IPs for management access unless strictly necessary.
Self-IPs are exposed to the data plane and should not be used as the primary administrative interface.
What will setting a Self IP to ''Allow None'' for Port Lockdown do?
The Port Lockdown feature controls which services a Self-IP will respond to.
Setting a Self-IP to Allow None means:
The Self-IP will not accept any traffic except the very limited, hard-coded HA ports such as TCP 4353 used for device trust and configuration sync.
All other HA ports, including those needed for network failover and other HA mechanisms, are blocked.
When essential HA services cannot communicate, each device assumes its peer is down.
This results in:
HA failover misbehavior
Both devices thinking the other is offline
Potential active-active condition, which is not intended and can cause traffic disruption
Thus, Allow None can break HA functionality unless the Self-IP is not used for HA links.
For security reasons, a BIG-IP Administrator needs to specify allowable IP ranges for access to the Configuration Utility (WebUI). The exhibit shows the User Administration section of the Configuration Utility.
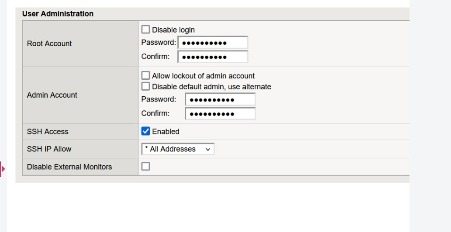
The administrator could not find any setting that explicitly restricts access to the Configuration Utility.
Which one of the following is a reason for that?
The screenshot shown is from the User Administration section of the BIG-IP GUI.
This section controls:
Root and Admin passwords
SSH Access
SSH IP Allow settings
However, it does not contain any controls for restricting access to the WebUI (TMUI).
BIG-IP does not provide TMUI access restrictions from this part of the GUI.
Access to the web-based Configuration Utility is controlled by the httpd allow list, configured through TMSH:
tmsh modify /sys httpd allow { <IP/subnet> }
This setting is not displayed in the User Administration panel, and in many BIG-IP versions, the httpd allow list is only configurable from the CLI, not the GUI.
Therefore, the administrator cannot find the setting in the screen shown because:
TMUI access restriction is not located in this GUI section
It must be configured using tmsh under /sys httpd allow
This is why Option A is correct.
A secondary administrator has been granted access to a BIG-IP device through its Management Interface, but is unable to access the Configuration Utility (WebUI).
What command can be run from the CLI to capture the network traffic on the management interface and troubleshoot the issue?
(Choose two.)
The BIG-IP has two distinct planes:
Management-plane handled entirely by the management interface (MGMT)
Data-plane (TMM) handles Self IPs, VLAN interfaces, and traffic processing
To capture traffic on the management interface, only the management-side NICs may be used:
mgmt Logical name for the management interface
eth0 Physical Linux interface mapped to the management port on most BIG-IP platforms
Both of these correctly capture inbound/outbound WebUI (HTTPS/443) traffic on the management port.
Why the correct answers are A and B
A . tcpdump -i eth0 -n port 443
On BIG-IP appliances and VMs, the management port maps to eth0 at the Linux OS level.
Capturing on eth0 correctly shows HTTPS traffic to the WebUI.
B . tcpdump -i mgmt -n port 443
mgmt is the BIG-IP alias for the management interface.
This is the preferred and most explicit capture interface for management-plane packet captures.
Why the other options are incorrect:
C . tcpdump -i 0.0
Interface 0.0 is the TMM switch interface used for data-plane packet captures.
It does NOT capture management-plane traffic.
D . tcpdump -i tun0
Used for tunnel interfaces (IPsec, VXLAN, etc.)
Not related to management access.
E . tcpdump -i management
There is no interface named management on BIG-IP.
The correct names are mgmt or eth0.
Unlock All Questions for F5 Networks F5CAB1 Exam
Full Exam Access, Actual Exam Questions, Validated Answers, Anytime Anywhere, No Download Limits, No Practice Limits
Get All 49 Questions & Answers