
Trusted Worldwide Questions & Answers
Fortinet FCP_FAZ_AN-7.6 Dumps - Pass Fortinet NSE 5 - FortiAnalyzer 7.6 Analyst Exam in 2026
The Fortinet FCP_FAZ_AN-7.6 exam, known as Fortinet NSE 5 - FortiAnalyzer 7.6 Analyst, is part of the Fortinet Certified Professional, FCP Fortinet Certified Professional Security Operations track. It is designed for security professionals who work with FortiAnalyzer and need to understand analysis, reporting, and operational workflows in a security operations environment. Earning this certification demonstrates practical knowledge that supports monitoring, investigation, and SOC efficiency.
| # | Exam Topics | Sub-Topics | Approximate Weightage (%) |
|---|---|---|---|
| 1 | Features and concepts | FortiAnalyzer roles, core components, data flow, logging and analysis concepts | 25% |
| 2 | Log Analysis | Log search, filtering, event review, correlation, investigation workflow | 30% |
| 3 | SOC operation and automation | Automation tasks, alert handling, SOC workflows, operational efficiency, response support | 25% |
| 4 | Reports | Report creation, report scheduling, templates, output review, report interpretation | 20% |
This exam tests how well candidates can apply FortiAnalyzer 7.6 knowledge in practical security operations tasks. It measures understanding of platform features, log analysis skills, SOC automation awareness, and reporting ability. Success requires more than memorization, since the questions are designed to reflect real working scenarios and operational decision-making.
How QA4Exam.com Helps You Pass
QA4Exam.com provides Exam PDF material with actual questions and answers, along with an Online Practice Test for the FCP_FAZ_AN-7.6 exam. These resources help you study with real exam simulation, so you can become familiar with the question style and pace before test day. The content is updated to stay aligned with the exam focus, and the verified answers help you review with confidence. Using the practice test also improves time management, which is important when you want to pass the Fortinet exam on your first attempt.
Frequently Asked Questions
1. Who should take the Fortinet FCP_FAZ_AN-7.6 exam?
This exam is for security professionals who want to validate their skills in FortiAnalyzer 7.6 as part of the Fortinet Certified Professional, FCP Fortinet Certified Professional Security Operations track.
2. Is the Fortinet NSE 5 - FortiAnalyzer 7.6 Analyst exam difficult?
It can be challenging because it covers features, log analysis, SOC operation and automation, and reports. Candidates who understand the platform and practice scenario-based questions usually feel more confident.
3. Can I pass with only braindumps?
Braindumps alone are not the best approach. You should combine exam questions and answers with proper review of the exam topics so you understand the concepts behind the answers.
4. Do I need hands-on experience with FortiAnalyzer?
Hands-on experience is very helpful because the exam focuses on practical knowledge of log analysis, SOC operations, and reporting tasks. Real-world familiarity makes the questions easier to understand.
5. Are the QA4Exam.com dumps and practice test enough to prepare for first attempt success?
They are a strong preparation tool because they include actual questions and answers, verified content, and exam-style practice. For best results, use them to review topics and test your readiness before the exam.
6. What format do QA4Exam.com products offer for FCP_FAZ_AN-7.6?
QA4Exam.com offers an Exam PDF and an Online Practice Test for the FCP_FAZ_AN-7.6 exam, giving you both study material and interactive practice in formats that support efficient preparation.
7. Will the practice test help with time management?
Yes, the Online Practice Test helps you get used to answering under time pressure, which improves pacing and reduces surprises on exam day.
The questions for FCP_FAZ_AN-7.6 were last updated on Sep 29, 2026.
- Viewing page 1 out of 16 pages.
- Viewing questions 1-5 out of 79 questions
Exhibit.
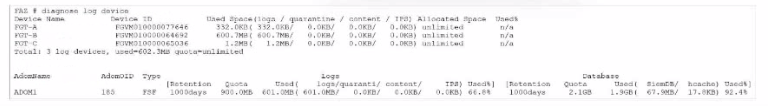
What can you conclude from this output?
Study Guide p.19-p.20: the Security Fabric root/upstream FortiGate relationship affects how traffic and UTM logs are correlated.
Technical Deep Dive: The correct answer is B. The output indicates FGT_B is acting as the Security Fabric root. In Security Fabric logging, FortiAnalyzer uses Fabric relationships to correlate logs and avoid duplicate traffic logging. The other options draw conclusions the output does not support: disk quota allocation to quarantine files, exact ADOM disk quota size, or archive-versus-analytics usage require explicit storage lines. The Fabric root conclusion is the one directly supported by the displayed Fabric relationship information.
What is the purpose of playbook trigger variables?
Study Guide p.211: trigger variables use information from the event or incident trigger in later playbook tasks.
Technical Deep Dive: The correct answer is B. Trigger variables allow a playbook task to reuse values from the event or incident that started the playbook, such as endpoint IP, device, severity, or incident fields. That allows a task to filter a report, get matching logs, or target a response action dynamically. Option A describes monitoring statistics, not variables. Option C reverses the relationship: the trigger starts the playbook, and the variables are then available to tasks. Option D is unrelated to ON_SCHEDULE timing.
Which statement regarding macros on FortiAnalyzer is true?
Study Guide p.173: macros represent dataset queries in abbreviated form, and macros are ADOM-specific.
Technical Deep Dive: The correct answer is C. FortiAnalyzer macros are not Excel-generation shortcuts and are not fixed templates. A macro is an abbreviated way to insert data extracted by a dataset query into a report without using a chart. Because reports, libraries, and related definitions are separated by ADOM, macros are ADOM-specific. Option A is wrong because custom macros can be created. Option B invents an Excel-specific behavior not described by the guide. Option D is too restrictive because macros are not limited only to FortiGate ADOMs.
Refer to the exhibit.
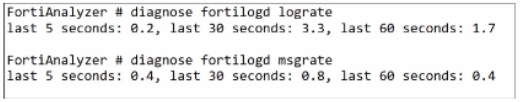
What can you conclude about the output?
Study Guide p.139: one compressed log message can contain multiple logs; message/log rate differences should be interpreted carefully.
Technical Deep Dive: The correct answer is C. If the exhibit shows message rate higher than log rate, that is not the normal relationship highlighted in the guide. FortiAnalyzer explains the normal case where one log message can contain multiple logs, making log rate higher than message rate. Options A and B cannot be concluded without indexing-completion or log-type breakdown information. Option D is wrong because these fortilogd rate outputs are not ADOM-specific unless a specific ADOM-scoped command is used.
In firmware version 7.6, how does on-premises FortiAnalyzer store logs? (Choose one answer)
Official Fortinet 7.6 documentation: historical logs migrate from PSQL to ClickHouse, and real-time logs insert into ClickHouse.
Technical Deep Dive: The correct answer is A. FortiAnalyzer 7.6 uses ClickHouse as the backend log database for on-premises log analytics. This change supports faster analytical queries and scalable handling of large log datasets. MySQL and Elasticsearch are not the FortiAnalyzer 7.6 log database. PostgreSQL was used in previous versions for log tables, but Fortinet's 7.6 documentation states that historical logs are migrated from PSQL to ClickHouse and new real-time logs are inserted into ClickHouse.
Unlock All Questions for Fortinet FCP_FAZ_AN-7.6 Exam
Full Exam Access, Actual Exam Questions, Validated Answers, Anytime Anywhere, No Download Limits, No Practice Limits
Get All 79 Questions & Answers