
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

Free FCP_FSA_AD-5.0 Exam Dumps and Practice Questions

Questions 1 to 5 of the 42-question FCP_FSA_AD-5.0 bank, each with its correct answer and an explanation. 2 of 5 ask for more than one answer. This is page 1 of 8.

1 / 8

Actual Fortinet FCP_FSA_AD-5.0 Exam Questions

Question 1

Single answer

Which stage of the Cyber Kill Chain does FortiSandbox and FortiClient EMS integration help to block? (Choose one answer)

Correct answer: A

From the FortiClient EMS Integration lesson, the Study Guide states that FortiSandbox and FortiClient EMS integration helps break the kill chain by monitoring all downloads, removable media, mapped network drives, and email client file downloads --- intercepting threats at the Delivery stage before they can execute on the endpoint.

Additionally, from the Attack Methodologies section: 'When a USB is attached to a host protected with FortiClient, FortiClient can send the files on the USB drive to FortiSandbox for analysis, before allowing the user access to the files' --- further confirming the Delivery stage focus.

Question 2

Multiple answers

You are asked to create some custom VMs to better represent your security environment. In which two FortiSandbox deployments is this supported? (Choose two answers)

Correct answer: A, C

From the Scanning and Rating Components lesson, the Study Guide explicitly states:

'FortiSandbox allows you to modify the number of CPUs and memory assigned to a custom VM. This feature is supported on hardware models and private cloud VMs.'

Hardware models = Device-based (Option C)

Private cloud VMs = Private cloud (Option A)

Azure non-nested mode and FortiSandbox Cloud do not support custom VM creation as per the Study Guide.


Question 3

Multiple answers

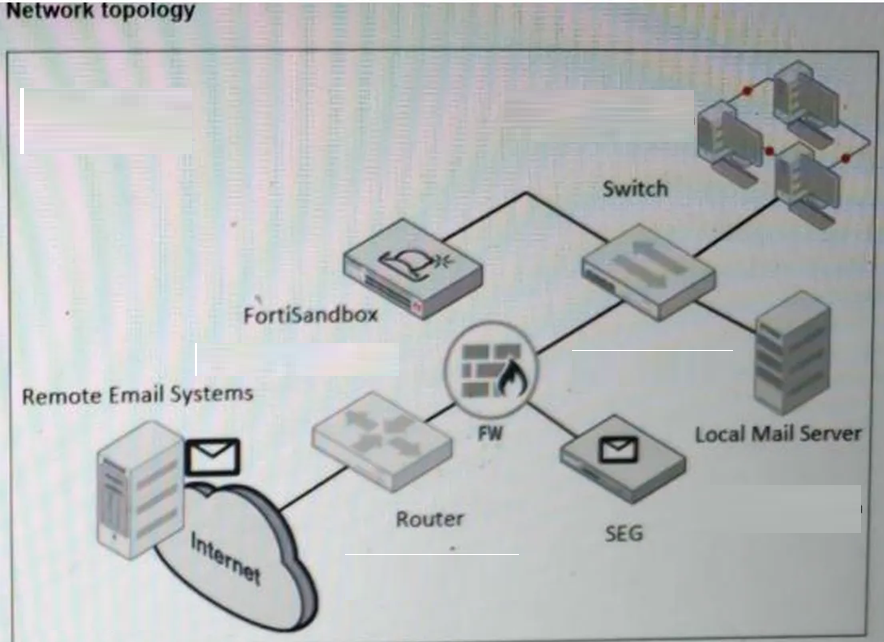
Refer to the exhibit.

A network topology is shown. Which two important steps must you take before you enable a BCC adapter on FortiSandbox? (Choose two answers)

Correct answer: C, D

From the Deployment and System Settings lesson, the Study Guide states:

'You can submit emails from an upstream MTA server to FortiSandbox using a BCC adapter. FortiSandbox will extract attachment files and URLs in an email body.'

For a BCC adapter to function correctly, two critical prerequisites must be in place:

Option C --- The upstream SEG must be configured to BCC emails to a FortiSandbox sub-domain so that email copies are routed to FortiSandbox for analysis

Option D --- An MX record must be added to the DNS server for the BCC email sub-domain, so that the sub-domain resolves to the FortiSandbox IP address, allowing the SEG to properly deliver BCC email copies

Option A is incorrect because the BCC adapter handles full email inspection --- FortiSandbox itself extracts files and URLs rather than the SEG doing this. Option B is incorrect because an MX record (not just an A record) is the required DNS configuration for email routing.


Question 4

Single answer

How can you limit an administrator's access to scan jobs on FortiSandbox based on the system that submitted the scan request? (Choose one answer)

Correct answer: D

The correct answer is D. The Study Guide states that FortiSandbox has default administrative profiles and specifically says: ''The Read Only profile is intended to be used for system-wide monitoring and reporting tasks, whereas the Device profile is intended to be used for monitoring alerts and reporting for a specific device.'' That wording directly matches the question requirement to limit access based on the system that submitted the scan request. In other words, FortiSandbox uses administrator profiles to control whether an admin can view broad system-wide activity or only jobs and alerts related to a specific submitting device.

This eliminates the other options. The Study Guide does not describe device groups, log server settings, or netshare groups as the mechanism for restricting admin visibility of scan jobs by submitter. Instead, access control is tied to the admin profile model. The Device profile is the exact fit because it narrows monitoring and reporting to a particular device context rather than the entire system. Therefore, the way to limit an administrator's access to scan jobs by the submitting system is by configuring administrator profiles that define job access.


Question 5

Single answer

You are troubleshooting long delays between FortiMail file submissions to FortiSandbox and verdicts being returned form FortiSandbox. Which FortiMail debug tool must you use to troubleshoot this issue further? (Choose one answer)

Correct answer: B

The FortiSandbox 5.0 Administrator Lab Guide shows that, when diagnosing FortiMail submission issues, the required FortiMail debugs are sandboxclid and deferd. It explicitly instructs: ''Enter the following commands to enable both deferd and sandboxclid debugging'' and then shows that the deferd daemon spools the email and later releases the email from the queue folder after FortiSandbox processing.

Because sandboxclid is not one of the answer choices, the best answer among the listed FortiMail debug tools is deferd. It is the FortiMail daemon directly shown in the official lab workflow for troubleshooting submission-and-verdict handling. The other options in the answer list are not the ones the lab uses for FortiMail-to-FortiSandbox submission troubleshooting. So, based on the uploaded guide, diagnose debug application deferd is the correct choice.


Unlock all Fortinet FCP_FSA_AD-5.0 questions

Full exam access, validated answers, and unlimited practice with no download limits.