
Trusted Worldwide Questions & Answers
Fortinet FCSS_NST_SE-7.6 Dumps - Pass Fortinet NSE 6 - Network Security 7.6 Support Engineer Exam in First Attempt 2026
The Fortinet FCSS_NST_SE-7.6 exam, also known as Fortinet NSE 6 - Network Security 7.6 Support Engineer, belongs to the Fortinet Certified Solution Specialist,FCSS Fortinet Certified Solution Specialist Network Security track. It is designed for professionals who support and troubleshoot Fortinet network security deployments in real-world environments. This certification matters because it validates practical knowledge in core support areas that are essential for maintaining secure and reliable network operations.
Candidates preparing for this exam should be comfortable with troubleshooting, authentication, security profiles, routing, and VPN-related tasks. The exam is important for those who want to prove they can solve common Fortinet security issues efficiently and accurately.
Exam Topics and Approximate Weightage
| # | Exam Topics | Sub-Topics | Approximate Weightage (%) |
|---|---|---|---|
| 1 | System troubleshooting | Device status checks, log analysis, connectivity issues, policy behavior validation | 30% |
| 2 | Authentication | Login methods, user verification, authentication failures, access control troubleshooting | 18% |
| 3 | Security profiles | Profile application, inspection behavior, policy effects, content filtering issues | 20% |
| 4 | Routing | Route verification, path selection, gateway issues, traffic flow troubleshooting | 17% |
| 5 | VPN | Tunnel status, phase negotiation, connectivity checks, remote access troubleshooting | 15% |
This exam tests how well you can apply practical support knowledge under real troubleshooting conditions. It focuses on identifying issues, interpreting symptoms, and choosing the right corrective action across the listed Fortinet technologies. Strong hands-on understanding is important because the questions are aligned with operational problem solving, not just memorization.
How QA4Exam.com Helps You Pass
QA4Exam.com offers Exam PDF materials with actual questions and answers, along with an Online Practice Test designed for the Fortinet FCSS_NST_SE-7.6 exam. These resources help you study with up-to-date questions, verified answers, and a format that mirrors the real exam experience. The practice test gives you valuable time management practice so you can build speed and confidence before exam day. By reviewing realistic exam content and testing yourself in a simulation environment, you can prepare more effectively and improve your chances of passing on the first attempt. If you want focused preparation for Fortinet NSE 6 - Network Security 7.6 Support Engineer, QA4Exam.com gives you a practical path to readiness.
Frequently Asked Questions
What is the Fortinet FCSS_NST_SE-7.6 exam?
It is the Fortinet NSE 6 - Network Security 7.6 Support Engineer exam, part of the Fortinet Certified Solution Specialist,FCSS Fortinet Certified Solution Specialist Network Security certification track.
Who should take this exam?
It is intended for professionals who support and troubleshoot Fortinet network security deployments and want to validate practical support skills.
Is the Fortinet FCSS_NST_SE-7.6 exam difficult?
It can be challenging because it focuses on practical troubleshooting across system issues, authentication, security profiles, routing, and VPN topics.
Can I pass with only braindumps?
Braindumps alone are not the best approach. You should combine them with review and hands-on understanding so you can answer scenario-based questions more confidently.
Do I need hands-on experience to pass?
Hands-on experience is very helpful because the exam tests practical support and troubleshooting ability, not just definitions or theory.
How can QA4Exam.com help me pass on the first attempt?
The Exam PDF and Online Practice Test help you study with actual questions and answers, verified content, realistic simulation, and time management practice for first-attempt readiness.
What format do the QA4Exam.com dumps and practice test use?
QA4Exam.com provides an Exam PDF and an Online Practice Test so you can review the material in a study-friendly format and practice in a test-like environment.
The questions for FCSS_NST_SE-7.6 were last updated on Sep 29, 2026.
- Viewing page 1 out of 27 pages.
- Viewing questions 1-5 out of 134 questions
Which three common FortiGate-to-collector-agent connectivity issues can you identify using the FSSO real-time debug? (Choose three.)
The diagnose debug authd fsso server command is the primary tool for troubleshooting communication between the FortiGate and the FSSO Collector Agent. This debug output reveals the status of the connection and the reasons for failure. The three most common connectivity issues identified by this debug are:
FortiGate cannot reach the IP address of the collector agent (Option C): The debug will show connection timeouts or 'host unreachable' errors if the Layer 3 connectivity is missing.
The connection was refused / Port mismatch (Option B): If the FortiGate can reach the IP but the Collector Agent is not listening on the specified port (default 8000), the debug will display 'Connection refused.' This often happens if the port configured on the FortiGate does not match the listening port on the agent.
The pre-shared key does not match (Option D): If the IP and Port are correct, the next step is authentication. If the password configured on the FortiGate does not match the one on the Collector Agent, the debug will explicitly show an 'Authentication failed' or 'password mismatch' error during the handshake.
Note on other options: Option A (SSL) is less common than basic connectivity/auth mismatches. Option E (Group filters) relates to user processing logic, which occurs after connectivity is established.
FortiGate Security 7.6 Study Guide (FSSO Troubleshooting): 'Troubleshooting FSSO... Check connectivity (IP/Port) and authentication (Password).'
Refer to the exhibits,
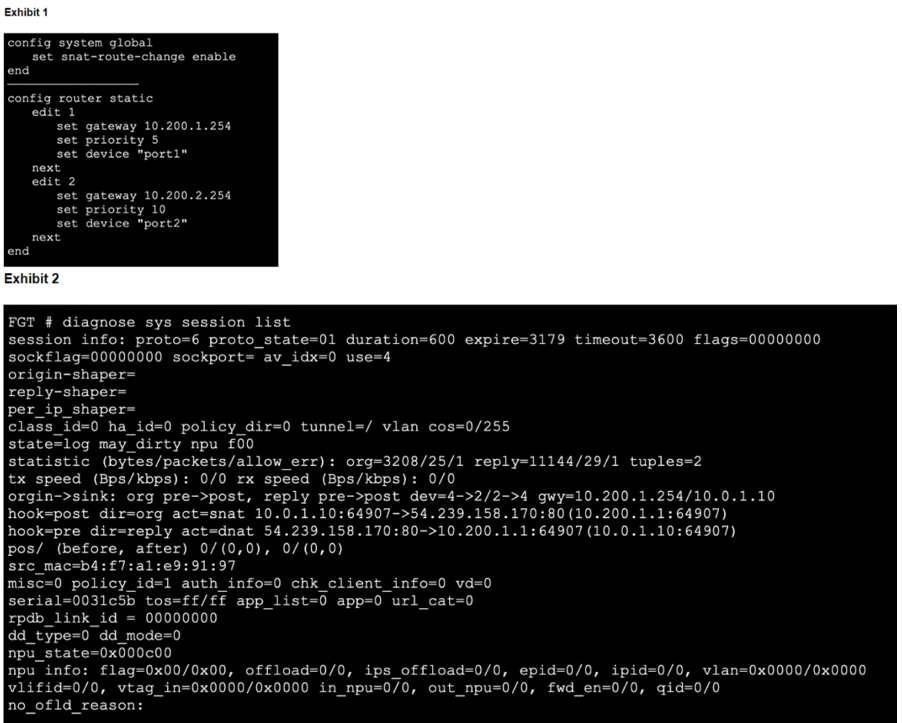
which show the configuration on FortiGate and partial session information for internet traffic from a user on the internal network. If the priority on route ID 2 were changed from 10 to 0, what would happen to traffic matching that user session? (Choose one answer)
The correct answer is A. This behavior is dictated by the configuration command set snat-route-change enable shown in Exhibit 1 under config system global.
Routing Change: By changing the priority of route ID 2 from 10 to 0, it becomes lower than route ID 1 (priority 5). In FortiOS, a lower priority value indicates a more preferred route. Consequently, the active route for the destination changes from port1 to port2.
SNAT Implication: The existing session (shown in Exhibit 2) is using Source NAT (SNAT) with the IP address associated with port1 (10.200.1.1). If the traffic were simply switched to port2, the source IP would be incorrect for that interface and the return traffic would likely fail or be dropped.
snat-route-change enable: This specific setting instructs the FortiGate on how to handle established SNAT sessions when a routing change occurs that alters the preferred outgoing interface. When enabled, if a route change forces an SNAT session to a new interface, FortiGate flushes (deletes) the session from the session table. This is necessary because a live TCP session cannot survive a change in its source IP address. The client must initiate a new session, which will then be created using the new correct route (port2) and the corresponding new SNAT IP.
If this setting were disabled, the session would likely remain 'sticky' to the original interface (port1) until it closed, provided the route still existed. However, the explicit configuration forces the deletion.
What are two reasons you might see iprope_in_check() check failed, drop when using the debug flow? (Choose two.)
The Network Security Support Engineer 7.6 Study Guide explicitly explains this debug message:
''iprope_in_check() check failed, drop'' means the packet is destined to a FortiGate IP address and one of these conditions applies:
The service is not enabled
The service is using a different TCP port
The source IP address is not included in the trusted host list
The packet matches a local-in policy with action deny
That directly confirms C. Trusted host list misconfiguration.
Why D is the second valid choice: The FortiOS administration guide explains that:
''IP pools and VIPs are considered local IP addresses if responding to ARP requests on these external IP addresses is enabled ... the FortiGate is considered a destination for those IP addresses ... once an IP pool or VIP has been configured ... the FortiGate considers it as a local address and will not forward traffic based on the routing table.''
Because iprope_in_check() is a local-in/local-destination type failure, a VIP or IP pool misconfiguration can cause traffic to be treated as destined for the FortiGate itself, which can then trigger this drop condition if the matching local service/local-in handling is not valid. So D is the closest supported second answer from the available choices.
Why the other options are wrong:
A is wrong because policy route problems are not the documented meaning of this specific debug message. The study guide instead ties iprope_in_check() check failed, drop to management/local-in conditions.
B is wrong because the study guide says traffic shaping drops appear as: ''Denied by quota check''
Which two statements are true regarding heartbeat messages sent from an FSSO collector agent to FortiGate? (Choose two.)
According to the official Fortinet documentation (Technical Tip: Useful FSSO Commands), heartbeat messages play a crucial role in communication between the FSSO Collector Agent and FortiGate. These messages are regularly sent from the Collector Agent to verify its status, maintain session awareness, and confirm connectivity between the authentication infrastructure and FortiGate appliances.
Option B is confirmed by Fortinet, as the collector agent logs on Windows or its management console will specifically note heartbeat events, connection status, and any issues maintaining contact with FortiGate units.
Option C is validated by both official CLI documentation and the technical tip linked. On FortiGate, heartbeat messages from the collector agent are visible using real-time debug tools such asdiagnose debug application authdor FSSO-specific commands. These enable administrators to monitor live logon states, session status, and connection health directly from the FortiGate CLI. The debug stream shows heartbeats received and their effect on active logons, associating health monitoring with active sessions.
Heartbeat operation is fully automated once FSSO is set up---there is no requirement for manual enablement or configuration, aligning with Fortinet's philosophy of seamless integration and centralized management across the Security Fabric. This ensures that both FortiGate and the collector agent can quickly and reliably detect any miscommunication or outage, addressing authentication issues proactively.
References:
Technical Tip: Useful FSSO Commands (Fortinet Community)
FortiOS Administration Guide: FSSO, Collector Agent, Heartbeat, CLI Debug
Refer to the exhibit, which shows the output of a real-time debug. Which statement about this output is true? (Choose one answer)
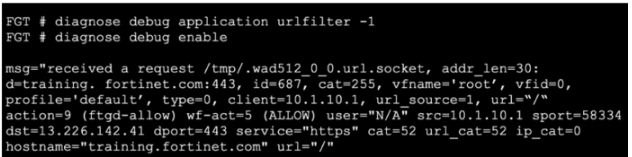
The correct answer is A.
The debug output is for an HTTPS request and shows a hostname value. The study guide explains that with SSL certificate inspection, FortiGate extracts the FQDN from either:
''TLS extension server name indication (SNI)''
''SSL certificate common name (CN)''
So the hostname shown in the real-time web-filter debug can be derived from the SNI in the client request or, if needed, from the CN in the server certificate. That makes A correct.
Why the other options are wrong:
B is wrong because the study-guide example for web-filter real-time debug explicitly says: ''This slide shows an example of real-time debug output when the URL to categorize isn't in the FortiGuard cache.''
In these debugs, cat=255 appears before the final lookup result, so this does not indicate a local-cache hit.
C is wrong because ftgd-allow is the action, not the profile name. The debug line shows the action as action=9 (ftgd-allow) while the profile shown is profile='default'. FortiOS web-filter logs also use the profile field separately from the action field
D is wrong because the final category shown is url_cat=52, not 255. The study guide's example shows the same pattern: an initial cat=255 in the request line, followed by the resolved result cat=52 url_cat=52
So the verified answer is: A.
Unlock All Questions for Fortinet FCSS_NST_SE-7.6 Exam
Full Exam Access, Actual Exam Questions, Validated Answers, Anytime Anywhere, No Download Limits, No Practice Limits
Get All 134 Questions & Answers