Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

NSE4_FGT_AD-7.6 Exam Dumps and Practice Questions

Questions 1 to 5 of the 93-question NSE4_FGT_AD-7.6 bank, each with its correct answer and an explanation. 1 of 5 ask for more than one answer. This is page 1 of 19.

1 / 19

Actual Fortinet NSE4_FGT_AD-7.6 Exam Questions

Question 1

Which statement correctly describes NetAPI polling mode for the FSSO collector agent?

Correct answer: B

NetAPI: Polls temporary sessions created on the DC when a user logs on or logs off and calls the NetSessionEnum function on Windows. It's faster than the WinSec and WMI methods; however, it can miss some logon events if a DC is under heavy system load. This is because sessions can be quickly created and purged form RAM, before the agent has a chance to poll and notify FG.


Question 2

Refer to the exhibit

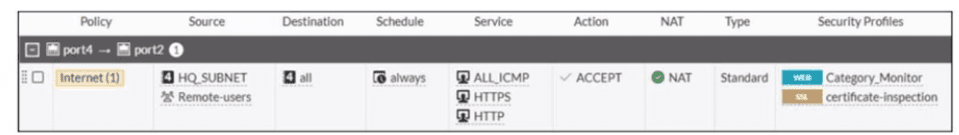
A firewall policy to enable active authentication is shown.

When attempting to access an external website using an active authentication method, the user is not presented with a login prompt. What is the most likely reason for this situation?

Correct answer: D

Based on the exhibit and FortiOS 7.6 Active Authentication (captive portal) behavior, the most likely reason the user is not presented with a login prompt is that DNS is missing from the firewall policy.

What the exhibit shows

The firewall policy configured for active authentication includes:

Source: HQ_SUBNET and Remote-users

Destination: all

Services:

HTTP

HTTPS

ALL_ICMP

Security Profiles: Web filter and SSL inspection enabled

Authentication: Active (user group referenced)

DNS is not included as a service in the policy.

Why DNS is required for active authentication

In FortiOS 7.6, active authentication (captive portal) works as follows:

The user attempts to access a website using a URL (for example, www.example.com).

The client must first perform a DNS lookup to resolve the domain name.

FortiGate intercepts the initial HTTP/HTTPS request and redirects the user to the authentication portal.

If DNS traffic is blocked or not allowed:

The hostname cannot be resolved.

The HTTP/HTTPS request never properly occurs.

FortiGate has nothing to intercept, so the login prompt is never triggered.

This is explicitly documented in the FortiOS 7.6 Authentication and Captive Portal requirements, which state that DNS must be permitted for captive portal--based authentication to function correctly.

Why the other options are incorrect

A . No matching user account exists for this user

Incorrect.

If the user account did not exist, the login page would still appear, but authentication would fail after credentials are entered.

B . The Remote-users group must be set up correctly in the FSSO configuration

Incorrect.

This policy is using active authentication, not FSSO.

FSSO configuration is irrelevant for active authentication login prompts.

C . The Remote-users group is not added to the Destination

Incorrect.

User groups are applied in the Source field for authentication-based policies.

Destination does not accept user groups.


Question 3

Refer to the exhibit.

As an administrator you have created an IPS profile, but it is not performing as expected. While testing you got the output as shown in the exhibit What could be the possible reason of the diagnose output shown in the exhibit?

Correct answer: A

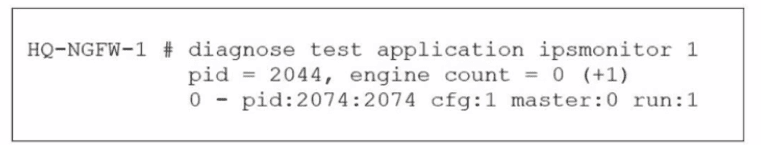
The exhibit shows the output of the following command:

diagnose test application ipsmonitor 1

pid = 2044, engine count = 0 (+1)

0 - pid:2074:2074 cfg:1 master:0 run:1

How to interpret this output (FortiOS 7.6 -- IPS internals)

ipsmonitor displays the status of IPS engines running on the FortiGate.

engine count = 0 means:

No IPS scanning engines are currently active

IPS is not processing any traffic

In FortiOS, IPS engines are started on demand.

Critical documented behavior

IPS processes are only spawned when at least one firewall policy is configured with an IPS profile and traffic matches that policy.

If no firewall policy references an IPS profile, the IPS engine:

Does not start

Shows engine count = 0

Appears ''not working,'' even though the IPS profile exists

This is exactly what the diagnose output indicates.

Why option A is correct

A . There is no firewall policy configured with an IPS security profile.

Creating an IPS profile alone is not sufficient

IPS must be applied to an active firewall policy

Traffic must match that policy for the IPS engine to run

Otherwise, ipsmonitor will show engine count = 0

This matches FortiOS 7.6 IPS operational behavior.

Why the other options are incorrect

B . Administrator entered the command diagnose test application ipsmonitor 5.

Incorrect.

The exhibit clearly shows ipsmonitor 1

Using a different argument would not explain engine count = 0

C . FortiGate entered into IPS fail open state.

Incorrect.

In fail-open, IPS engines may be bypassed, but they still initialize

engine count = 0 specifically indicates IPS is not in use at all

D . Administrator entered the command diagnose test application ipsmonitor 99.

Incorrect.

The command argument affects debug level, not engine creation

Again, the exhibit shows ipsmonitor 1


Question 4

A network administrator is reviewing firewall policies in both Interface Pair View and By Sequence View. The policies appear in a different order in each view. Why is the policy order different in these two views?

Correct answer: C

In FortiOS 7.6, firewall policies can be displayed in multiple views to help administrators understand and manage rules more effectively. The difference in ordering between Interface Pair View and By Sequence View is intentional and documented.

Why the policy order is different

Interface Pair View

Groups firewall policies based on the incoming (From) and outgoing (To) interfaces.

Policies are organized under interface pairs such as:

LAN WAN

WAN LAN

Within each interface pair, policies may appear reordered compared to the global list.

This view is designed for readability and troubleshooting, not to show execution order.

By Sequence View

Displays firewall policies in their actual evaluation (processing) order.

This is the top-down order FortiGate uses when matching traffic.

It reflects the real rule sequence that determines which policy is hit first.

Why option C is correct

C . Interface Pair View sorts policies based on matching interfaces, while By Sequence View shows the actual processing order of rules.

This statement exactly matches FortiOS behavior as documented in the FortiOS 7.6 Firewall Policy Views section of the Administrator Guide.

Why the other options are incorrect

A: Interface Pair View does not follow traffic logs, and By Sequence View is not based on ''rule priority'' grouping.

B: FortiGate does not dynamically reorder policies based on traffic patterns.

D: Security levels do not affect policy ordering in Interface Pair View.


Question 5

Refer to the exhibit.

Which two statements about the FortiGuard connection are true? (Choose two.)

Correct answer: A, D

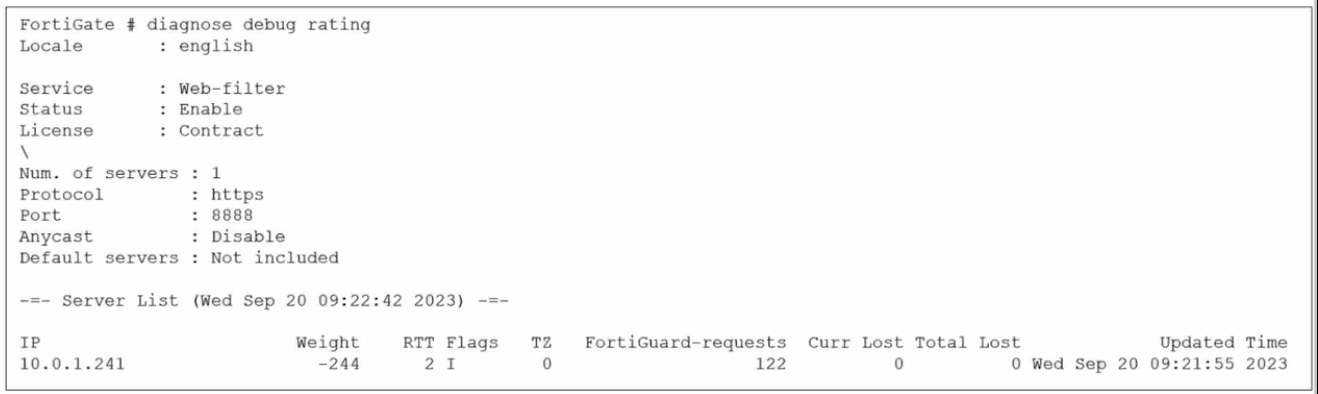
Based on the diagnose debug rating output provided in the exhibit and the standard behavior of the FortiGuard connection mechanism in FortiOS 7.6:

Weight Calculation (Statement A is True):

In FortiOS, the rating server selection process uses a weight-based system.

According to official documentation, the weight increases with failed packets (lost responses) and decreases with successful packets.

This mechanism ensures that servers with poor reliability are penalized by having higher weights, effectively pushing them to the bottom of the preference list.

Default Port Communication (Statement D is True):

The exhibit explicitly shows the communication is using HTTPS on port 8888.

In FortiOS 7.6 (and legacy versions like 6.2/6.4), FortiGuard filtering supports specific protocols and ports: HTTPS on ports 443, 53, and 8888, where 8888 is considered a default port for FortiGuard queries.

Ports 53 and 8888 are standard for both UDP and TCP/HTTPS FortiGuard communications to avoid common firewall blocks on standard web ports.

Why other options are incorrect:

Statement B (Unreliable protocols): While you can configure UDP (which is unreliable), the exhibit specifically shows HTTPS is being used, which is a reliable (TCP-based) protocol.

Statement C (DNS lookup): In the 'Flags' column of the server list, a server found via DNS lookup would be marked with the 'D' flag. The exhibit shows the flag as 'I' (indicating the last INIT request was sent to this server) and a numeric '2,' but the 'D' flag is absent. Additionally, the IP 10.0.1.241 is a private address, suggesting it is a manually configured FortiManager or local override server rather than a public server found via global DNS lookup.


Unlock all Fortinet NSE4_FGT_AD-7.6 questions

Full exam access, validated answers, and unlimited practice with no download limits.