
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

NSE5_FSW_AD-7.6 Exam Dumps and Practice Questions

Preview page 1 of 23 with real questions 1 to 5 from the full 114-question Fortinet set.

Fortinet NSE5_FSW_AD-7.6 Dumps - Pass Fortinet NSE 5 - FortiSwitch 7.6 Administrator Exam in 2026

The Fortinet NSE5_FSW_AD-7.6 exam, also known as Fortinet NSE 5 - FortiSwitch 7.6 Administrator, is part of the Fortinet Certified Professional, FCP Fortinet Certified Professional Secure Networking certification path. It is designed for network professionals who manage and support FortiSwitch environments and want to validate their administrative skills. This exam matters because it confirms your ability to work with FortiSwitch concepts, deployment, security, and troubleshooting in real-world networks.

# Exam Topics Sub-Topics Approximate Weightage (%)
1 FortiSwitch concepts
  • FortiSwitch architecture and roles
  • Switching fundamentals and features
  • FortiLink overview
25%
2 Deployment and management
  • Initial deployment steps
  • Device discovery and registration
  • Configuration and management tasks
30%
3 Layer 2 control and security
  • VLAN handling and segmentation
  • Spanning Tree and loop protection
  • Access control and security settings
25%
4 Monitoring and troubleshooting
  • Status and health monitoring
  • Event and log analysis
  • Common connectivity troubleshooting
20%

This exam tests both conceptual knowledge and practical administration skills for FortiSwitch 7.6 environments. Candidates need to understand how FortiSwitch works, how to deploy and manage it, how to apply Layer 2 controls and security, and how to monitor and troubleshoot issues effectively. The focus is on real-world readiness, not just memorization.

Actual Fortinet NSE5_FSW_AD-7.6 Exam Questions

Question 1

Refer to the exhibit.
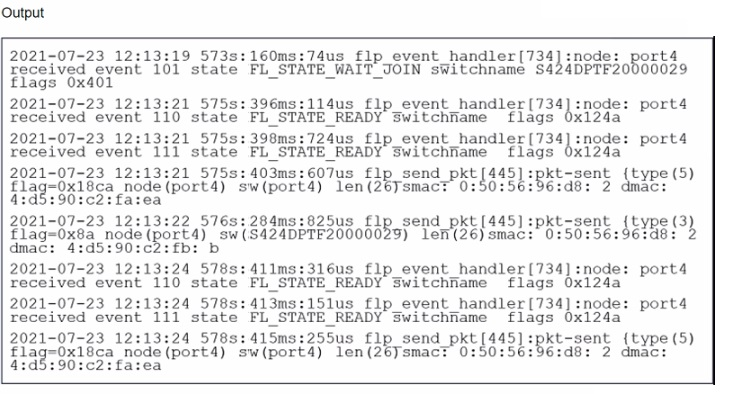
Which two statements best describe what is displayed in the FortiLink debug output shown in the exhibit? (Choose two.)

Correct answer: A, B

The provided debug output indicates that the FortiSwitch is sending FortiLink heartbeats to the FortiGate and is currently waiting to join the stack group. Here's a breakdown of the relevant lines:

Line 1:Shows the date, time, elapsed time since boot, and process ID for the FortiLink event handler.

573s:160ms: 74ustranslates to roughly 573 seconds, 160 milliseconds, and 74 microseconds since uptime.

Event 101:This indicates the FortiSwitch is in a 'wait join' state (FL_STATE_WAIT_JOIN). This means it's discovered by the FortiGate and is awaiting further instructions to join the FortiLink stack group.

switchname S424DPTF20000029:This displays the serial number of the FortiSwitch.

flags 0x401:The specific flag meaning might depend on the FortiSwitch model and version, but it likely indicates general communication between the switch and FortiGate.

Lines 2 and onward:These lines show subsequent events with similar timestamps, suggesting a regular heartbeat interval. There are also instances of the FortiSwitch sending packets to the FortiGate (indicated bypkt-sent).

Why the Other Options Are Less Likely:

C . FortiSwitch is discovered and authorized by FortiGate.While discovery might have happened before these lines, the 'wait join' state suggests authorization hasn't necessarily completed yet.

D . FortiSwitch is ready to push its new hostname to FortiGate.There's no explicit indication of hostname changes in this excerpt.The focus is on joining the stack group.

In Summary:

The key point is the 'FL_STATE_WAIT_JOIN' state, which signifies the FortiSwitch is ready to be fully integrated but is waiting for further commands from the FortiGate to complete the process.
Question 2

Refer to the exhibits

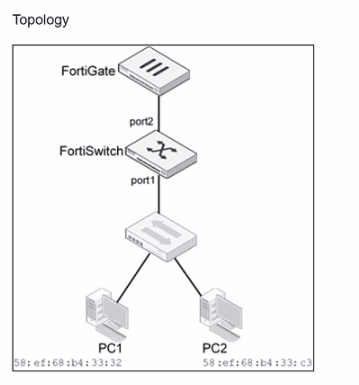
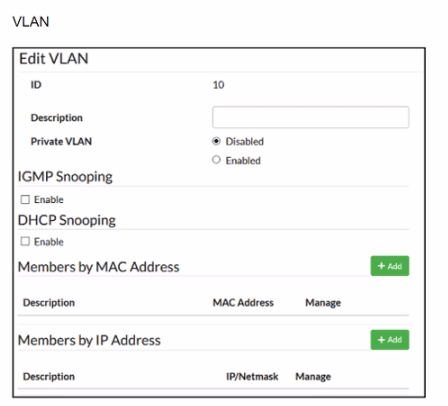
Traffic arriving on port2 on FortiSwitch is tagged with VLAN ID 10 and destined for PC1 connected on port1. PC1 expects to receive traffic untagged from port1 on FortiSwitch. Which two configurations can you perform on FortiSwitch to ensure PC1 receives untagged traffic on port1? (Choose two.)

Correct answer: B, C

According to theFortiSwitchOS 7.6 Administration Guideand theFortiSwitch 7.6 Study Guide, the way a FortiSwitch handles VLAN tags on egress (outgoing) traffic is governed by the port'sNative VLANand itsUntagged VLAN list. When traffic for VLAN 10 arrives at port2 (the uplink) and is forwarded to port1, the switch must determine whether to strip the 802.1Q tag before transmission.

Untagged VLAN List (Option B):The documentation explicitly states that the 'untagged VLAN list' specifies VLANs for which the port will transmit frameswithout the VLAN tag. By adding VLAN ID 10 to the untagged VLANs on port1, any traffic belonging to VLAN 10 will have its tag stripped at the egress point, ensuring PC1 receives a standard untagged frame.

Configuration Logic (Option C):In FortiSwitch management, moving a VLAN from the 'Allowed' list (which typically implies tagged delivery) to the 'Untagged' list on a specific interface forces the switch to perform the tag-stripping action. This effectively converts the port from a trunked behavior for that VLAN to an 'access' or untagged behavior.

Regarding the incorrect options:Option A (MAC-based assignment)is used primarily foringress classification. While it can assign a device to a VLAN when it sends trafficintothe switch, the documentation notes that by default, egress packets for MAC-based VLANs still include the tag unless the untagged list is configured.Option D(Private VLANs) is a security feature for isolating traffic between ports within the same VLAN and does not address the physical tagging requirements of the endpoint.


Question 3

FortiGate is unable to establish a tunnel with the FortiSwitch device it is supposed to manage Based on the debug output shown in the exhibit, what is the reason for the failure?

Correct answer: C

The issue described pertains to the establishment of a tunnel (likely a CAPWAP tunnel for management purposes between FortiGate and FortiSwitch).Based on typical error analysis in tunnel setup scenarios:

The CAPWAP tunnel failed to come up due to a mismatch in time (Option C): This answer is plausible because time synchronization is crucial for security protocols that underpin tunnel establishments, such as DTLS (Datagram Transport Layer Security) used within CAPWAP tunnels. If the clocks on FortiGate and FortiSwitch are significantly out of sync, the security handshake (which can include timestamp validation) could fail, preventing the tunnel from coming up.


Fortinet's technical documentation typically outlines the importance of time synchronization for secure communications. In CAPWAP/DLTS scenarios, precise time matching is crucial to ensure that the cryptographic parameters align correctly during the handshake process.

Question 4

(Full question statement start from here)

When you change FortiSwitch management mode fromstandalonetomanaged, what happens to the existing standalone configuration? (Choose one answer)

Correct answer: C

When a FortiSwitch is converted fromstandalone (local) management modetoFortiGate-managed mode using FortiLink, FortiSwitchOS follows a well-defined and protective transition process. According to the FortiSwitchOS 7.6 Administrator Guide, the switchdoes not mergeits existing standalone configuration with FortiLink-managed settings, nor does FortiGate import or preserve the active configuration for reuse.

Instead, when the management mode change occurs, the FortiSwitchsaves the current standalone configuration internallyand thenresets its operational configuration to the default FortiLink configuration. This default configuration is required so the switch can correctly establish FortiLink control-plane communication with the FortiGate, including CAPWAP-based management, VLAN 4094 usage, and dynamic policy provisioning.

Once the FortiSwitch is under FortiGate management,all configuration is controlled centrally by the FortiGate, including VLANs, port policies, security features, and firmware management. The previously saved standalone configuration is retained only as a backup reference on the switch and isnot actively usedunless the switch is later reverted back to standalone mode.

This behavior ensures configuration consistency, prevents conflicts between local and centralized policies, and aligns the switch with the FortiGate-centricSecurity Fabric architecture. It also avoids unpredictable results that could occur if legacy standalone settings were merged with FortiLink-managed profiles.

The other options are incorrect because FortiSwitch does not register with FortiSwitch Cloud automatically, does not merge configurations, and FortiGate does not back up the standalone configuration during onboarding.

Therefore, the correct and fully documented answer isC. FortiSwitch saves the standalone configuration and changes to the default FortiLink configuration.


Question 5

How is traffic routed on FortiSwitch?

Correct answer: D

Layer 3 routing can be configured on FortiSwitch, while managed by FortiGate (D): FortiSwitch, when managed by FortiGate, supports Layer 3 routing capabilities. This allows for routing between VLANs directly on the switch, enhancing network efficiency by reducing the need to pass traffic through higher network layers for inter-VLAN communication. This configuration enables more sophisticated network setups and efficient routing directly at the switch level.


Unlock all Fortinet NSE5_FSW_AD-7.6 questions

Full exam access, validated answers, and unlimited practice with no download limits.

How QA4Exam.com Helps You Pass

QA4Exam.com offers Exam PDF and Online Practice Test materials designed to help you prepare for the Fortinet NSE5_FSW_AD-7.6 exam with confidence. The Exam PDF gives you actual questions and answers in a convenient study format, while the Online Practice Test helps you experience a realistic exam simulation. With up-to-date questions and verified answers, you can focus on the topics that matter most and measure your readiness accurately. The practice test also helps you build time management skills so you can handle the real exam more effectively. Together, these resources can improve your preparation and support your goal of passing on the first attempt.

Frequently Asked Questions

1. Who should take the Fortinet NSE5_FSW_AD-7.6 exam?

It is intended for network professionals who work with FortiSwitch and want to validate their knowledge as part of the Fortinet Certified Professional, FCP Fortinet Certified Professional Secure Networking path.

2. Is the Fortinet NSE 5 - FortiSwitch 7.6 Administrator exam difficult?

It can be challenging because it covers concepts, deployment, Layer 2 security, and troubleshooting. Candidates who understand the product and practice with exam-style questions usually feel more prepared.

3. Can I pass with only braindumps?

Braindumps alone are not the best approach. You should combine practice questions with product understanding and hands-on familiarity so you can answer scenario-based questions with confidence.

4. Do I need hands-on experience with FortiSwitch?

Yes, hands-on experience is very helpful. The exam is focused on practical administration, so real exposure to deployment, management, and troubleshooting makes preparation stronger.

5. Are the QA4Exam.com dumps enough to pass on the first attempt?

The QA4Exam.com Exam PDF and Online Practice Test are designed to support first-attempt success by giving you actual questions and answers, verified content, and realistic practice. Using them with review and practice can improve your readiness significantly.

6. What is included in the QA4Exam.com practice test format?

The Online Practice Test is built to simulate the exam environment, helping you practice under timed conditions and get familiar with the question style before test day.

7. Will these materials help me manage exam time better?

Yes, the practice test is useful for time management practice because it lets you work through questions in an exam-like setting and improve your pacing before the real test.