
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

NSE5_FWB_AD-8.0 Exam Dumps and Practice Questions

Questions 1 to 5 of the 36-question NSE5_FWB_AD-8.0 bank, each with its correct answer and an explanation. 1 of 5 ask for more than one answer. This is page 1 of 7.

1 / 7

Actual Fortinet NSE5_FWB_AD-8.0 Exam Questions

Question 1

Refer to the exhibit.
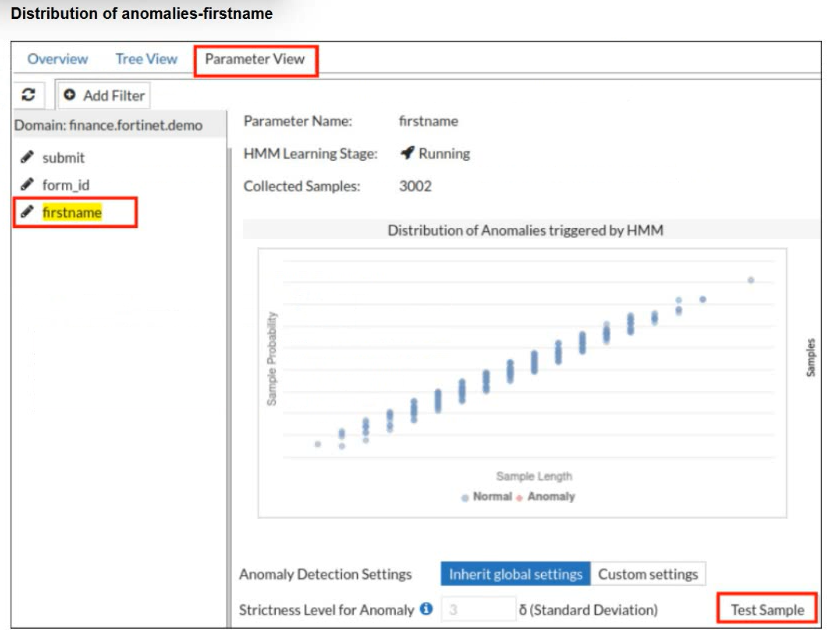
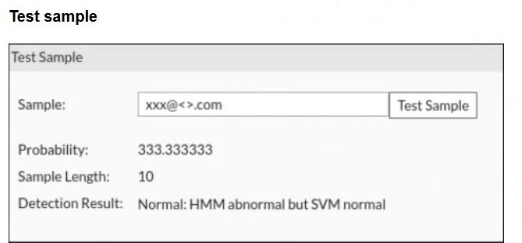
A FortiWeb administrator tests a new form input value after training the machine learning (ML) anomaly detection system.

The hidden Markov model (HMM) flags the input as abnormal, while the support vector machine (SVM) model classifies it as normal. FortiWeb allows the request.

What does this result indicate about the FortiWeb ML anomaly detection behavior?

Correct answer: C

FortiWeb machine learning uses layered detection rather than treating every unusual value as malicious. The HMM layer models normal parameter behavior and can flag a value as abnormal when it falls outside the learned distribution. However, abnormal does not automatically mean hostile. FortiWeb then uses additional ML classification logic, including SVM-based evaluation, to determine whether the anomaly resembles an actual attack or simply a legitimate unusual input. In this case, HMM noticed that the value was uncommon, but SVM classified it as normal, so FortiWeb allowed the request. That is expected behavior. Raising thresholds, disabling models, or assuming FortiWeb failed would misunderstand the two-stage ML decision process.

Question 2

A FortiWeb administrator wants to create a machine learning (ML)-based bot detection system.

Which three actions must the administrator take to build and activate this ML model? (Choose three.)

Correct answer: A, D, E

FortiWeb machine learning protection depends on observed application traffic. The administrator must first collect traffic samples so FortiWeb can learn normal behavior and create a useful baseline. After sample collection, FortiWeb uses the collected data to build the detection model. Once the model is built, it must be enabled or run in the live environment so FortiWeb can evaluate production requests and detect abnormal or bot-like behavior. Manual verification on test data only is not enough to activate the model for real traffic. Bayesian analysis is not the FortiWeb configuration step shown for this process; the platform handles model logic internally. The practical workflow is collection, model building, and live enforcement or detection.


Question 3

A FortiWeb administrator is deciding between using SAML SSO or HTML authentication. They want to minimize the number of credential prompts users receive across multiple Fortinet services.

Which statement accurately describes which option is best, and why?

Correct answer: A

SAML SSO is the correct choice when the goal is to reduce repeated credential prompts across multiple services. SAML uses a federated identity model, where users authenticate through an identity provider and then use assertions to access service providers without repeatedly entering credentials. This is exactly the value of single sign-on. HTML form authentication is more local and application-specific; it can authenticate users to a protected site, but it does not provide the same cross-service identity federation. Option B overstates SAML as a policy-blocking mechanism. Option C may be simpler but does not meet the SSO requirement. Option D incorrectly describes HTML form authentication as token-based remote-service access.


Question 4

A FortiWeb administrator wants to stop coordinated scraping traffic coming from several IP addresses, each making only a few requests so thresholds never trigger.

Which tactic should the administrator deploy to identify botnets using shared behavioral signals instead of volume?

Correct answer: C

The scenario describes distributed scraping where each individual IP stays below request-rate thresholds. A simple DoS threshold is weak here because the attacker avoids volume-based detection per source. Static blocklists are also ineffective because many botnet IPs may appear only once or rotate frequently. Blocking every non-allowlisted user agent would cause severe false positives and is easy for bots to evade by spoofing headers. FortiWeb bot mitigation is the correct control because it can evaluate behavior beyond source IP volume. Device fingerprinting, browser behavior, headers, JavaScript challenges, and client characteristics help correlate suspicious automation even when requests are spread across many addresses. Therefore, bot mitigation with behavioral/device fingerprinting is the strongest answer.


Question 5

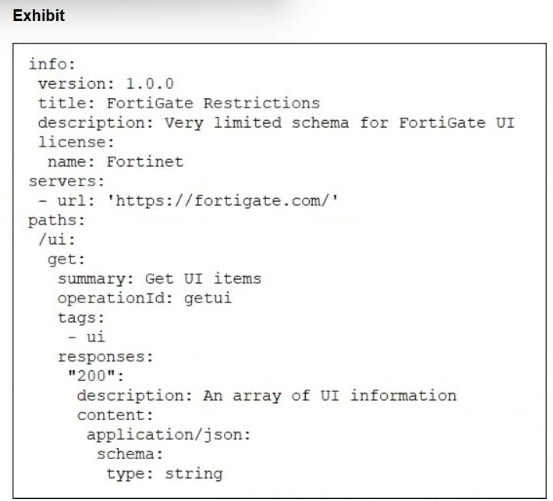
Refer to the exhibit.

What does the exhibit show?

Correct answer: D

The exhibit is written in structured OpenAPI/YAML-style format. It includes fields such as info, version, title, servers, paths, HTTP method get, operationId, responses, content type application/json, and a schema definition. That is not HTML and it is not a live API response. It is also not CLI output from FortiWeb. FortiWeb OpenAPI validation uses OpenAPI description files in YAML or JSON to define API structure, endpoints, parameters, and expected data types. FortiWeb then uses that uploaded schema as a baseline to validate API requests and block requests that do not conform. So the exhibit is best identified as an API schema file


Unlock all Fortinet NSE5_FWB_AD-8.0 questions

Full exam access, validated answers, and unlimited practice with no download limits.