
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

NSE5_SSE_AD-7.6 Exam Dumps and Practice Questions

Questions 1 to 5 of the 50-question NSE5_SSE_AD-7.6 bank, each with its correct answer and an explanation. 2 of 5 ask for more than one answer. This is page 1 of 10.

1 / 10

Actual Fortinet NSE5_SSE_AD-7.6 Exam Questions

Question 1

Refer to the exhibit, which shows the SD-WAN rule status and configuration.
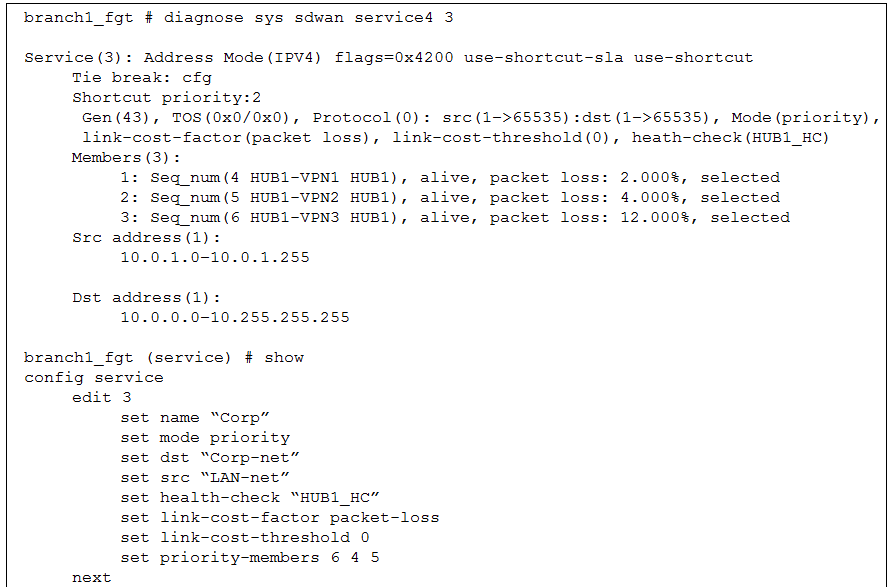
Based on the exhibit, which change in the measured packet loss will make HUB1-VPN3 the new preferred member? (Choose one answer)

Correct answer: A

According to the SD-WAN 7.6 Core Administrator study guide and the FortiOS 7.6 Administration Guide, the selection process for the Best Quality (priority) strategy depends on two primary factors: the measured link quality metric and the configured member priority order.

Based on the provided exhibit (image_b40dfc.png), we can determine the following:

Strategy and Metric: The rule is in Mode(priority) (Best Quality) using link-cost-factor(packet loss).

Strict Comparison: The link-cost-threshold is set to 0. This means there is no 'advantage' given to the current preferred link; the FortiGate performs a strict comparison where the link with the objectively best metric is chosen.

Tie-Breaker Logic: When multiple links have the same packet loss, the FortiGate uses the Member Priority Order defined in the rule (set priority-members 6 4 5) as the tie-breaker.

Member 6 (HUB1-VPN3) is the highest priority.

Member 4 (HUB1-VPN1) is the second priority.

Member 5 (HUB1-VPN2) is the lowest priority.

Current State: HUB1-VPN1 is currently selected because its packet loss (2.000%) is lower than HUB1-VPN2 (4.000%) and HUB1-VPN3 (12.000%). Even though HUB1-VPN3 has a higher configuration priority, its significantly higher packet loss prevents it from being chosen.

Evaluation of Options:

Option A (Verified): If all three members have the same packet loss (e.g., they all show 2%), the quality metrics are equal. The SD-WAN engine then refers to the priority-members list. Since HUB1-VPN3 (Seq 6) is the first member in that list, it will immediately become the new preferred member.

Option B: If HUB1-VPN1 reaches 4%, it matches HUB1-VPN2 (4%). HUB1-VPN3 remains at 12%. The system will choose between VPN1 and VPN2. Since VPN1 (Seq 4) is higher in the priority list than VPN2 (Seq 5), HUB1-VPN1 stays preferred.

Option C: If HUB1-VPN1 reaches 12%, it matches HUB1-VPN3. However, HUB1-VPN2 is still better at 4.000%. Therefore, HUB1-VPN2 would become the new preferred member, not HUB1-VPN3.

Option D: If HUB1-VPN3 drops to 4%, it matches HUB1-VPN2. However, HUB1-VPN1 is still the best link at 2.000%, so it remains selected.
Question 2

SD-WAN interacts with many other FortiGate features. Some of them are required to allow SD-WAN to steer the traffic.

Which three configuration elements must you configure before FortiGate can steer traffic according to SD-WAN rules? (Choose three.)

Correct answer: A, C, D

According to the SD-WAN 7.6 Core Administrator study guide and the FortiOS 7.6 Administration Guide, for the FortiGate SD-WAN engine to successfully steer traffic using SD-WAN rules, three fundamental configuration components must be in place. This is because the SD-WAN rule lookup occurs only after certain initial conditions are met in the packet flow:

Interfaces (Option C): You must first define the physical or logical interfaces (such as ISP links, LTE, or VPN tunnels) as SD-WAN members. These members are then typically grouped into SD-WAN Zones. Without designated member interfaces, there is no 'pool' of links for the SD-WAN rules to select from.

Routing (Option D): For a packet to even be considered by the SD-WAN engine, there must be a matching route in the Forwarding Information Base (FIB). Usually, this is a static route where the destination is the network you want to reach, and the gateway interface is set to the SD-WAN virtual interface (or a specific SD-WAN zone). If there is no route pointing to SD-WAN, the FortiGate will use other routing table entries (like a standard static route) and bypass the SD-WAN rule-based steering logic entirely.

Firewall Policies (Option A): In FortiOS, no traffic is allowed to pass through the device unless a Firewall Policy permits it. To steer traffic, you must have a policy where the Incoming Interface is the internal network and the Outgoing Interface is the SD-WAN zone (or the virtual-wan-link). The SD-WAN rule selection happens during the 'Dirty' session state, which requires a policy match to proceed with the session creation.

Why other options are incorrect:

Security Profiles (Option B): While mandatory for Application-level steering (to identify L7 signatures), basic SD-WAN steering based on IP addresses, ports, or ISDB objects does not require security profiles to be active.

Traffic Shaping (Option E): This is an optimization feature used to manage bandwidth once steering is already determined; it is not a prerequisite for the steering engine itself to function.


Question 3

Refer to the exhibit.

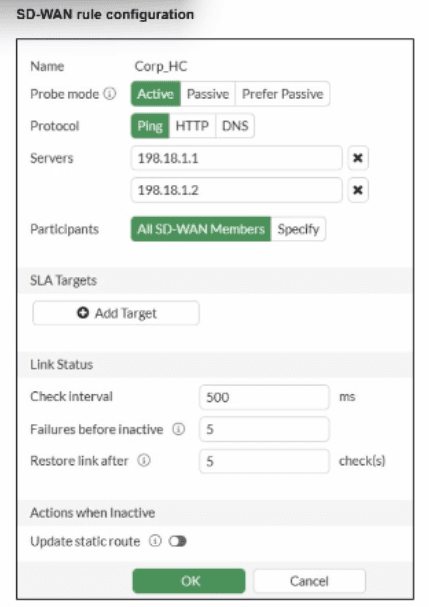
You want the performance service-level agreement (SLA) to measure the jitter of each member. Which configuration change must you make to achieve this result?

Correct answer: A

According to the SD-WAN 7.6 Core Administrator study guide and FortiOS 7.6 Administration Guide, no configuration change is required to simply measure jitter.

Implicit Measurement: In FortiOS, once a Performance SLA (Health Check) is configured with an Active probe mode (as seen in the exhibit with Ping selected), the FortiGate automatically begins calculating three key quality metrics for every member interface: Latency, Jitter, and Packet Loss.

Visibility: Even without an SLA Target defined, these real-time measurements are visible in the SD-WAN Monitor and via the CLI command diagnose sys virtual-wan-link health-check <SLA_Name>.

Active Probes: Because the probe mode is set to Active using the Ping protocol, the FortiGate sends synthetic packets at the defined Check interval (500ms in the exhibit). It calculates jitter by measuring the variation in the round-trip time (RTT) between these consecutive probes.

Why other options are incorrect:

Option B: Adding an SLA target and defining a jitter threshold is only necessary if you want the SD-WAN engine to make steering decisions based on that metric (e.g., 'remove this link from the pool if jitter exceeds 50ms'). It is not required just to measure the jitter.

Option C: While you can specify participants, the current setting is 'All SD-WAN Members,' which means it is already measuring jitter for every member.

Option D: HTTP is an alternative probe protocol, but Ping (ICMP) is perfectly capable of measuring jitter and is often preferred for its lower overhead.


Question 4

Which two statements correctly describe what happens when traffic matches the implicit SD-WAN rule? (Choose two answers)

Correct answer: B, E

According to the SD-WAN 7.6 Core Administrator study guide and FortiOS 7.6 Administration Guide, the 'implicit rule' is the default rule at the bottom of the SD-WAN rule list (ID 0). It is only evaluated if traffic does not match any manually configured SD-WAN rules.

Policy Route Table Context (Option B): SD-WAN rules are technically a specialized form of policy-based routing. For a packet to match the implicit rule, it must first pass through the routing hierarchy. If traffic matches the implicit rule, it indicates that it did not match any higher-priority user-defined SD-WAN rules or any specific entries in the manual policy route table that would have intercepted the traffic earlier.

Session Information (Option E): When you use the CLI to inspect an active session (e.g., diagnose sys session list), the output contains a field for the SD-WAN Service ID. If traffic is steered by a user-defined rule, it displays the ID of that rule (e.g., service_id=1). However, when traffic falls through to the implicit rule, the session information displays no SD-WAN service ID (it often shows as 0 or is omitted), because the implicit rule does not function as a 'service' in the same way user-defined rules do.

Routing Behavior: The implicit rule follows the standard routing table (RIB/FIB) logic. It uses the priority and distance of the static routes to determine the path. If multiple paths have the same distance and priority, it uses the algorithm set by v4-ecmp-mode, but this is a function of the routing engine, not the SD-WAN engine itself.

Why other options are incorrect:

Option A: While v4-ecmp-mode (e.g., source-ip-based) is used for ECMP routing, this is part of the general FortiOS routing behavior for equal-cost paths in the FIB, whereas the implicit rule simply 'hands over' the decision to that routing table.

Option C: When traffic matches the implicit rule, the session is actually flagged with vwl_id=0 and potentially dirty if a route change occurs, but vwl_default is not the standard flag name used in this specific context in the curriculum.

Option D: This is incorrect because the implicit rule does respect weight, distance, and priority as defined in the static routes within the routing table; it does not distribute traffic 'regardless' of these values.


Question 5

Refer to the exhibit.

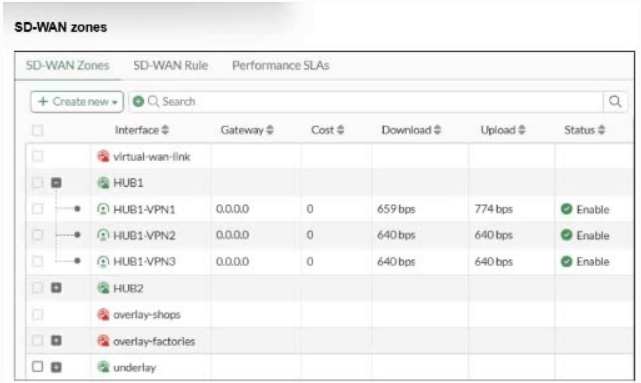
An SD-WAN zone configuration on the FortiGate GUI is shown.

What can you conclude about the zone and member configuration on this device?

Correct answer: C

The exhibit indicates that the overlay-factories zone currently contains no SD-WAN member. In the GUI, zones containing members can be expanded to display their member interfaces; for example, HUB1 is expanded and shows HUB1-VPN1, HUB1-VPN2, and HUB1-VPN3. The overlay-factories entry does not display any member beneath it. The SD-WAN study material explains that an SD-WAN zone uses one or more interface members and that a zone used for traffic steering must contain at least one member. SD-WAN_7.6_Enterprise_Administr... The exhibit alone does not establish that overlay-factories can safely be deleted because other configuration references can prevent deletion. Likewise, virtual-wan-link is the default SD-WAN zone and cannot simply be treated as a removable user-created zone. Therefore, the directly supported conclusion is that overlay-factories has no member.


Unlock all Fortinet NSE5_SSE_AD-7.6 questions

Full exam access, validated answers, and unlimited practice with no download limits.