
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

Free Fortinet NSE6_OTS_AR-7.6 Exam Dumps and Practice Questions

Questions 1 to 5 of the 35-question Fortinet NSE 6 - OT Security 7.6 Architect exam bank, each with its correct answer and an explanation. 3 of 5 ask for more than one answer. This is page 1 of 7.

1 / 7

Actual Fortinet NSE6_OTS_AR-7.6 Exam Questions

Question 1

Multiple Answers

Refer to the exhibit.
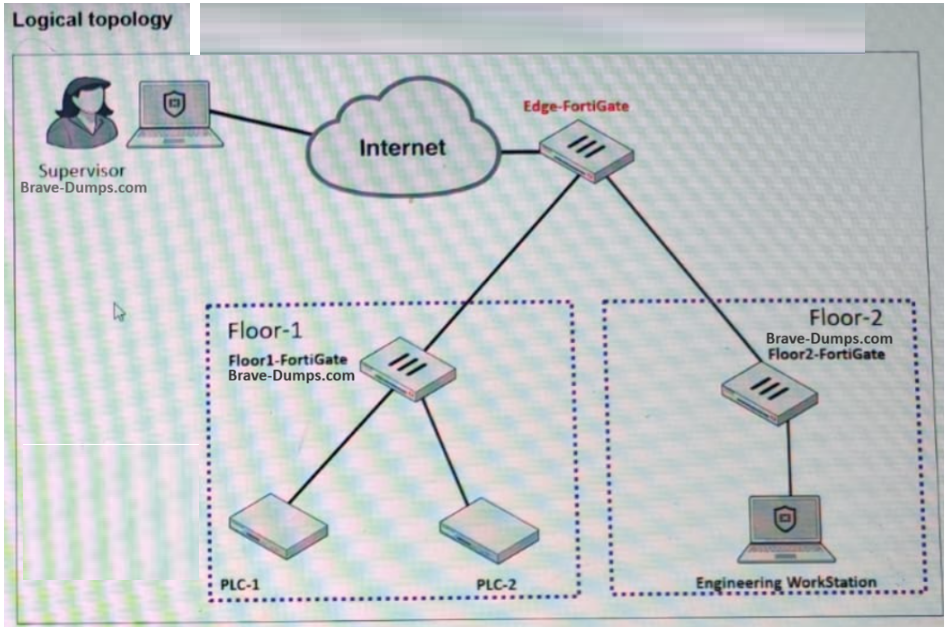
A partial OT network is shown. You want to provide the supervisor with secure remote access. Which two features can you implement on Edge-FortiGate? (Choose two answers)

Correct answer: A, B

Based on the exhibit and the OT Security 7.6 Architect standards for Secure Remote Access:

Secure Tunneling (Statement A): The exhibit shows a Remote PC connecting through a VPN Cloud to the Edge-FortiGate. In the Fortinet architecture, IPsec VPN is the primary method for establishing a secure, encrypted tunnel for remote administrators or supervisors to access the internal OT segments (Level 2/3) from an external location.

Multi-Factor Authentication (Statement B): Secure remote access in OT environments (aligned with IEC 62443 standards) requires strong authentication. The study guide emphasizes the use of FortiToken to provide Two-Factor Authentication (2FA) for VPN users, ensuring that compromised credentials alone are not enough to gain access to critical infrastructure.

FSSO (Statement D): Fortinet Single Sign-On is generally used for identifying internal users already on the network to apply identity-based policies; it is not the primary mechanism for establishing the remote connection itself.

SD-WAN (Statement C): While SD-WAN can manage the path of the VPN traffic, it is a WAN optimization and reliability feature, not a 'secure remote access' feature for a supervisor in the context of authentication and encryption.
Question 2

Multiple Answers

Refer to the exhibit.

A partial OT network is shown. You want to configure an automated alert sent by FortiAnalyzer when an attack occurs on a FortiGate device. Which two configurations must you implement? (Choose two answers)

Correct answer: A, D

The correct answers are A and D. The study guide provides a direct use case called Attack Detection and Automated Alert. It states: ''A downstream FortiGate detects an attack and sends logs to FortiAnalyzer. FortiAnalyzer parses the logs and notifies the root FortiGate. The root FortiGate triggers the action, which in this case, is a notification to the administrator.'' The same slide also explicitly shows ''Stitches configured on root FortiGate.'' This confirms that to send the automated alert, you must configure the automation stitch on the root FortiGate.

The second required configuration is an event handler on FortiAnalyzer. The guide explains that ''Event handlers generate events'' and that ''FortiAnalyzer uses event handlers to filter all incoming logs. If logs match the conditions configured in an event handler, FortiAnalyzer generates an event.'' Since FortiAnalyzer must detect the attack from the received logs before notifying the root FortiGate, an event handler is required on FortiAnalyzer.

Option B is incorrect because the study guide does not identify a LOCALHOST task as the required configuration for this attack-alert flow. Option C is also incorrect because the question asks what must be configured to enable the automated alert workflow. An IPS profile may detect some attacks, but the required automation path in the study guide is specifically event handler on FortiAnalyzer + stitch on the root FortiGate.


Question 3

Single Answer

According to the IEC 62443 standard, your security level is 4. What is your OT environment defending against? (Choose one answer)

Correct answer: C

According to the OT Security 7.6 Architect study guide regarding IEC 62443 Security Levels:

Security Level 4 (SL 4) Definition: This level provides 'Protection against intentional violation using sophisticated means with extended resources, specific skills, and high motivation'.

Real-World Application: The study guide specifically notes: 'If you are facing a syndicate of cyber extortionists with extensive resources and capabilities, then you should strive for security level 4'.

Comparison to other levels:

SL 1: Protection against 'casual or unintentional system violation'.

SL 2: Protection against 'intentional violation using simple means with low resources'.

SL 3: Protection against 'intentional violation using sophisticated means with moderate resources'.


Question 4

Single Answer

Refer to the exhibit.

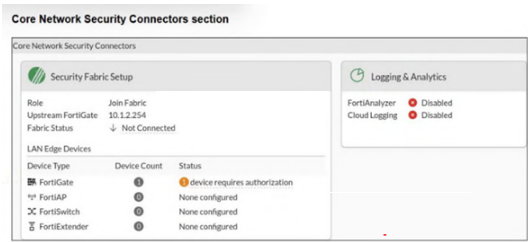
The Core Network Security Connectors page of the FortiGate-2 device is shown. Which statement is correct? (Choose one answer)

Correct answer: D

Based on the provided exhibit and the OT Security 7.6 Architect curriculum regarding the Fortinet Security Fabric:

Fabric Role: The exhibit clearly shows that FortiGate-2 has the role set to Join Fabric. This confirms it is a downstream device and not the Fabric Root (eliminating Option A).

Upstream Connection: The device is configured to point to an Upstream FortiGate at IP address 10.1.2.254.

Fabric Status: The status is currently displayed as Not Connected. In a standard Fortinet Security Fabric deployment, once a downstream device is configured to join the fabric, it sends a request to the upstream root device. The root FortiGate must then explicitly authorize the downstream unit before the connection is established and the status changes to 'Connected.'

Authorization Requirement: The 'Not Connected' status, while having the upstream IP correctly configured, is the classic indicator that the authorization step is pending on the root FortiGate. Furthermore, under the LAN Edge Devices section, it shows another downstream FortiGate requiring authorization on this specific unit, highlighting that authorization is a manual security requirement for all stages of the Fabric hierarchy.

FortiAnalyzer Status: While the Logging & Analytics section shows FortiAnalyzer is Disabled, this is a configuration choice and does not prevent the Security Fabric from connecting; therefore, configuring it is not the solution to the connectivity status shown (eliminating Option C).

In summary, FortiGate-2 cannot join the fabric until an administrator logs into the Root FortiGate (10.1.2.254) and authorizes the join request from FortiGate-2.


Question 5

Multiple Answers

Refer to the exhibit.

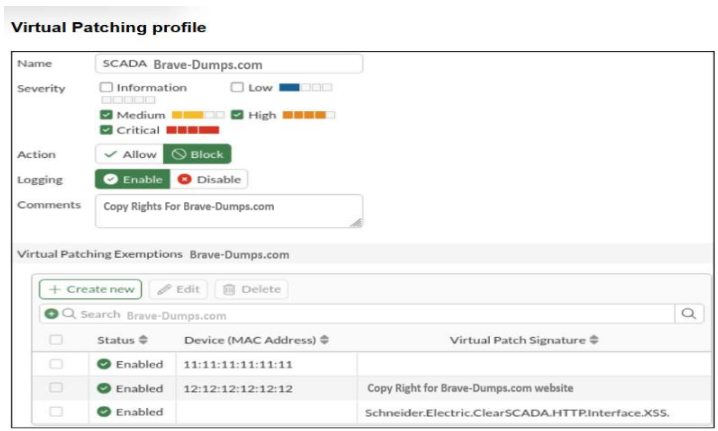
A Virtual Patching profile is shown. You have recently updated your SCADA system and would like to apply the SCADA virtual patching profile. Which two statements about this profile are correct? (Choose two answers)

Correct answer: B, D

The correct answers are B and D.

Option B is correct because the profile has Medium, High, and Critical selected, while Low severity is not selected. That means low-severity virtual patching signatures are not enforced by this profile. So for the device with MAC address 12:12:12:12:12, low-severity signatures are not blocked. The study guide explains virtual patching as device-specific protection where ''FortiGate caches the signatures and mitigation rules that apply to each device'' and applies them when the related traffic matches the firewall policy.

Option D is correct because the Virtual Patching Exemptions table shows a row with the MAC address 11:11:11:11:11 and no specific signature listed. The study guide states that in the Virtual Patching profile you can ''Exempt a specific device with the MAC address or a specific signature.'' A MAC-only exemption means that specific device is excluded from virtual patching enforcement, so in practical terms it is treated as having no applicable vulnerabilities in this profile.

Option C is incorrect because the profile does not block critical signatures for all devices. The exemptions list proves that at least one device can be excluded by MAC address, and a specific signature can also be exempted. Therefore, enforcement is not universal across all devices.

Option A is incorrect because the entry Schneider.Electric.ClearSCADA.HTTP.Interface.XSS appears as a specific signature exemption, not as the only remaining vulnerability. The profile display is showing exemptions, not a statement that only one vulnerability is still present.


Unlock all Fortinet NSE6_OTS_AR-7.6 questions

Full exam access, validated answers, and unlimited practice with no download limits.