
An administrator is relying on an Azure Bicep linter to find possible issues in Bicep files.
Which problem can the administrator expect to find?
Correct answer:
B
Questions 1 to 5 of the 67-question NSE7_CDS_AR-7.6 bank, each with its correct answer, 3 with an explanation. This is page 1 of 13.
An administrator is relying on an Azure Bicep linter to find possible issues in Bicep files.
Which problem can the administrator expect to find?
Refer to the exhibit.
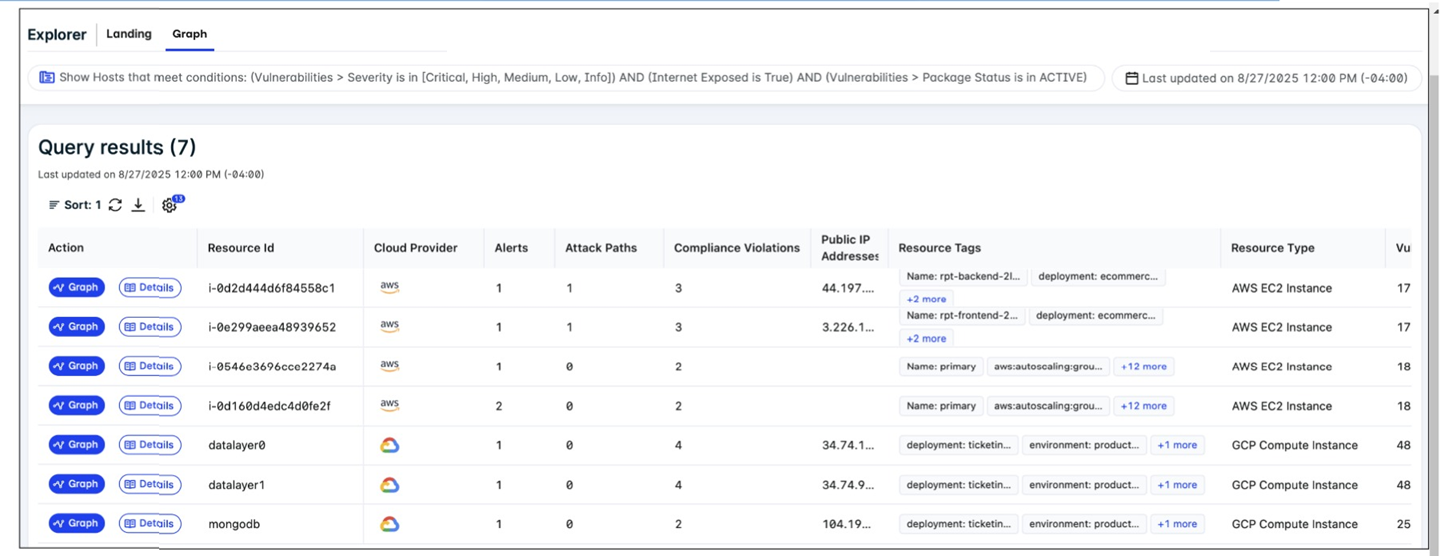
A FortiCNAPP administrator used the FortiCNAPP Explorer to reveal all hosts exposed to the internet that are running active packages with vulnerabilities of all severity levels. Why do only the first two results have an attack path? (Choose one answer)
Comprehensive and Detailed Explanation From FortiOS 7.6, FortiWeb 7.4 Exact Extract study guide:
Based on the FortiCNAPP (formerly Lacework) Cloud Security documentation regarding Attack Path Analysis and Explorer functionality:
Attack Path Generation (Option A): In FortiCNAPP, an 'Attack Path' is a visualized sequence of potential exploit steps that an external attacker could take to reach a sensitive resource. For the platform to generate and display an attack path, the target resource must be externally reachable.
Evidence in the Exhibit: * The exhibit shows a list of EC2 and GCP instances.
The first two results (Resource IDs i-0d2d... and i-0e29...) have values populated in the Public IP Addresses column (44.197.... and 3.226....). Consequently, these are the only two resources showing a value of 1 in the Attack Paths column.
The remaining resources in the list do not have public IP addresses listed in the exhibit's view, and as a result, their Attack Paths count is 0. This confirms that FortiCNAPP specifically calculates these paths for resources that have a direct entry point from the internet via a public IP.
Contextual Risk Assessment: FortiCNAPP prioritizes attack path analysis for internet-exposed assets because they represent the highest immediate risk. While internal resources may have vulnerabilities, the lack of a public-facing network interface means there is no direct external 'path' to visualize in this specific Explorer view.
The cloud administration team is reviewing an AWS deployment that was done using CloudFormation.
The deployment includes six FortiGate instances that required custom configuration changes after being deployed. The team notices that unwanted traffic is reaching some of the FortiGate instances because the template is missing a security group.
To resolve this issue, the team decides to update the JSON template with the missing security group and then apply the updated template directly, without using a change set.
What is the result of following this approach?
Refer to the exhibit.
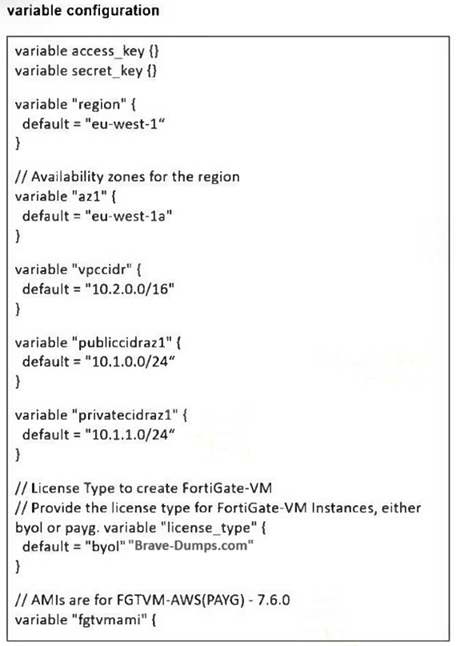
You are tasked to deploy a FortiGate VM with private and public subnets in Amazon Web Services (AWS). You examined the variables.tf file. Assume that all the other terraform files are in place. What will be the final result after running the terraform init and terraform apply commands? (Choose one answer)
Comprehensive and Detailed Explanation From FortiOS 7.6, FortiWeb 7.4 Exact Extract study guide:
Based on the FortiOS 7.6 AWS Administration Guide and the Fortinet 7.4 Public Cloud Security documentation regarding Terraform deployments:
Variable Validation and Logic (Option A): The variables.tf file contains a logic error that prevents a successful deployment.
Specifically, the variable license_type has a default value defined as 'byol' 'Brave-Dumps.com'.
In Terraform HCL (HashiCorp Configuration Language), a variable's default attribute can only hold a single value string (e.g., 'byol'). The inclusion of the secondary string 'Brave-Dumps.com' within the same default assignment is a syntax error.
Impact on Execution: When terraform apply is executed, the Terraform engine performs a validation check on all loaded files. Because of this syntax error in the variable definition, the validation will fail, and Terraform will stop execution with an error message before any resources---including the FortiGate VM---are created in AWS.
Network Mismatch: Additionally, the variable vpccidr is set to 10.2.0.0/16, while the public (10.1.0.0/24) and private (10.1.1.0/24) subnets are defined within a completely different address space (10.1.x.x). Even if the syntax error were fixed, the deployment would likely fail at the infrastructure level because subnets must reside within the CIDR block of their parent VPC.
Why other options are incorrect:
Option B, C, & D: None of these successful deployment outcomes can occur because the Terraform parser will identify the invalid syntax in the variables.tf file and abort the process entirely.
Refer to the exhibit.
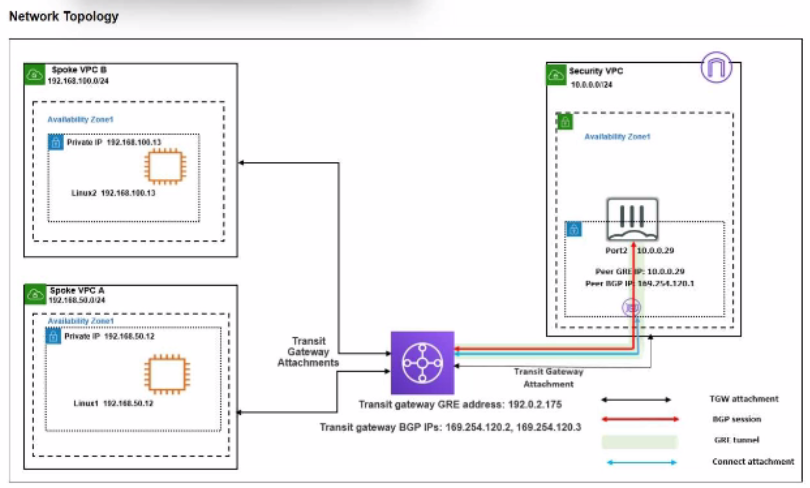
You attempted to access the Linux1 EC2 instance directly from the internet using its public IP address in AWS. However, your connection is not successful.
Given the network topology, what can be the issue?
The Fortinet documentation states: 'An IGW in AWS is a VPC component that allows communication between instances in your VPC and the internet... AWS users with less experience may face connectivity issues if they create a new VPC, add EC2 instances to it, but forget that they need an IGW for internet connectivity.'
Full exam access, validated answers, and unlimited practice with no download limits.