
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

NSE7_SSE_AD-25 Exam Dumps and Practice Questions

Preview page 1 of 18 with real questions 1 to 5 from the full 88-question Fortinet set.

Fortinet NSE7_SSE_AD-25 Dumps - Pass Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator Exam in First Attempt 2026

The Fortinet NSE7_SSE_AD-25 exam, also known as the Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator exam, is part of the Fortinet Certified Solution Specialist, FCSS Fortinet Certified Solution Specialist Secure Access Service Edge certification track. It is designed for professionals who manage and secure SASE environments and want to validate their practical understanding of FortiSASE. This exam matters because it demonstrates the ability to deploy, integrate, and manage secure access services in modern enterprise networks. Earning this certification can help show that you are prepared for real-world SASE administration tasks.

Exam Topics and Approximate Weightage

# Exam Topics Sub-Topics Approximate Weightage (%)
1 SASE architecture and integration FortiSASE components, integration with enterprise networks, identity and access design, traffic flow and policy alignment 30%
2 SASE deployment and management Deployment planning, configuration tasks, policy administration, service monitoring and operational management 30%
3 Secure Private Access (SPA) Access control setup, private application access, user and group policy, secure connectivity validation 20%
4 Analytics Log review, reporting insights, event analysis, security and usage visibility 20%

This exam tests more than memorization. Candidates need a solid grasp of FortiSASE concepts, deployment workflows, and management tasks, along with the ability to interpret analytics and apply secure access principles in practical scenarios. It is designed to measure both knowledge depth and day-to-day administrative readiness.

Actual Fortinet NSE7_SSE_AD-25 Exam Questions

Question 1

A FortiSASE customer has been enforcing always-on VPN for their remote users running FortiClient. What option can be enabled under the customer's Endpoint Profile to allow them access different resources located in the same L2 network? (Choose one answer)

Correct answer: A

In a FortiSASE environment where always-on VPN is enforced, FortiClient typically establishes a full tunnel to a Security Point of Presence (PoP). By default, a full-tunnel configuration instructs the endpoint to send all traffic---including traffic destined for the local network---through the secure tunnel to FortiSASE for inspection.

The Local Access Challenge: When a remote user is at home or in a satellite office, they often need to access local resources such as printers, NAS devices, or other computers on the same Layer 2 (L2) broadcast domain. In a standard full-tunnel setup, these local resources become unreachable because the routing table on the endpoint prioritizes the VPN interface for all non-local-gateway traffic.

Allow Local LAN Access: To resolve this while maintaining the security of the 'Always-On' requirement, FortiSASE administrators can enable the Allow Local LAN Access feature within the Endpoint Profile.

Configuration Logic: This setting modifies the FortiClient configuration (often via an XML update pushed from the FortiSASE EMS) to include an exemption for the endpoint's locally connected subnet. Specifically, it ensures that traffic destined for the local L2 network does not enter the IPsec or SSL-VPN tunnel, allowing the user to interact with local peripherals while all other internet and corporate-bound traffic remains secured by FortiSASE.

Incorrect Options: * Option B and C: Sandbox and Anti-Virus protections are security features for threat detection and do not influence the routing of local network traffic.

Option D: Network Lockdown actually does the opposite; it restricts network access until a VPN connection is established and typically blocks local LAN access unless specific exemptions are made, making it the incorrect choice for enabling access to local resources.

Question 2

During FortiSASE provisioning, how many security points of presence (POPs) need to be configured by the FortiSASE administrator?

Correct answer: D

During FortiSASE provisioning, the FortiSASE administrator needs to configure at least one security point of presence (PoP). A single PoP is sufficient to get started with FortiSASE, providing the necessary security services and connectivity for users.

Security Point of Presence (PoP):

A PoP is a strategically located data center that provides security services such as secure web gateway, firewall, and VPN termination.

Configuring at least one PoP ensures that users can connect to FortiSASE and benefit from its security features.

Scalability:

While only one PoP is required to start, additional PoPs can be added as needed to enhance redundancy, load balancing, and performance.


FortiOS 7.6 Administration Guide: Provides details on the provisioning process for FortiSASE.

FortiSASE 23.2 Documentation: Explains the configuration and role of security PoPs in the FortiSASE architecture.

Question 3

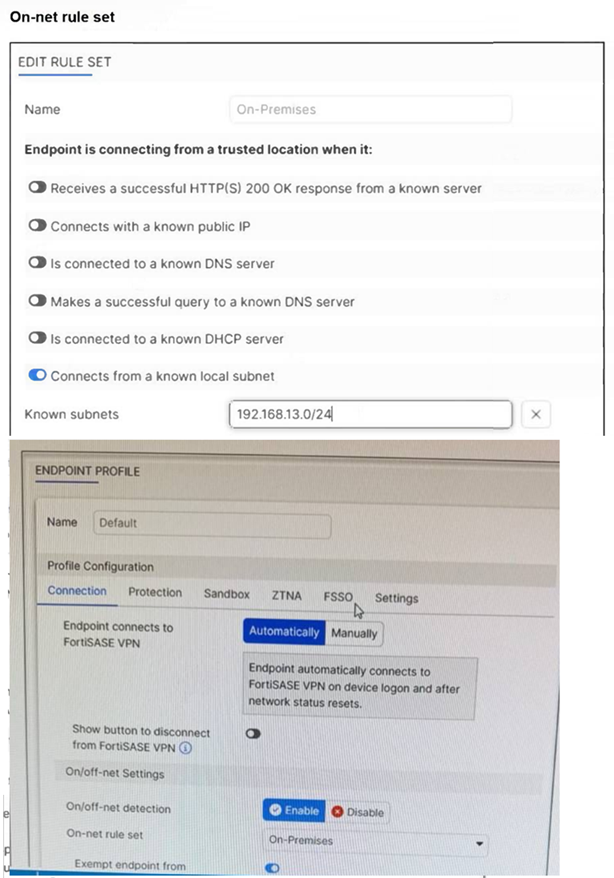
Refer to the exhibits.

An endpoint is assigned an IP address of 192.168.13.101/24. Which action will be run on the endpoint? (Choose one answer)

Correct answer: C

Based on the provided exhibits and the logic of FortiSASE On/off-net detection, the endpoint's behavior is determined by its network environment relative to the configured rules.

Subnet Matching and Detection: The On-net rule set (named 'On-Premises') is configured to identify a trusted location when the endpoint 'Connects from a known local subnet'. The administrator has defined the known subnet as $192.168.13.0/24$. Since the endpoint's IP address is $192.168.13.101$, it falls within this range. Consequently, FortiClient detects the endpoint as being on-net (on-fabric).

Action Logic (Exemption): In a FortiSASE Endpoint Profile, when On/off-net detection is enabled and an endpoint matches an 'On-net' rule, the standard behavior is to exempt the endpoint from auto-connecting to the FortiSASE VPN tunnel. This design assumes the endpoint is already in a secured office environment where the corporate firewall (FortiGate) provides the necessary protection, making the SASE tunnel redundant.

Comparison of Other Options: * Option B: Incorrect, because the IP matches the defined 'known local subnet' rule for on-net detection.

Option D: Incorrect, as auto-connect only triggers when the endpoint is detected as off-net to ensure remote security.


Question 4

What are the key differences between the FortiSASE BGP per overlay and BGP on loopback routing design methods? (Choose one answer)

Correct answer: A

FortiSASE supports two main routing design methods for Secure Private Access (SPA) when connecting to a FortiGate SD-WAN hub:

BGP per Overlay (Traditional/Default Method): In this configuration, a separate iBGP session is established over every individual IPsec overlay (tunnel) between the FortiSASE PoP and the hub. These sessions terminate on the tunnel interface IP addresses. To facilitate this, the hubs typically use the IPsec VPN mode-cfg feature to dynamically assign tunnel IP addresses to the SASE PoPs. For every LAN prefix, the system generates multiple BGP routes---one for each overlay---which increases the total number of routes advertised across the network.

BGP on Loopback (Modern Alternative): This newer design establishes only a single iBGP session between the spoke and the hub, regardless of how many physical or logical overlays (tunnels) connect them. The session is terminated on a loopback interface on both sides.

Key Advantages of BGP on Loopback:

Reduced Complexity: It significantly simplifies the BGP configuration because there are fewer neighbors to manage.2

Improved Scalability: It greatly reduces the volume of routes advertised, as only a single BGP route is generated for each LAN prefix, making it the preferred choice for large-scale deployments.

Resiliency: The BGP session remains active as long as the loopback is reachable via any of the available overlays, meaning no BGP convergence is required if a single overlay fails.


Question 5

One user has reported connectivity issues; no other users have reported problems. Which tool can the administrator use to identify the problem? (Choose one answer)

Correct answer: B

In a FortiSASE deployment, Digital Experience Monitoring (DEM) is the primary diagnostic tool used to troubleshoot connectivity and performance issues specifically for a single user or endpoint.

End-to-End Visibility: DEM provides real-time, end-to-end visibility into the network path between the end-user's device and the application they are trying to reach. This is critical when only one user reports an issue, as it allows administrators to pinpoint whether the problem resides on the local device, the local ISP, the SASE backbone, or the destination application.

Performance Metrics: The DEM agent (often integrated with the FortiMonitor agent on the endpoint) collects granular performance metrics such as latency, jitter, packet loss, and RTT (Round Trip Time). It also provides device-specific health data, including CPU and memory usage, to determine if the connectivity issue is actually caused by the remote computer's performance.

Hop-by-Hop Analysis: Unlike standard monitoring, DEM offers End-to-End Continuous Hop Analytics. This path monitoring visualizes every 'hop' in the traffic route and highlights exactly where degraded service is occurring. For a single user experiencing issues while everyone else is fine, this tool immediately triangulates if a specific 'problem hop' in their unique connection path is the cause.

Operational Comparison: * MDM (A) is used for managing device configurations and software distribution, not for real-time network performance troubleshooting.

Forensics (C) is a security-focused service used for investigating malware incidents or data breaches, not for measuring network latency.

SOCaaS (D) is a managed security service for threat monitoring and event triage; while it handles 'security' connectivity issues (like a blocked IP), it is not a tool for performance metric evaluation.


Unlock all Fortinet NSE7_SSE_AD-25 questions

Full exam access, validated answers, and unlimited practice with no download limits.

How QA4Exam.com Helps You Pass

QA4Exam.com offers the Exam PDF with actual questions and answers, plus an Online Practice Test that helps you prepare with confidence for the Fortinet NSE7_SSE_AD-25 exam. The practice test gives you a real exam simulation so you can get familiar with the question style and improve your time management. The questions are updated and verified, helping you focus on the most relevant exam content. With both the PDF and practice test, you can strengthen your preparation and work toward passing on your first attempt.

Frequently Asked Questions

1. Who should take the Fortinet NSE7_SSE_AD-25 exam?

This exam is for professionals working with FortiSASE and secure access service edge environments who want to validate their enterprise administration skills as part of the FCSS Secure Access Service Edge certification track.

2. Is the Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator exam difficult?

It can be challenging because it tests practical knowledge of SASE architecture, deployment, SPA, and analytics. Candidates who understand real FortiSASE administration tasks are usually better prepared.

3. Can I pass with only braindumps?

Braindumps alone are not a complete preparation method. They are most effective when combined with hands-on understanding and practice so you can handle different question styles and scenarios.

4. Do I need hands-on experience for NSE7_SSE_AD-25?

Hands-on experience is very helpful because the exam focuses on deployment, management, integration, and operational knowledge. Practical familiarity makes it easier to understand the correct answers.

5. Are QA4Exam.com dumps and practice tests enough to prepare?

They are a strong preparation resource because they provide verified answers, updated questions, and a realistic practice format. Many candidates use them to reinforce study and improve exam readiness.

6. How do the QA4Exam.com practice tests help with first-attempt success?

The online practice test simulates the exam environment, helps you manage time, and shows you how questions may appear in the real test. This can improve confidence and reduce surprises on exam day.

7. What format do the QA4Exam.com study materials use?

QA4Exam.com provides an Exam PDF with actual questions and answers and an Online Practice Test for interactive preparation. Both formats are designed to support efficient study and exam simulation.