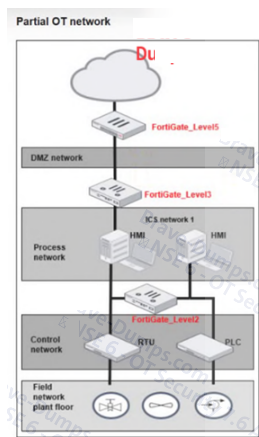
Refer to the exhibit.
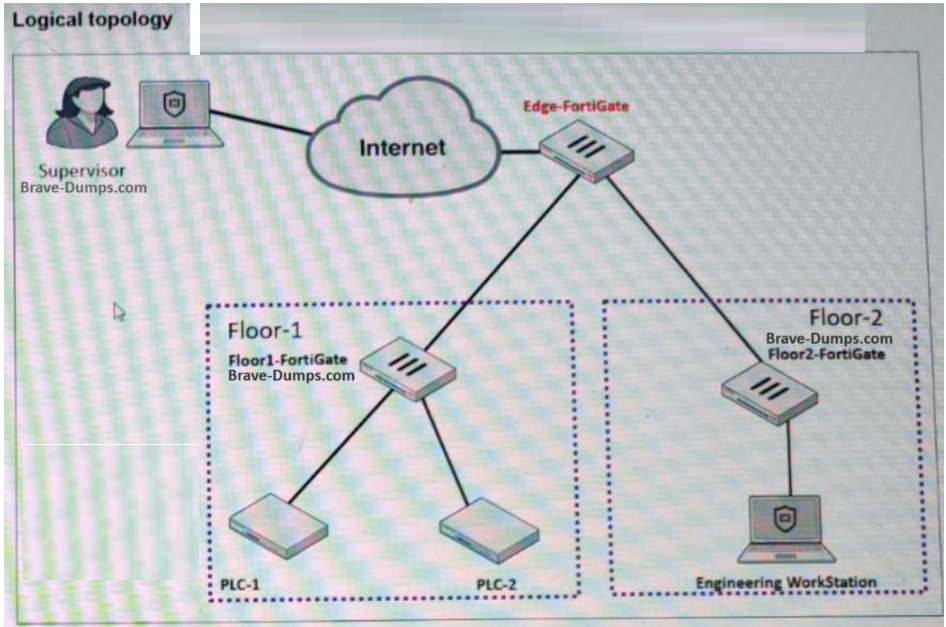
A partial OT network is shown. You want to provide the supervisor with secure remote access. Which two features can you implement on Edge-FortiGate? (Choose two answers)
Based on the exhibit and the OT Security 7.6 Architect standards for Secure Remote Access:
Secure Tunneling (Statement A): The exhibit shows a Remote PC connecting through a VPN Cloud to the Edge-FortiGate. In the Fortinet architecture, IPsec VPN is the primary method for establishing a secure, encrypted tunnel for remote administrators or supervisors to access the internal OT segments (Level 2/3) from an external location.
Multi-Factor Authentication (Statement B): Secure remote access in OT environments (aligned with IEC 62443 standards) requires strong authentication. The study guide emphasizes the use of FortiToken to provide Two-Factor Authentication (2FA) for VPN users, ensuring that compromised credentials alone are not enough to gain access to critical infrastructure.
FSSO (Statement D): Fortinet Single Sign-On is generally used for identifying internal users already on the network to apply identity-based policies; it is not the primary mechanism for establishing the remote connection itself.
SD-WAN (Statement C): While SD-WAN can manage the path of the VPN traffic, it is a WAN optimization and reliability feature, not a 'secure remote access' feature for a supervisor in the context of authentication and encryption.