
What is the BEST alternative if you discover that a rootkit has been installed on one of your computers?
If a rootkit is discovered, you will need to reload from known good media. This typically means performing a complete reinstall.
Exam dumps demo
Preview page 1 of 175 with real questions 1 to 5 from the full 877-question GAQM set.
The GAQM CPEH-001 - Certified Professional Ethical Hacker (CPEH) Exam is part of the GAQM Certified Ethical Hacker certification path. It is designed for candidates who want to validate their knowledge of ethical hacking concepts and practical security awareness. This exam is a strong choice for learners and professionals who want to strengthen their understanding of defensive and offensive security topics. Earning this certification can help demonstrate readiness for real-world cybersecurity responsibilities.
| # | Exam Topics | Sub-Topics | Approximate Weightage (%) |
|---|---|---|---|
| 1 | Module Information - 1 | Core ethical hacking concepts, security fundamentals, attack surface awareness | 34% |
| 2 | Module Information - 2 | Reconnaissance methods, vulnerability identification, scanning techniques, basic exploitation awareness | 33% |
| 3 | Module Information - 3 | Web and system security testing, mitigation concepts, reporting, and remediation best practices | 33% |
The exam tests how well candidates understand ethical hacking principles, security assessment logic, and practical decision-making across common attack and defense scenarios. It also checks depth of knowledge, attention to detail, and the ability to apply concepts in a structured way. Strong preparation should focus on both theory and hands-on awareness so you can answer questions accurately under time pressure.
What is the BEST alternative if you discover that a rootkit has been installed on one of your computers?
If a rootkit is discovered, you will need to reload from known good media. This typically means performing a complete reinstall.
What are the two basic types of attacks? (Choose two.
Passive and active attacks are the two basic types of attacks.
A pentester is using Metasploit to exploit an FTP server and pivot to a LAN. How will the pentester pivot using Metasploit?
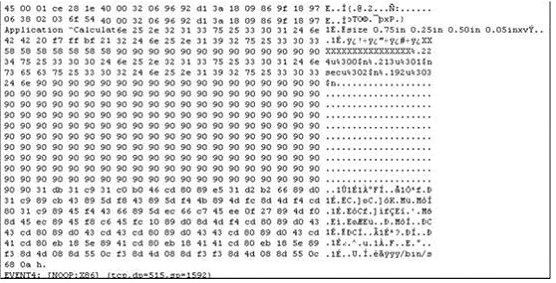
Exhibit:

The following is an entry captured by a network IDS.You are assigned the task of analyzing this entry. You notice the value 0x90, which is the most common NOOP instruction for the Intel processor. You figure that the attacker is attempting a buffer overflow attack. You also notice "/bin/sh" in the ASCII part of the output. As an analyst what would you conclude about the attack?
This log entry shows a hacker using a buffer overflow to fill the data buffer and trying to insert the execution of /bin/sh into the executable code part of the thread. It is probably an existing exploit that is used, or a directed attack with a custom built buffer overflow with the ''payload'' that launches the command shell.
Joseph has just been hired on to a contractor company of the Department of Defense as their Senior Security Analyst. Joseph has been instructed on the company's strict security policies that have been implemented, and the policies that have yet to be put in place. Per the Department of Defense, all DoD users and the users of their contractors must use two-factor authentication to access their networks. Joseph has been delegated the task of researching and implementing the best two-factor authentication method for his company. Joseph's supervisor has told him that they would like to use some type of hardware device in tandem with a security or identifying pin number. Joseph's company has already researched using smart cards and all the resources needed to implement them, but found the smart cards to not be cost effective. What type of device should Joseph use for two-factor authentication?
Full exam access, validated answers, and unlimited practice with no download limits.
QA4Exam.com offers Exam PDF materials with actual questions and answers plus an Online Practice Test for the GAQM CPEH-001 exam. These resources help you experience a realistic exam simulation, so you can become familiar with the style and pace of the questions before test day. The verified answers and up-to-date questions make it easier to focus on the most relevant exam content. The practice test also helps you build time management skills, identify weak areas, and improve confidence for first-attempt success. With both formats, you can study in a way that is practical, efficient, and focused on passing.
It is the GAQM CPEH-001 exam for the GAQM Certified Ethical Hacker certification path, focused on ethical hacking knowledge and security awareness.
It can be challenging because it tests both knowledge and practical understanding, so focused preparation is important.
Braindumps alone are not the best approach. You should use them with review and practice to understand the concepts behind the answers.
Hands-on experience is helpful because it improves your understanding of ethical hacking topics and makes the exam content easier to apply.
The Exam PDF and Online Practice Test are strong preparation tools, and many candidates also review their notes or related study material for better understanding.
They help you practice real exam-style questions, manage time better, and review verified answers so you can enter the exam with more confidence.
QA4Exam.com provides an Exam PDF with actual questions and answers and an Online Practice Test that simulates the exam experience.