
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

HPE6-A84 Exam Dumps and Practice Questions

Preview page 1 of 12 with real questions 1 to 5 from the full 60-question HP set.

Most Recent HPE6-A84 Exam Dumps


Prepare for the HP Aruba Certified Network Security Expert Written Exam exam with our extensive collection of questions and answers. These practice Q&A are updated according to the latest syllabus, providing you with the tools needed to review and test your knowledge.

QA4Exam focus on the latest syllabus and exam objectives, our practice Q&A are designed to help you identify key topics and solidify your understanding. By focusing on the core curriculum, These Questions & Answers helps you cover all the essential topics, ensuring you're well-prepared for every section of the exam. Each question comes with a detailed explanation, offering valuable insights and helping you to learn from your mistakes. Whether you're looking to assess your progress or dive deeper into complex topics, our updated Q&A will provide the support you need to confidently approach the HPE6-A84 exam and achieve success.

Actual HP HPE6-A84 Exam Questions

Question 1

Refer to the scenario.

A customer has an AOS10 architecture that is managed by Aruba Central. Aruba infrastructure devices authenticate clients to an Aruba ClearPass cluster.

In Aruba Central, you are examining network traffic flows on a wireless IoT device that is categorized as ''Raspberry Pi'' clients. You see SSH traffic. You then check several more wireless IoT clients and see that they are sending SSH also.

You want an easy way to communicate the information that an IoT client has used SSH to Aruba ClearPass Policy Manager (CPPM).

What step should you take?

Correct answer: A

This is because an Endpoint Context Server (ECS) is a feature that allows ClearPass to receive contextual information from external sources, such as Aruba Central, and use it for policy enforcement and reporting. An ECS can be configured to point to the Aruba Central API and fetch data such as device type, category, OS, applications, traffic flows, etc.

An ECS can be used to communicate the information that an IoT client has used SSH to Aruba ClearPass Policy Manager (CPPM). The ECS can query the Aruba Central API and retrieve the network traffic flows of the wireless IoT devices that are categorized as ''Raspberry Pi'' clients. The ECS can then filter the traffic flows by the SSH protocol and send the relevant information to CPPM. CPPM can then use this information for policy decisions, such as allowing or denying SSH access, or triggering alerts or actions.

B) On CPPM enable Device Insight integration. This is not a valid step because Device Insight is a feature that allows ClearPass to discover, profile, and fingerprint devices on the network using deep packet inspection (DPI) and machine learning (ML). Device Insight does not communicate with Aruba Central or receive information from it. Moreover, Device Insight might not be able to detect SSH traffic on encrypted wireless IoT devices without decrypting it first.

C) On Central configure APs and gateways to use CPPM as the RADIUS accounting server. This is not a valid step because RADIUS accounting is a feature that allows network devices to send periodic updates about the status and activity of authenticated users or devices to a RADIUS server, such as CPPM. RADIUS accounting does not communicate with Aruba Central or receive information from it. Moreover, RADIUS accounting might not be able to capture SSH traffic on wireless IoT devices without inspecting it first.

D) On Central set up CPPM as a Webhook application. This is not a valid step because Webhook is a feature that allows Aruba Central to send notifications or events to external applications or services using HTTP requests. Webhook does not communicate with CPPM or send information to it. Moreover, Webhook might not be able to send SSH traffic information on wireless IoT devices without filtering it first.

Question 2

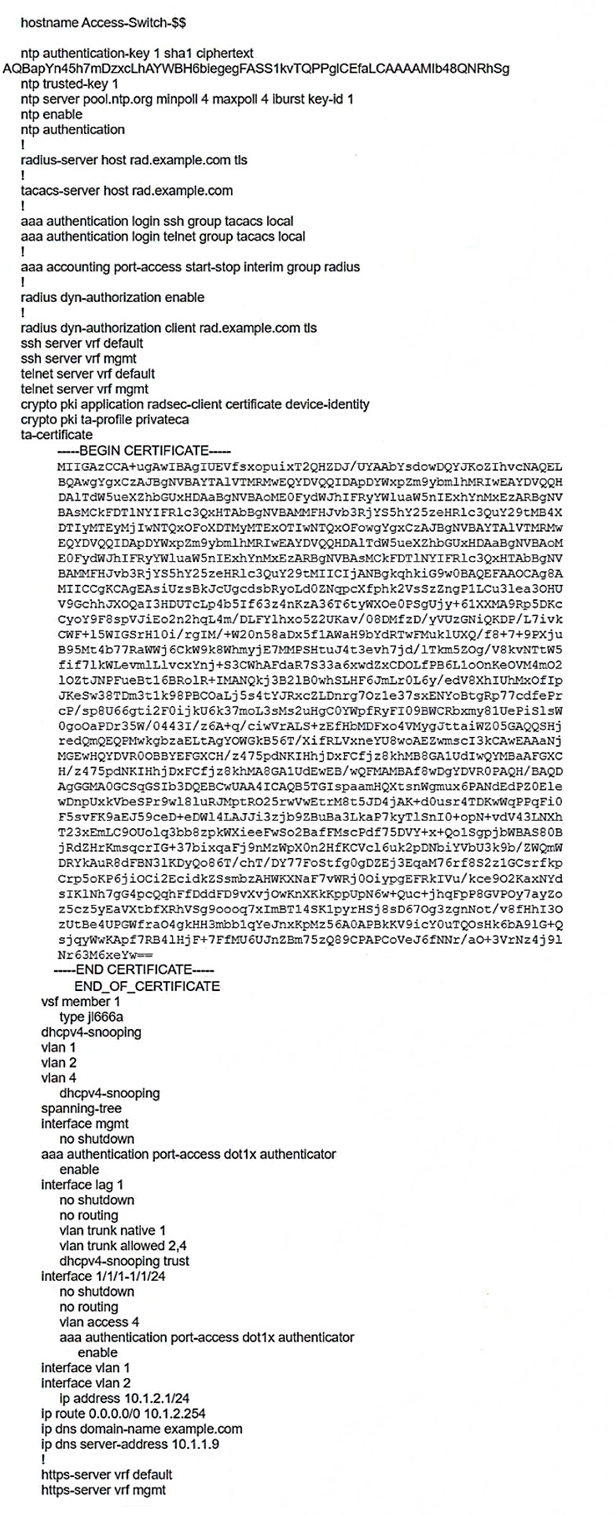
Refer to the scenario.

A customer has asked you to review their AOS-CX switches for potential vulnerabilities. The configuration for these switches is shown below:

What is one immediate remediation that you should recommend?

Question 3

Refer to the scenario.

An organization wants the AOS-CX switch to trigger an alert if its RADIUS server (cp.acnsxtest.local) rejects an unusual number of client authentication requests per hour. After some discussions with other Aruba admins, you are still not sure how many rejections are usual or unusual. You expect that the value could be different on each switch.

You are helping the developer understand how to develop an NAE script for this use case.

The developer explains that they plan to define the rule with logic like this:

monitor > value

However, the developer asks you what value to include.

What should you recommend?

Correct answer: D

This is because a parameter is a variable that can be defined and modified by the user or the script, and can be used to customize the behavior and output of the NAE script. A parameter can be referred to by using the syntax self ^ramsfname], where ramsfname is the name of the parameter.

By defining a parameter for the value, the developer can make the NAE script more flexible and adaptable to different scenarios and switches. The parameter can be set to a default value, such as 10, but it can also be changed by the user or the script based on the network conditions and requirements. For example, the parameter can be adjusted dynamically based on the average or standard deviation of the number of rejects per hour, or based on the feedback from the user or other admins. This way, the NAE script can trigger an alert only when the number of rejects is truly unusual and not just arbitrary.

A) Checking one of the access switches' RADIUS statistics and adding 10 to the number listed for rejects. This is not a good recommendation because it does not account for the variability and diversity of the network environment and switches. The number of rejects listed for one switch might not be representative or relevant for another switch, as different switches might have different traffic patterns, client types, RADIUS configurations, etc. Moreover, adding 10 to the number of rejects is an arbitrary and fixed value that might not reflect the actual threshold for triggering an alert.

B) Defining a baseline and referring to it for the value. This is not a bad recommendation, but it is not as good as defining a parameter. A baseline is a reference point that represents the normal or expected state of a network metric or performance indicator. A baseline can be used to compare and contrast the current network situation and detect any anomalies or deviations. However, a baseline might not be easy or accurate to define, as it might require historical data, statistical analysis, or expert judgment. Moreover, a baseline might not be stable or constant, as it might change over time due to network growth, evolution, or optimization.

C) Using 10 (per hour) as a good starting point for the value. This is not a good recommendation because it is an arbitrary and fixed value that might not reflect the actual threshold for triggering an alert. Using 10 (per hour) as the value might result in false positives or false negatives, depending on the network conditions and switches. For example, if the normal number of rejects per hour is 5, then using 10 as the value might trigger an alert too frequently and unnecessarily. On the other hand, if the normal number of rejects per hour is 15, then using 10 as the value might miss some important alerts and risks.


Question 4

You are designing an Aruba ClearPass Policy Manager (CPPM) solution for a customer. You learn that the customer has a Palo Alto firewall that filters traffic between clients in the campus and the data center.

Which integration can you suggest?

Question 5

A customer's admins have added RF Protect licenses and enabled WIDS for a customer's AOS 8-based solution. The customer wants to use the built-in capabilities of APs without deploying dedicated air monitors (AMs). Admins tested rogue AP detection by connecting an unauthorized wireless AP to a switch. The rogue AP was not detected even after several hours.

What is one point about which you should ask?

Correct answer: C

RF Protect is a feature that enables wireless intrusion detection and prevention system (WIDS/WIPS) capabilities on AOS 8-based solutions. WIDS/WIPS allows detecting and mitigating rogue APs, unauthorized clients, and other wireless threats. RF Protect requires RF Protect licenses to be installed and WIDS to be enabled on the Mobility Master (MM).

To use the built-in capabilities of APs for WIDS/WIPS, without deploying dedicated air monitors (AMs), admins need to set at least one radio on each AP to air monitor mode. Air monitor mode allows the AP to scan the wireless spectrum and report any wireless activity or anomalies to the MM. Air monitor mode does not affect the other radio on the AP, which can still serve clients in access mode. By setting at least one radio on each AP to air monitor mode, admins can achieve full coverage and visibility of the wireless environment and detect rogue APs.

If admins do not set any radio on the APs to air monitor mode, the APs will not scan the wireless spectrum or report any wireless activity or anomalies to the MM. This means that the APs will not be able to detect rogue APs, even if they are connected to the same network. Therefore, admins should check whether they have set at least one radio on each AP to air monitor mode.


Unlock all HP HPE6-A84 questions

Full exam access, validated answers, and unlimited practice with no download limits.