
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

CIPT Exam Dumps and Practice Questions

Preview page 1 of 44 with real questions 1 to 5 from the full 220-question IAPP set.

IAPP CIPT Dumps - Pass Certified Information Privacy Technologist Exam in 2026

The IAPP CIPT exam, Certified Information Privacy Technologist, is part of the IAPP Certification Programs and is designed for professionals who work at the intersection of privacy and technology. It focuses on the skills and knowledge needed to support privacy requirements within systems, products, and processes. This certification matters because it helps demonstrate that you understand how to apply privacy principles in technical environments. It is valuable for candidates who want to strengthen their privacy engineering and technology-focused privacy expertise.

# Exam Topics Sub-Topics Approximate Weightage (%)
1 Foundational principles Privacy concepts, core terminology, data protection basics, legal and ethical foundations 15%
2 The privacy technologist's role in the context of the organization Stakeholder collaboration, governance support, policy alignment, communication with business and technical teams 15%
3 Privacy risks, threats and violations Risk identification, threat scenarios, violation impacts, incident awareness and response considerations 20%
4 Privacy-enhancing strategies, techniques and technologies Data minimization, access controls, encryption concepts, anonymization and pseudonymization 15%
5 Privacy engineering Requirements analysis, technical controls, implementation planning, testing and validation 15%
6 Privacy by design Design principles, lifecycle integration, default settings, embedding privacy into products and services 10%
7 Evolving or emerging technologies in privacy New technology trends, privacy implications, adaptive controls, future-focused privacy considerations 10%

The exam tests more than memorization. It measures how well candidates understand privacy concepts, how they apply privacy thinking in technical settings, and how they respond to real-world risks and design challenges. Strong preparation should include practical awareness, conceptual clarity, and the ability to choose appropriate privacy-focused solutions.

Actual IAPP CIPT Exam Questions

Question 1

SCENARIO

Please use the following to answer the next question:

Light Blue Health (LBH) is a healthcare technology company developing a new web and mobile application that collects personal health information from electronic patient health records. The application will use machine learning to recommend potential medical treatments and medications based on information collected from anonymized electronic health records. Patient users may also share health data collected from other mobile apps with the LBH app.

The application requires consent from the patient before importing electronic health records into the application and sharing it with their authorized physicians or healthcare provider. The patient can then review and share the recommended treatments with their physicians securely through the app. The patient user may also share location data and upload photos in the app. The patient user may also share location data and upload photos in the app for a healthcare provider to review along with the health record. The patient may also delegate access to the app.

LBH's privacy team meets with the Application development and Security teams, as well as key business stakeholders on a periodic basis. LBH also implements Privacy by Design (PbD) into the application development process.

The Privacy Team is conducting a Privacy Impact Assessment (PIA) to evaluate privacy risks during development of the application. The team must assess whether the application is collecting descriptive, demographic or any other user related data from the electronic health records that are not needed for the purposes of the application. The team is also reviewing whether the application may collect additional personal data for purposes for which the user did not provide consent.

What is the best way to ensure that the application only collects personal data that is needed to fulfill its primary purpose of providing potential medical and healthcare recommendations?

Correct answer: D

Primary Purpose Principle: Ensuring that data collection is strictly for fulfilling the primary purpose helps in maintaining data minimization and relevance.

Mapping Data to Functionality: Documenting each personal data category and mapping it to specific app functions or features ensures that only the necessary data is collected and used. This approach adheres to the principle of data minimization, a core aspect of Privacy by Design.

Data Inventory and Mapping: Creating a comprehensive data inventory that links each piece of personal data to its specific use case in the application helps in justifying the necessity of data collection and provides transparency.

Reference: The IAPP guidelines on conducting Privacy Impact Assessments (PIAs) highlight the importance of data mapping in identifying and documenting the personal data collected and ensuring it aligns with the application's functionalities and purposes.

Question 2

SCENARIO

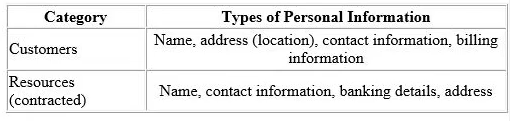
Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephone, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q's business model, resources are contracted as needed instead of permanently employed.

The table below indicates some of the personal information Clean-Q requires as part of its business operations:

Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation. Therefore, the Clean-Q permanent employee base is not included as part of this scenario.

With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q's traditional supply and demand system that has caused some overlapping bookings.

Ina business strategy session held by senior management recently, Clear-Q invited vendors to present potential solutions to their current operational issues. These vendors included Application developers and Cloud-Q's solution providers, presenting their proposed solutions and platforms.

The Managing Director opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform: A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information.

A customer facing web interface that enables customers to register, manage and submit cleaning service requests online.

A resource facing web interface that enables resources to apply and manage their assigned jobs.

An online payment facility for customers to pay for services.

Considering that LeadOps will host/process personal information on behalf of Clean-Q remotely, what is an appropriate next step for Clean-Q senior management to assess LeadOps' appropriateness?

Correct answer: D

Given that LeadOps will host/process personal information on behalf of Clean-Q remotely, it is crucial to involve the Information Security team to understand in more detail the types of services and solutions LeadOps is proposing.

Security Assessment: The Information Security team should evaluate LeadOps' security measures, data protection practices, and compliance with relevant regulations. This assessment ensures that the service provider has adequate safeguards to protect personal information.

Risk Management: Understanding the security environment helps identify potential risks associated with outsourcing data processing. This includes assessing encryption practices, data storage policies, and incident response plans.

Legal and Compliance Considerations: Involving the Information Security team ensures that Clean-Q adheres to data protection regulations such as GDPR or CCPA, which require businesses to ensure their processors provide adequate data protection.


IAPP Privacy Management, Information Privacy Technologist Certification Textbooks

ISO/IEC 27001 -- Information Security Management Systems

GDPR Articles 28 and 32

Question 3

Which of the following occurs when an individual takes a specific observable action to indicate and confirm that they give permission for their information to be processed?

Correct answer: A

Option A: Express consent occurs when an individual takes a specific, observable action, such as signing a document or clicking an 'I agree' button online, to give explicit permission for their information to be processed. This type of consent is clear and unambiguous.

Option B: Implied consent is inferred from an individual's actions, such as when they provide information voluntarily without a specific action indicating consent.

Option C: Informed notice refers to providing individuals with information about how their data will be used, but it does not itself constitute consent.

Option D: Authorized notice is not a standard term in data protection and privacy contexts.


IAPP CIPT Study Guide

GDPR Article 4(11) Definitions on Consent

Question 4

In terms of data extraction, which of the following should NOT be considered by a privacy technologist in relation to data portability?

Correct answer: A

In relation to data portability, the size of the data should not be a primary consideration for a privacy technologist. Data portability focuses on enabling individuals to easily transfer their personal data between different service providers. The key factors to consider are the format of the data, ensuring it is in an interoperable and machine-readable format; the range of the data, covering the scope of data to be transferred; and the medium of the data, ensuring secure and efficient transfer mechanisms. According to IAPP, while data size might affect technical implementation, it is not a primary concern in ensuring compliance with data portability requirements under regulations like the GDPR.


Question 5

Which of the following entities would most likely be exempt from complying with the General Data Protection Regulation (GDPR)?

Correct answer: D

The General Data Protection Regulation (GDPR) applies to entities that process personal data of individuals within the European Union, regardless of where the processing takes place. In this scenario, the North American company is servicing customers in South Africa and, although it uses a cloud storage system made by a European company, it is not directly involved in the processing of personal data of EU citizens. Therefore, it is most likely exempt from complying with the GDPR. Reference: GDPR Article 3 (Territorial Scope), IAPP Certification Textbooks, Section on GDPR Applicability.


Unlock all IAPP CIPT questions

Full exam access, validated answers, and unlimited practice with no download limits.

Frequently Asked Questions

What is the IAPP CIPT exam?

The IAPP CIPT exam is the Certified Information Privacy Technologist exam under IAPP Certification Programs. It is aimed at candidates who work with privacy in technical environments and want to validate privacy technology knowledge.

Who should take the CIPT exam?

It is a strong fit for privacy technologists, technical privacy professionals, and candidates who support privacy in systems, products, and processes. It is also useful for professionals who want to show practical privacy engineering knowledge.

Is the CIPT exam difficult?

The exam can be challenging because it covers both privacy concepts and technical application. Candidates who study the topics carefully and practice with realistic questions usually feel more prepared.

Can I pass with only braindumps?

Braindumps alone are not a complete preparation strategy. You should use them as part of a broader study plan that includes understanding the concepts, reviewing the topics, and practicing with exam-style questions.

Do I need hands-on experience for CIPT?

Hands-on experience is very helpful because the exam focuses on practical privacy technology thinking. Even if you have limited experience, focused study and practice can help you build the needed understanding.

Are the QA4Exam.com dumps enough to pass on the first attempt?

The Exam PDF and Online Practice Test can greatly improve your readiness, especially when used consistently. They help you learn question patterns, verify answers, and practice time management, which supports first-attempt success.

What format do the QA4Exam.com materials use?

QA4Exam.com offers an Exam PDF with actual questions and answers and an Online Practice Test for interactive preparation. These formats are useful for review, self-assessment, and real exam simulation.

How do the practice test and PDF help with time management?

The practice test lets you work through questions under exam-like conditions, which helps you improve pacing. The PDF also supports repeated review so you can answer faster and more confidently on test day.