Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

JN0-232 Exam Dumps and Practice Questions

Questions 1 to 5 of the 110-question JN0-232 bank, each with its correct answer and an explanation. 4 of 5 ask for more than one answer. This is page 1 of 22.

1 / 22

Actual Juniper JN0-232 Exam Questions

Question 1

Which two statements are true about the NextGen Web Filtering (NGWF) feature on an SRX Series device? (Choose two.)

Correct answer: B, C

License Requirement (Option B): NextGen Web Filtering (NGWF) is a licensed feature on SRX devices. Without a license, the service cannot operate.

Local vs. Cloud Lists (Option C): NGWF checks local block/allow lists first. If the URL does not match locally, the request is then checked against the Juniper cloud database.

Option A: Incorrect, since the cloud is only consulted if the URL is not in the local list.

Option D: Incorrect, as NGWF requires a valid subscription/license.

Correct Statements: NGWF requires a license, and it checks local lists before cloud lookup.

Question 2

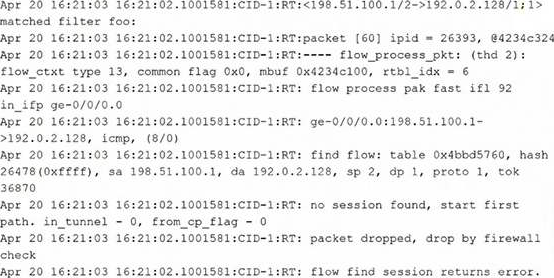
Your manager asks you to ping 192.0.2.128. The ping fails and you do not know why, so you enable a trace option on your SRX Series Firewall.

Referring to the exhibit, what is the reason for this behavior?

Correct answer: D

The trace output shows that the SRX receives the ICMP packet, does not find an existing session, starts first path processing, and then drops the packet with a firewall check failure before a session is successfully created. In SRX troubleshooting, first path processing includes route lookup, policy evaluation, and session creation. If the device cannot determine a valid forwarding path for the destination, the session cannot be established and the packet is dropped. The exhibit does not show evidence of a web filtering decision, ALG processing, or a screen counter match. Therefore, the best answer is that there is no known route to the destination 192.0.2.128. The appropriate operational verification would be to check the routing table using a command such as show route 192.0.2.128.


Question 3

Click the Exhibit button.

Referring to the exhibit, which two statements are correct? (Choose two.)

Correct answer: A, B

From the exhibit:

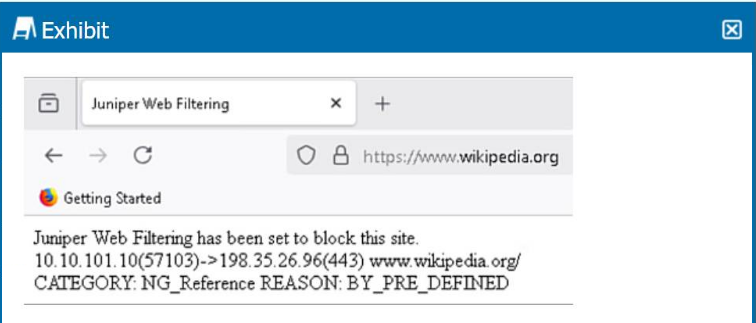
The user attempted to access https://www.wikipedia.org.

The block page indicates:

CATEGORY: NG_Reference

REASON: BY_PRE_DEFINED

The header states: ''Juniper Web Filtering has been set to block this site.''

Analysis of options:

Option A: Correct. The log shows ''REASON: BY_PRE_DEFINED,'' which means the site was blocked because it matched a predefined category in the Web filtering database.

Option B: Correct. The category ''NG_Reference'' indicates that the NextGen (Enhanced/Cloud-based) Web Filtering type is being used.

Option C: Incorrect. The exhibit does not provide any information about SSL proxy configuration; it only shows that the HTTPS site was blocked.

Option D: Incorrect. The block page shown is the standard Juniper default block page, not a custom message.

Correct Statements: The URL matches a predefined Web filtering category, and the NextGen Web Filtering type is being used.


Question 4

Which two statements correctly describe static NAT? (Choose two.)

Correct answer: A, C

Static NAT creates a fixed one-to-one mapping between real and mapped addresses. Juniper documentation describes static NAT as mapping one IP subnet to another IP subnet and states that translation is limited to one-to-one mappings or address blocks of the same size. This makes option A correct. Juniper also states that no address pools are necessary for static NAT, which makes option C correct. Address pools are commonly associated with source NAT or destination NAT pool configurations, not the basic static NAT mapping model. Static NAT can support static port mapping in specific configurations, but the general static NAT behavior tested here is one-to-one address translation, not dynamic PAT. Therefore, the correct answers are A and C.


Question 5

You need to ensure that the security policy is configured correctly for a flow with both source NAT and destination NAT involved. In this scenario, which two match conditions are valid for source and destination addresses? (Choose two.)

Correct answer: A, B

When both source NAT and destination NAT are involved, the security policy must match addresses according to Junos NAT processing order. Juniper documents that static NAT and destination NAT are processed before route lookup and security policy lookup, while source NAT is processed after route and security policy lookup. This means that by the time policy evaluation occurs, the destination address has already been translated by destination NAT. However, the source address has not yet been translated by source NAT. Therefore, the correct policy match conditions are the post-NAT destination address and the pre-NAT source address. Matching on the pre-NAT destination or post-NAT source would not align with Junos SRX processing order.


Unlock all Juniper JN0-232 questions

Full exam access, validated answers, and unlimited practice with no download limits.