Question 1
Referring to the exhibit,
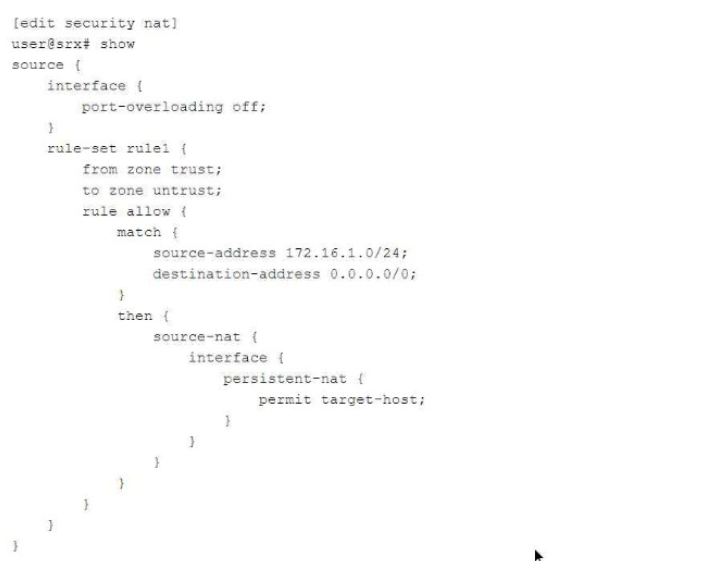
which two statements are correct about the NAT configuration? (Choose two.)
Correct answer:
A, B

Exam dumps demo
Preview page 1 of 23 with real questions 1 to 5 from the full 115-question Juniper set.
The Juniper JN0-637 - Security, Professional exam is part of the Juniper Junos Security Certification and is designed for professionals who work with advanced security features in Juniper environments. It evaluates the ability to configure, secure, and troubleshoot complex network security solutions with confidence. This certification matters for engineers who want to validate practical skills in security policy control, VPNs, high availability, and threat mitigation. Passing this exam shows that you can handle real-world Juniper security deployments at a professional level.
| # | Exam Topics | Sub-Topics | Approximate Weightage (%) |
|---|---|---|---|
| 1 | Advanced Policy-Based Routing (APBR) | Route selection policies, traffic steering, rule evaluation, policy verification | 12% |
| 2 | Advanced IPsec VPNs | Tunnel configuration, security associations, phase 1 and phase 2 concepts, VPN troubleshooting | 16% |
| 3 | Layer 2 Security | Port security, MAC filtering, protection against spoofing, L2 enforcement controls | 12% |
| 4 | Advanced Network Address Translation (NAT) | Source NAT, destination NAT, rule order, address translation behavior, verification | 14% |
| 5 | Logical Systems and Tenant Systems | Segmentation models, resource separation, system hierarchy, operational context | 10% |
| 6 | Troubleshooting Security Policies and Security Zones | Policy matching, zone relationships, traffic flow analysis, logging and validation | 16% |
| 7 | Multinode High Availability (HA) | Redundancy design, failover behavior, node coordination, HA validation | 10% |
| 8 | Automated Threat Mitigation | Threat detection, response actions, mitigation policies, event handling | 10% |
| Total | 100% | ||
Referring to the exhibit,
which two statements are correct about the NAT configuration? (Choose two.)
You want to configure the SRX Series device to map two peer interfaces together and ensure that there is no switching or routing lookup to forward traffic.
Which feature on the SRX Series device is used to accomplish this task?
Comprehensive Detailed Step-by-Step Explanation with All Juniper Security Reference
Understanding Secure Wire:
Secure Wire Feature:
Connects two interfaces directly without any Layer 2 or Layer 3 processing.
No routing or switching lookup occurs.
Use Case:
Ideal for scenarios where traffic needs to pass through the SRX device transparently.
Option B: Secure wire
Secure wire creates a bidirectional link between two interfaces.
Traffic flows between the interfaces as if they are connected by a physical wire.
'The secure wire feature allows traffic to pass between two interfaces without any security processing or route lookups.'
Source: Juniper TechLibrary - Secure Wire Overview
Why Other Options Are Incorrect:
Option A: Transparent mode involves Layer 2 switching.
Option C: Mixed mode combines Layer 2 and Layer 3 but doesn't prevent switching/routing lookups.
Option D: Switching mode operates at Layer 2 and includes switching lookups.
Conclusion:
Secure wire is the correct feature to map two interfaces together without switching or routing lookups.
Exhibit:
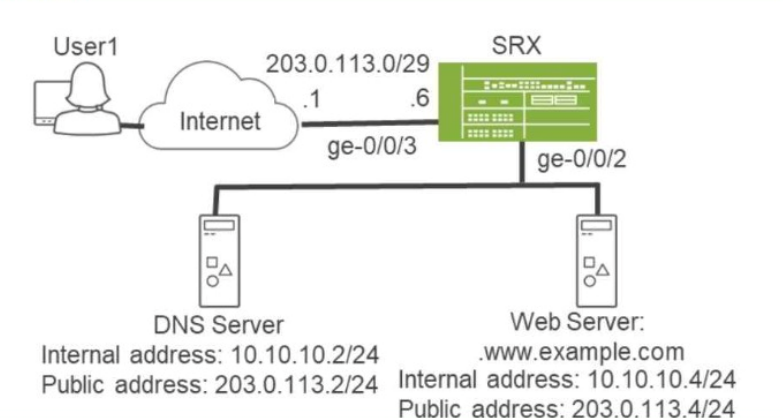
You are asked to ensure that Internet users can access the company's internal webserver using its FQDN. However, the internal DNS server's A record only points to the webserver's private address.
Referring to the exhibit, which two actions are required to complete this task? (Choose two.)
In the scenario where internal users are trying to access the company's web server via its FQDN but the DNS server resolves to a private IP, two key actions are needed:
Static NAT (Answer B): Since the internal DNS server resolves the web server to its private IP address (10.10.10.4/24), you need to configure static NAT for both the DNS server and the webserver. This will ensure that requests coming from the internet will be translated to the web server's public IP (203.0.113.4) and the DNS server's public IP (203.0.113.2).
Example Command:
bash
set security nat static rule-set public-to-private from zone untrust
set security nat static rule-set public-to-private rule dns-server match destination-address 203.0.113.2/32
set security nat static rule-set public-to-private rule dns-server then static-nat-prefix 10.10.10.2/32
set security nat static rule-set public-to-private rule web-server match destination-address 203.0.113.4/32
set security nat static rule-set public-to-private rule web-server then static-nat-prefix 10.10.10.4/32
Proxy ARP (Answer D): The SRX needs to respond to ARP requests for the public IP addresses of both the DNS and webserver on the interface facing the internet (ge-0/0/3). This allows the SRX to handle requests directed at the public IPs.
Example Command:
set interfaces ge-0/0/3 unit 0 family inet proxy-arp interface-address 203.0.113.2/32
set interfaces ge-0/0/3 unit 0 family inet proxy-arp interface-address 203.0.113.4/32
These two configurations allow external users to access the internal web server via its public IP, as resolved by the DNS server.
Your customer needs embedded security in an EVPN-VXLAN solution.
What are two benefits of adding an SRX Series device in this scenario? (Choose two.)
The SRX Series can inspect traffic within VXLAN tunnels, providing in-depth security services across multiple layers. Adding SRX in the overlay network allows comprehensive control, leveraging advanced firewall capabilities. For more details, see Juniper EVPN-VXLAN Security.
When integrating an SRX Series device into an EVPN-VXLAN solution, it offers several security benefits:
Layer 4-7 Security Services (Answer A): The SRX can provide deep packet inspection for VXLAN encapsulated traffic, enhancing security by offering services such as intrusion prevention, application layer filtering, and antivirus scanning. This allows security monitoring of the encapsulated traffic at higher layers of the OSI model (Layers 4-7), which is essential for advanced threat detection.
Security in the Overlay Network (Answer C): The SRX adds security by functioning as an enterprise-grade firewall within the EVPN-VXLAN overlay. This means that traffic flowing between virtualized segments or networks can be inspected and filtered using SRX firewall rules, ensuring that the VXLAN overlay remains secure.
These features make the SRX a powerful addition for securing EVPN-VXLAN environments, providing comprehensive security for encapsulated traffic and ensuring that both the underlay and overlay networks are protected.
You configured two SRX series devices in an active/passive multimode HA setup.
In this scenario, which statement is correct?
Full exam access, validated answers, and unlimited practice with no download limits.
This exam tests more than memorization. Candidates must understand how Juniper security features work together, how to apply them in practical scenarios, and how to troubleshoot issues under exam pressure. It also checks your ability to interpret traffic behavior, validate configuration outcomes, and choose the right security control for a given situation. Strong hands-on knowledge is important because the exam focuses on applied skills and operational decision-making.
QA4Exam.com offers the JN0-637 Exam PDF with actual questions and answers, along with an Online Practice Test that helps you prepare in a focused and efficient way. The practice format gives you a real exam simulation so you can get familiar with the question style and pace. You also benefit from up-to-date questions and verified answers that support accurate revision before the test. By practicing with timed sessions, you improve time management and build confidence for the actual Juniper JN0-637 exam. This combination can help you prepare smarter and aim for a first attempt pass.
It is intended for professionals working with Juniper security solutions who want to validate advanced knowledge in security policies, VPNs, NAT, HA, and threat mitigation.
Yes, it can be challenging because it focuses on practical understanding and troubleshooting, not just basic theory. Strong hands-on preparation is important.
Braindumps alone are not the best approach. They are most effective when used with real study and hands-on practice so you understand the concepts behind the answers.
Yes, hands-on experience is highly recommended because the exam includes troubleshooting, configuration behavior, and practical security scenarios.
They are very helpful for focused revision, exam pattern familiarity, and answer verification, but combining them with study and practical experience gives the best chance of first attempt success.
The practice format is built to simulate the exam experience, and the PDF version provides actual questions and answers for revision. Both are designed to support efficient preparation.
Yes, timed practice helps you manage pace, reduce pressure, and improve confidence before taking the real exam.