Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

SC-300 Exam Dumps and Practice Questions

Preview page 1 of 77 with real questions 1 to 5 from the full 383-question Microsoft set.

Microsoft SC-300 Dumps - Pass Microsoft Identity and Access Administrator Exam in 2026

The Microsoft SC-300 exam, also known as Microsoft Identity and Access Administrator, is part of the Microsoft Azure certification track. It is designed for professionals who manage identity solutions, authentication, access, and governance in modern cloud environments. This exam matters because identity is the foundation of secure access across Azure services and enterprise applications. Passing SC-300 validates that you can support secure and efficient identity management for an organization.

Exam Topics and Approximate Weightage

# Exam Topics Sub-Topics Approximate Weightage (%)
1 Implement and manage user identities Create and manage users, manage groups, assign licenses, manage external users 25
2 Implement authentication and access management Configure authentication methods, manage conditional access, implement MFA, secure sign-in access 30
3 Plan and implement workload identities Register applications, manage service principals, configure app permissions, manage managed identities 20
4 Plan and implement identity governance Configure access reviews, entitlement management, privileged identity management, lifecycle processes 25

Actual Microsoft SC-300 Exam Questions

Question 1

You need to allocate licenses to the new users from

Correct answer: B

In Azure AD, license automation is implemented through group-based licensing. The SC-300 materials explain that ''you can assign licenses to a group in Azure Active Directory; when you assign a license to a group, all users who are members of the group are assigned that license''. They also clarify that ''dynamic group membership uses rules to automatically add or remove users based on user attributes'', which is the recommended way to on-board new populations without manual effort. For licensing, the guide is explicit that ''group-based licensing works with security groups and Microsoft 365 Groups'' and that ''distribution lists are not supported for license assignment''. Administrative Units are described as ''a scoping mechanism for delegating administrative permissions to subsets of users and devices'', not a licensing entity. Likewise, Organizational Units (OUs) are on-premises AD containers and ''do not control license assignment in Azure AD''.

Given the requirement to allocate licenses automatically to new A. Datum users as they appear, the least-effort, policy-driven approach is to create an Azure AD Dynamic User security group with a membership rule that targets those users (for example, by domain, company attribute, or a synced attribute), then assign the required Microsoft 365/Azure AD licenses to that group. As the documentation notes, ''when users join or leave the group based on the rule, licenses are added or removed automatically.''


Question 2

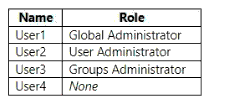
You have a Microsoft 365 subscription that contains the users shown in the following table.

From the tenan1, you configure a naming policy for groups.

Which users are affected by the naming policy?

Correct answer: D

According to the Microsoft Identity and Access Administrator (SC-300) Study Guide and the Microsoft Learn -- ''Manage Microsoft 365 Groups naming policies'' documentation, group naming policies in Azure Active Directory (now Microsoft Entra ID) apply to end users who create Microsoft 365 groups, but do not apply to administrators who have roles that allow them to override naming restrictions.

The policy defines conventions such as prefixes, suffixes, blocked words, and enforced naming rules. However, certain administrative roles are exempt from this policy to allow organizational management and automation processes. The exempt roles are:

Global Administrator

User Administrator

These two roles can create Microsoft 365 groups without the naming policy constraints. Other users --- including Groups Administrator and users without administrative roles --- are subject to the naming policy when creating groups.

From the official documentation:

''Naming policies apply to all users who create groups, except for global administrators and user administrators. These roles can create groups that bypass the naming policy restrictions.''

Applying this rule:

User1 (Global Administrator) --- exempt

User2 (User Administrator) --- exempt

User3 (Groups Administrator) --- affected by the policy

User4 (no role) --- affected by the policy


Question 3

You have a Microsoft Entra tenant.

You configure self-service password reset (SSPR) with the following settings:

Require users to register when signing in: Yes

Number of methods required to reset: 1

What is a valid authentication method available to users?

Correct answer: B

Comprehensive and Detailed In-Depth

Let's break this down step by step based on Microsoft Entra ID self-service password reset (SSPR) settings and the available authentication methods, as outlined in Microsoft Identity and Access Administrator documentation.

Understanding Self-Service Password Reset (SSPR) in Microsoft Entra ID:

Self-service password reset (SSPR) allows users to reset their passwords without administrator intervention, improving security and reducing helpdesk workload.

The settings provided are:

Require users to register when signing in: Yes-- Users must register their authentication methods (e.g., phone number, email, security questions) the first time they sign in. This ensures they have methods available for SSPR.

Number of methods required to reset: 1-- Users must verify their identity using one authentication method to reset their password. This is the minimum number of methods required, meaning users must have at least one method registered, and they will use one method during the reset process.

Available Authentication Methods for SSPR:

Microsoft Entra ID SSPR supports a specific set of authentication methods that users can use to verify their identity during a password reset. These methods are configured by the administrator in the Microsoft Entra admin center under 'Password reset' settings.

The default authentication methods available for SSPR include:

Email:Users receive a code sent to an alternate email address.

Mobile phone (SMS):Users receive a code via SMS to their registered mobile phone.

Mobile app code:Users use a code generated by the Microsoft Authenticator app (or another compatible authenticator app).

Mobile app notification:Users receive a push notification in the Microsoft Authenticator app to approve the reset.

Security questions:Users answer predefined security questions they set up during registration.

Important Note:Methods like smartcards, FIDO2 security tokens, and Windows Hello are not supported for SSPR. These methods are typically used for authentication during sign-in (e.g., MFA or passwordless sign-in), not for the SSPR process.

Analysis of the Options:

A . A smartcard:

Smartcards are a form of certificate-based authentication often used for sign-in to Windows devices or VPNs. They require a physical card and a reader, and they are typically used for primary authentication, not for SSPR.

Microsoft Entra ID SSPR does not support smartcards as an authentication method for password reset. Smartcards are not listed as an available method in the SSPR configuration settings.

Conclusion:This is incorrect.

B . A mobile app code:

A mobile app code refers to a time-based one-time password (TOTP) generated by an authenticator app, such as the Microsoft Authenticator app.

This is a supported method for SSPR in Microsoft Entra ID. Users can register the Microsoft Authenticator app (or another compatible app) and use the generated code to verify their identity during a password reset.

Since the setting 'Number of methods required to reset: 1' means only one method is needed, a mobile app code is a valid option if the user has registered it.

Conclusion:This is correct.

C . An FIDO2 security token:

FIDO2 security tokens (e.g., YubiKey) are hardware-based security keys that support passwordless authentication in Microsoft Entra ID. They are part of Microsoft's passwordless authentication strategy and can be used for sign-in.

However, FIDO2 security tokens are not supported for SSPR. The SSPR process does not allow users to verify their identity using a FIDO2 security key because the reset process is designed to work with simpler, more accessible methods like email, SMS, or app-based codes.

Conclusion:This is incorrect.

D . A Windows Hello PIN:

Windows Hello PIN is a device-specific authentication method used to sign in to Windows devices. It is part of Windows Hello, which also includes biometric authentication (e.g., facial recognition, fingerprint).

Windows Hello PIN is not supported for SSPR in Microsoft Entra ID. The SSPR process occurs in a web-based portal (e.g., aka.ms/sspr) and does not integrate with device-specific authentication methods like Windows Hello. Additionally, Windows Hello PIN is tied to a specific device, whereas SSPR is designed to be device-agnostic.

Conclusion:This is incorrect.

Additional Considerations:

The setting 'Require users to register when signing in: Yes' ensures that users have at least one authentication method registered. However, the question does not specify which methods are enabled by the administrator. In Microsoft Entra ID, the default enabled methods for SSPR typically include email, mobile phone (SMS), mobile app code, and mobile app notification. Security questions may also be enabled but are less common due to security concerns.

If the administrator has disabled certain methods (e.g., mobile app code), the answer could change. However, the question does not indicate any such restrictions, so we assume the default methods are available.

The 'Number of methods required to reset: 1' setting means users only need to use one method to reset their password, but they may have multiple methods registered. The question asks for a 'valid authentication method available to users,' so we need to identify a method that SSPR supports.

Conclusion:Based on the SSPR settings and the supported authentication methods in Microsoft Entra ID:

A mobile app code (option B) is a valid authentication method for SSPR, as it is supported by default and aligns with the configuration.

Smartcards, FIDO2 security tokens, and Windows Hello PIN are not supported for SSPR.Therefore, the correct answer isB.


Microsoft Entra ID documentation: 'Self-service password reset authentication methods' (Microsoft Learn:https://learn.microsoft.com/en-us/entra/identity/authentication/concept-sspr-howitworks#authentication-methods)

Microsoft Entra ID documentation: 'Configure self-service password reset' (Microsoft Learn:https://learn.microsoft.com/en-us/entra/identity/authentication/howto-sspr-deployment)

Microsoft Identity and Access Administrator (SC-300) exam study guide, which covers SSPR configuration and supported authentication methods.

Question 4

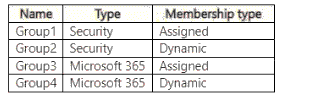
You have a Microsoft Entra tenant that contains the groups shown in the following table.

You need to implement Privileged Identity Management (PIM) for the groups.

Which groups can be managed by using PIM?

Correct answer: C

Privileged Identity Management (PIM) for groups in Microsoft Entra ID can only be applied to eligible assignment groups, specifically security groups and Microsoft 365 groups that have a membership type of Assigned. According to Microsoft documentation (''Manage Privileged Access Groups in PIM''), only assigned groups can be enabled for PIM. Dynamic groups are not supported for PIM because their memberships are automatically managed based on rules, and PIM requires manual activation and approval for eligible roles or memberships.

From the official study guide and Microsoft Learn module ''Implement Privileged Identity Management (PIM) for Groups'':

''Only groups with an Assigned membership type can be managed in Privileged Identity Management. Dynamic membership groups cannot be enabled for privileged access.''

Therefore, among the listed groups:

Group1 (Security, Assigned) Supported

Group2 (Security, Dynamic) Not supported

Group3 (Microsoft 365, Assigned) Supported

Group4 (Microsoft 365, Dynamic) Not supported

Correct Answe r: C. Group1 and Group3 only


Question 5

You need to meet the planned changes for the User administrator role.

What should you do?

Correct answer: B

In Azure AD Privileged Identity Management (PIM) for Azure AD roles, the exam materials describe that you tailor how a role (for example, User administrator) is used by editing its Role settings. These settings control activation behavior, including require multi-factor authentication, justification, approval, assignment/activation durations, and notifications. The guide states that administrators can ''configure activation requirements and time-bound eligibility on a per-role basis'' and ''enforce approval workflows and MFA at activation.'' Access reviews are used to periodically verify who still needs a role, but they do not implement the operational changes to how the role is activated. Active assignments simply shows and changes who currently holds active/eligible assignments; it does not set policy for the role's activation behavior. Administrative units scope certain directory tasks, but they are not how you change PIM activation/approval/MFA requirements. Therefore, to meet planned changes for the User administrator role (such as least privilege activation with approval, justification, and MFA), you update PIM Azure AD roles User administrator Role settings. This aligns with the SC-300 objective to ''configure PIM settings and policies for Azure AD roles,'' ensuring governance by policy rather than ad-hoc assignment.


Unlock all Microsoft SC-300 questions

Full exam access, validated answers, and unlimited practice with no download limits.

The SC-300 exam tests both conceptual knowledge and practical ability in Microsoft identity and access administration. Candidates must understand how to secure user access, configure authentication controls, and manage identity governance in real-world scenarios. The exam also checks whether you can apply Azure identity skills to business requirements with accuracy and confidence.

How QA4Exam.com Helps You Pass

QA4Exam.com provides SC-300 Exam PDF content with actual questions and answers, plus an Online Practice Test designed to mirror the real exam experience. The practice material helps you study updated questions, review verified answers, and understand the exam pattern before test day. With realistic simulation, you can improve time management and get comfortable with the pressure of answering within the exam format. This combination gives you a focused way to prepare and increases your chances of passing the Microsoft SC-300 exam on your first attempt.

Frequently Asked Questions

Who should take the Microsoft SC-300 exam?

The exam is for professionals who work with Microsoft Azure identity and access administration, including user identities, authentication, access management, workload identities, and identity governance.

Is the Microsoft SC-300 exam difficult?

It can be challenging if you do not have hands-on knowledge of Azure identity features. The exam checks practical understanding, not just memorization.

Can I pass SC-300 with only braindumps?

Braindumps alone are not the best approach. You should use them with study and practice so you understand the concepts behind the answers.

Do I need hands-on experience for SC-300?

Yes, hands-on experience is highly useful because the exam focuses on real administration tasks such as access control, identity governance, and authentication management.

Are the QA4Exam.com dumps enough to pass?

The Exam PDF and Online Practice Test are strong preparation tools, but the best results come from combining them with review of the exam topics and practical understanding.

How do the QA4Exam.com practice tests help with first attempt success?

They help you study updated questions, verify answers, simulate the exam format, and practice time management so you can answer more confidently on exam day.

What is included in the QA4Exam.com SC-300 format?

QA4Exam.com offers an Exam PDF with questions and answers and an Online Practice Test that follows a realistic exam style for focused preparation.