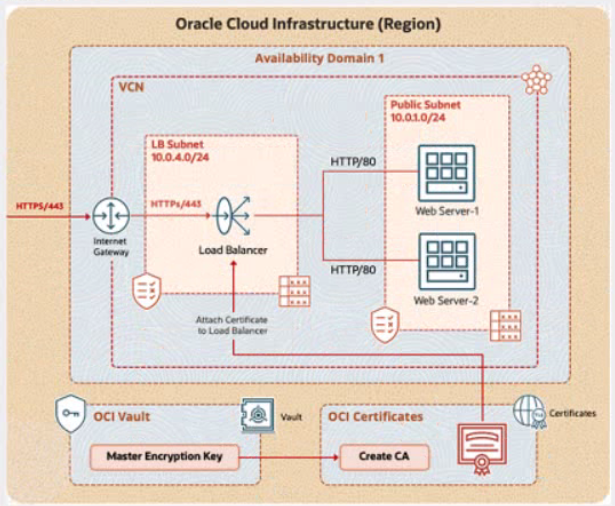
Challenge 1: Integrate TLS Certificate Issued by the OCI Certificates Service with Load Balancer
Task 1: Create and Configure a Virtual Cloud Network (VCN)
Step 1: Create the Virtual Cloud Network (VCN)
Log in to the OCI Console.
Navigate to Networking > Virtual Cloud Networks.
Click Create Virtual Cloud Network.
Select VCN with Internet Connectivity (to include an Internet Gateway by default).
Enter the following details:
Name: PBT-CERT-VCN-01
Compartment: Select your assigned compartment.
VCN CIDR Block: 10.0.0.0/16
Leave other settings as default (e.g., create a new public subnet and route table).
Click Create Virtual Cloud Network. Wait for the VCN to be created.
Step 2: Create Subnet 1 (Compute-Subnet-PBT-CERT)
In the VCN details page for PBT-CERT-VCN-01, click Subnets under Resources.
Click Create Subnet.
Enter the following details:
Name: Compute-Subnet-PBT-CERT
Subnet Type: Regional
CIDR Block: 10.0.1.0/24
Route Table: Select the default route table created with the VCN.
Subnet Access: Public Subnet (to allow internet access).
DNS Resolution: Enabled.
Click Create.
Step 3: Create Subnet 2 (LB-Subnet-PBT-CERT-SNET-02)
In the VCN details page, click Subnets under Resources.
Click Create Subnet.
Enter the following details:
Name: LB-Subnet-PBT-CERT-SNET-02
Subnet Type: Regional
CIDR Block: 10.0.2.0/24
Route Table: Select the default route table created with the VCN.
Subnet Access: Public Subnet (to allow internet access for the load balancer).
DNS Resolution: Enabled.
Click Create.
Step 4: Verify Internet Gateway
In the VCN details page, under Resources, click Internet Gateways.
Ensure an Internet Gateway is listed and attached to PBT-CERT-VCN-01. If not created, click Create Internet Gateway, name it (e.g., PBT-CERT-IGW), and attach it.
Step 5: Configure Route Table
In the VCN details page, under Resources, click Route Tables.
Select the default route table or create a new one named PBT-CERT-RT-01.
Click Add Route Rule. 4 - Destination CIDR Block: 0.0.0.0/0
Target Type: Internet Gateway
Target: Select the Internet Gateway created (e.g., PBT-CERT-IGW).
Click Add Route Rule and save.
Step 6: Create Security List for Subnet 1 (Compute-Subnet-PBT-CERT)
In the VCN details page, under Resources, click Security Lists.
Click Create Security List.
Enter the following:
Name: PBT-CERT-CS-SL-01
Compartment: Your assigned compartment.
Add the following ingress rule:
Source CIDR: 0.0.0.0/0 (allow from any source, adjust as per security needs)
IP Protocol: TCP
Source Port Range: All
Destination Port Range: 22 (for SSH)
Allows: Traffic
Click Create.
Step 7: Create Security List for Subnet 2 (LB-Subnet-PBT-CERT-SNET-02)
In the VCN details page, under Resources, click Security Lists.
Click Create Security List.
Enter the following:
Name: PBT-CERT-LB-SL-01
Compartment: Your assigned compartment.
Add the following ingress rule:
Source CIDR: 0.0.0.0/0 (allow from any source, adjust as per security needs)
IP Protocol: TCP
Source Port Range: All
Destination Port Range: 443 (for HTTPS)
Allows: Traffic
Click Create.
Step 8: Retrieve and Enter VCN OCID
Go to the VCN details page for PBT-CERT-VCN-01.
Copy the OCID from the VCN information section.
Enter the OCID in the provided text box.