
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

NetSec-Analyst Exam Dumps and Practice Questions

Preview page 1 of 15 with real questions 1 to 5 from the full 74-question Palo Alto Networks set.

Palo Alto Networks NetSec-Analyst Dumps - Pass Palo Alto Networks Network Security Analyst Exam in First Attempt 2026

The Palo Alto Networks NetSec-Analyst exam, also known as Palo Alto Networks Network Security Analyst, is part of the Palo Alto Networks Certified Network Security Administrator certification path. It is designed for candidates who want to validate practical network security administration knowledge and exam-ready skills. This certification matters for professionals who work with security policies, configuration, operations, and troubleshooting in Palo Alto Networks environments. Passing this exam shows that you can handle core tasks with confidence in real-world scenarios.

# Exam Topics Sub-Topics Approximate Weightage (%)
1 Object Configuration Creation and Application Object creation, object groups, application of objects, reusable configuration elements 25%
2 Policy Creation and Application Security policy rules, policy matching, rule order, policy application and validation 30%
3 Management and Operations Administrative tasks, device management, configuration review, operational workflows 20%
4 Troubleshooting Issue identification, log analysis, policy troubleshooting, configuration problem resolution 25%

This exam tests how well candidates can apply Palo Alto Networks knowledge in practical situations, not just memorize terms. You should be ready for configuration-based questions, policy decisions, operational understanding, and troubleshooting scenarios. A strong grasp of daily administrative tasks and how features work together is important for success.

Actual Palo Alto Networks NetSec-Analyst Exam Questions

Question 1

Which action ensures that sensitive information such as medical records, financial transactions, and legal communications are not decrypted and that they maintain strong security?

Correct answer: D

Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:

In a Palo Alto Networks environment, decryption is essential for visibility, but legal and compliance requirements often dictate that certain types of traffic---specifically those involving sensitive personal data---must remain encrypted. To comply with these regulations while still inspecting other high-risk traffic, a Network Security Analyst should create a 'no-decrypt' policy for traffic matching specific URL categories (D).

Palo Alto Networks provides predefined URL categories such as financial-services, health-and-medicine, and government. When these categories are used as matching criteria in a Decryption Policy rule with the action set to 'No Decrypt,' the firewall will bypass the SSL/TLS decryption process for that specific traffic. This ensures that the privacy of sensitive transactions, like medical records or banking, is maintained and that the raw data is never exposed in the firewall's memory or logs.

Furthermore, to maintain 'strong security' as requested, the analyst should attach a Decryption Profile to this no-decrypt rule. This profile can be configured to block sessions that use weak protocols (like SSLv3 or TLS 1.0) or expired certificates, ensuring that even if the traffic is not decrypted, it is still forced to meet modern security standards before entering or leaving the network.

Question 2

An analyst needs to prevent users from downloading executable files from "High-Risk" URL categories while allowing them from "Business-and-Economy." Which profile should be configured to achieve this specific file-type restriction?

Correct answer: C

Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:

The File Blocking Profile is the primary tool used by Palo Alto Networks firewalls to control the movement of specific file types across the network. While a URL Filtering Profile (Option A) can block access to a website based on its category, it does not have the granular ability to distinguish between a PDF download and an EXE download on that site.

To meet the requirement, the analyst creates a File Blocking Profile with rules that target the .exe file extension. The profile allows the analyst to set actions like alert, block, or continue based on the direction of the traffic (upload or download) and the application being used. By attaching this profile to a Security policy rule, the firewall uses Content-ID to look deep into the payload---beyond just the file extension---to identify the true file type. This prevents users from bypassing security by simply renaming a malicious .exe file to .txt. This is a core objective for ensuring that sanctioned web browsing does not become a vector for malware delivery.


Question 3

A security administrator needs to block access to a specific list of 500 malicious domains. These domains are updated daily by a third-party intelligence feed. What is the most efficient way to manage these domains as an object?

Correct answer: B

Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:

For high-volume, frequently changing indicators of compromise (IoCs), manual entry is not scalable. An External Dynamic List (EDL) allows the firewall to automatically import a list of domains from an external web server.

When configured as a 'Domain' type EDL, the analyst simply provides the URL of the text file hosted by the intelligence provider. The firewall then periodically retrieves this file (e.g., every 5 minutes or hourly) and updates the security policy in real-time without requiring a configuration commit. This automation is a critical objective for maintaining a proactive security posture. Using an EDL ensures that the perimeter defense is always synchronized with the latest threat intelligence, whereas manual lists (Options A and D) introduce significant administrative overhead and a 'security gap' between the time a threat is identified and the time the firewall is updated.


Question 4

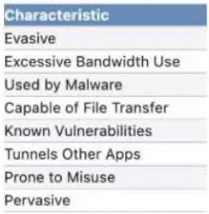
A security administrator is creating an internet of things (IoT) Security policy and needs to select behaviors for the traffic.

Which characteristic has the greatest impact to the risk level of applications?

Correct answer: A

Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:

In the Palo Alto Networks ecosystem, App-ID utilizes specific characteristics to help administrators assess the risk profile of applications traversing the network. These characteristics---which include whether an application is evasive, prone to misuse, or capable of file transfer---are aggregated into a numerical Risk Score ranging from 1 (lowest risk) to 5 (highest risk).

Among the listed characteristics, 'Used by Malware' (A) typically has the greatest immediate impact on the assigned risk level. This characteristic indicates that the application is a known vector for Command and Control (C2) traffic, data exfiltration, or payload delivery, necessitating a high risk rating (often 4 or 5). While 'Known Vulnerabilities' (D) and 'Tunnels Other Apps' (C) certainly increase the risk level by providing an exploit surface or obscuring visibility, they represent potential risks. In contrast, an application being actively 'Used by Malware' represents a direct and validated threat to the environment.

'Pervasive' (B) refers to how common an application is and generally does not drive a high-risk score on its own. For an analyst building an IoT Security policy, prioritizing applications with the 'Used by Malware' characteristic is critical, as many IoT devices lack robust internal security and are frequently recruited into botnets via these specific communication channels.


Question 5

What are two valid pattern types in a Data Filtering profile? (Choose two.)

Correct answer: C, D

Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:

In the Palo Alto Networks ecosystem, specifically when utilizing Strata Cloud Manager (SCM) and Enterprise Data Loss Prevention (DLP), Data Filtering profiles are used to identify and protect sensitive information. When an analyst creates a custom data pattern to be used within these profiles, the system allows for two primary methods of identification: Regular Expressions (Regex) and File Properties.

Regular Expressions (D) allow the analyst to define a specific string or numerical pattern, such as a custom employee ID format or a proprietary project code. This is the most flexible and common way to catch sensitive text data within a file or data stream.

File Properties (C) allow the analyst to create patterns based on the metadata or attributes of a file rather than its contents. This includes identifying files based on the 'Author,' 'Title,' 'Company,' or even custom tags embedded in document properties (e.g., Microsoft Word or PDF metadata). By combining these two pattern types, a Network Security Analyst can create a highly granular detection engine. For instance, a policy could block any file where the 'Company' property is set to a competitor or any file containing text that matches a specific Regex-defined sensitive data format.

While 'Predefined' patterns (like Credit Card numbers) are also a core component, they are not listed as an option here. 'Proximity Patterns' are a feature used to reduce false positives by ensuring two patterns appear near each other, but the fundamental 'pattern types' for custom definitions are Regex and File Properties.


Unlock all Palo Alto Networks NetSec-Analyst questions

Full exam access, validated answers, and unlimited practice with no download limits.

How QA4Exam.com Helps You Pass

QA4Exam.com provides Exam PDF content with actual questions and answers, along with an Online Practice Test built to support your Palo Alto Networks NetSec-Analyst preparation. The practice test helps you experience a real exam simulation so you can become familiar with question style and exam flow. Updated questions and verified answers help you study with more confidence and reduce guesswork. The online format also gives you a chance to improve time management before exam day. With both formats, you can prepare more efficiently and aim for first attempt success.

Frequently Asked Questions

1. Who should take the Palo Alto Networks Network Security Analyst exam?

It is for candidates who want to validate their network security administration skills within the Palo Alto Networks Certified Network Security Administrator certification path.

2. Is the NetSec-Analyst exam difficult?

It can be challenging because it tests practical understanding of objects, policy, operations, and troubleshooting, not just theory.

3. Can I pass with only braindumps?

Relying on only braindumps is not the best approach. You should use verified questions and answers together with practical study so you understand the concepts behind the answers.

4. Do I need hands-on experience for this exam?

Hands-on experience is very helpful because the exam focuses on configuration, policy application, management, and troubleshooting scenarios.

5. Are QA4Exam.com dumps enough to help me pass in the first attempt?

QA4Exam.com materials are designed to strengthen your preparation with actual questions and answers, but your best chance for first attempt success comes from using them with focused review and practice.

6. What format does QA4Exam.com provide for NetSec-Analyst preparation?

QA4Exam.com offers an Exam PDF and an Online Practice Test so you can study offline, practice in a simulated exam environment, and review verified answers.

7. How does the online practice test help with exam readiness?

It helps you practice under timed conditions, understand the question style, and build confidence before taking the real exam.

8. Are the questions updated and verified?

QA4Exam.com presents updated questions and verified answers to help you prepare with more reliability and less uncertainty.