
Trusted Worldwide Questions & Answers
Proofpoint PPAN01 Dumps for Certified Threat Protection Analyst Exam Success in 2026
The Proofpoint PPAN01 - Certified Threat Protection Analyst Exam is part of the Proofpoint Cybersecurity Certifications track and is designed for candidates who want to validate their knowledge of threat protection and incident handling. It is a strong fit for security professionals who work with detection, response, and recovery workflows in modern environments. This certification matters because it shows that you understand the practical steps needed to analyze incidents and support effective threat protection operations.
| # | Exam Topics | Sub-Topics | Approximate Weightage (%) |
|---|---|---|---|
| 1 | Incident Response Foundations | Incident response concepts, roles and responsibilities, response lifecycle | 15% |
| 2 | The Preparation Phase | Readiness planning, response tools and resources, documentation and communication setup | 20% |
| 3 | Detection and Analysis | Alert triage, evidence review, threat validation, impact assessment | 25% |
| 4 | Containment, Eradication, and Recovery | Short-term containment, removing malicious activity, restoring systems and services | 25% |
| 5 | Post-Incident Activity | Lessons learned, reporting, process improvement, follow-up actions | 15% |
This exam tests how well candidates understand the full incident response workflow, from preparation and detection to containment and recovery. It also checks practical judgment, analysis skills, and the ability to choose the right response actions in real-world security situations. Candidates need both conceptual knowledge and applied understanding to perform well.
How QA4Exam.com Helps You Pass
QA4Exam.com provides Exam PDF materials with actual questions and answers, along with an Online Practice Test for the Proofpoint PPAN01 exam. These resources help you review up-to-date questions, understand verified answers, and experience real exam simulation before test day. The practice format also improves time management so you can answer efficiently under exam pressure. With focused preparation and realistic practice, you can build confidence and improve your chances of passing on the first attempt.
Frequently Asked Questions
1. What is the Proofpoint Certified Threat Protection Analyst Exam PPAN01?
PPAN01 is the Certified Threat Protection Analyst Exam in the Proofpoint Cybersecurity Certifications track. It focuses on incident response, detection, containment, recovery, and post-incident activities.
2. Who should take the PPAN01 exam?
It is suitable for security professionals who want to validate practical knowledge of threat protection and incident response processes. It is especially relevant for candidates working in detection and response roles.
3. Is the Proofpoint PPAN01 exam difficult?
It can be challenging because it covers the complete incident response flow and expects practical understanding, not just memorization. Candidates who study the topics carefully and practice with realistic questions are better prepared.
4. Can I pass PPAN01 with only braindumps?
Braindumps alone are not the best approach. You should use them together with structured review and practice so you understand why the answers are correct and can handle different question styles.
5. Do I need hands-on experience for the exam?
Hands-on experience is helpful because the exam includes practical incident response concepts. Even if you are studying from dumps and practice tests, real-world familiarity can improve your confidence and decision-making.
6. Are the QA4Exam.com dumps and practice test enough to prepare?
QA4Exam.com provides Exam PDF questions and answers plus an Online Practice Test to support targeted preparation. These materials are very useful, and combining them with careful review of the listed exam topics can strengthen your readiness.
7. How do the QA4Exam.com practice tests help with first-attempt success?
They simulate the exam experience, show you up-to-date questions, and help you practice time management. This makes it easier to identify gaps, improve accuracy, and enter the exam with more confidence.
8. What format do the QA4Exam.com materials use for PPAN01?
The study package includes an Exam PDF with questions and answers and an Online Practice Test. This gives you both review material and a realistic practice environment for exam preparation.
The questions for PPAN01 were last updated on Sep 26, 2026.
- Viewing page 1 out of 10 pages.
- Viewing questions 1-5 out of 52 questions
Exhibit:
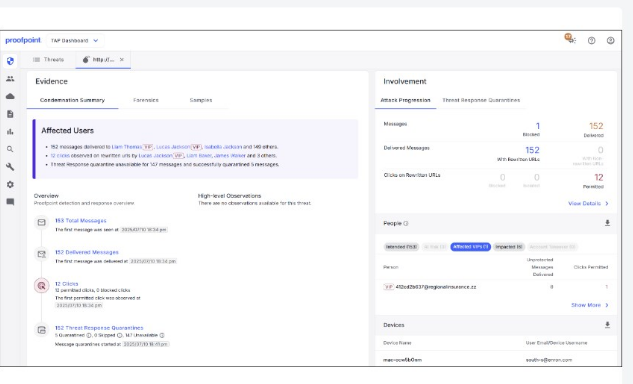
What can be determined by the threat information shown in the exhibit?
The exhibit's threat detail indicates that a VIP user clicked and that the click occurred on a non-rewritten URL (D). This determination is significant in Proofpoint IR because non-rewritten clicks can bypass URL Defense's time-of-click protections and logging, reducing both prevention and visibility. It often happens when a user accesses the link outside the protected path (e.g., copying/pasting the URL into a browser, using a client/app that didn't preserve rewriting, or receiving the URL through a channel where rewriting wasn't applied). For responders, this elevates urgency: the VIP user should be prioritized for compromise assessment (credential reset, token/session revocation, MFA verification, mailbox rule/forwarding review, suspicious login checks) because the protective block page may not have been enforced. It also drives containment improvements: ensure URL Defense rewriting is applied broadly (body links), verify supported clients and configurations, and consider additional controls such as isolation or stricter policies for VIP cohorts. The other options (A--C) require explicit remediation or message-count indicators that are not definitively implied by the ''VIP clicked non-rewritten URL'' exhibit signal.
An analyst is reviewing the Threat Response Quarantines card for a message in TAP Dashboard, as shown in the exhibit.
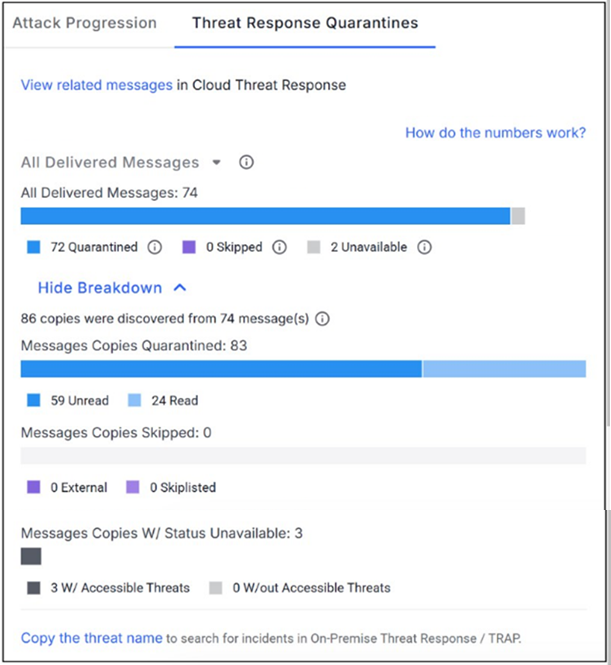
Why might a message be flagged with status ''unavailable''?
In Proofpoint Threat Response / post-delivery remediation workflows, a quarantine action depends on the message still existing in the target mailbox (Inbox or other folders where the connector searches). A status of ''unavailable'' commonly indicates the system could not locate the message to apply the action---most often because it was deleted or otherwise removed before quarantine occurred (A). This can happen if the user manually deletes it, an automated mailbox rule moves it to Deleted Items and empties it, retention policies purge it, or another remediation tool removes it first. From an IR containment perspective, ''unavailable'' is important because it changes the response plan: if the message cannot be pulled, you must pivot to containment through other controls (blocklist URLs/domains, disable sender delivery, enforce URL Defense blocking, reset credentials if interaction occurred) and expand scoping (search for duplicates in other mailboxes). Best practice is to correlate ''unavailable'' with click telemetry (Impacted users), authentication results, and mailbox audit logs to confirm whether exposure occurred and whether compensating actions are required to prevent recurrence.
Which Proofpoint product quarantines malicious email after delivery?
TRAP (Threat Response Auto-Pull) is the Proofpoint capability designed for post-delivery remediation---it can locate and quarantine/pull messages from user mailboxes after they have already been delivered. This is critical in real-world IR because many threats are discovered after initial delivery (e.g., URL reputation flips, delayed detonation results, user-reported phish via ''Report Suspicious,'' or new campaign intelligence). TAP provides detection, verdicting, and campaign intelligence, but TRAP is the mechanism that operationalizes containment inside mailboxes by removing the message from inboxes and other folders to reduce further exposure. In incident handling, TRAP actions are commonly paired with scoping queries (who received it), retroactive search for similar messages, and compensating controls (URL Defense blocks, domain blocks, authentication enforcement). Using TRAP effectively reduces ''time at risk'' and limits additional clicks or credential submissions after the incident is identified. It also supports auditability by recording which mailboxes were remediated and whether any items were ''unavailable,'' which becomes a follow-up scoping requirement.
What type of threat does the Cloud Security Report help identify in connected environments?
The Cloud Security Report is designed to highlight risks and suspicious activity across connected cloud environments, with a strong focus on indicators consistent with account takeover (ATO) (B). In Proofpoint cloud-connected contexts (e.g., cloud email and SaaS integrations), ATO manifests through patterns such as unusual sign-in behavior, suspicious mailbox activity, anomalous sending, unexpected forwarding rules, OAuth application consents, and risky access from new locations/devices. For IR, this is critical because modern phishing frequently targets credentials and sessions rather than delivering executable malware, and compromised cloud identities enable fast lateral movement through internal phishing, invoice fraud, and data access. Proofpoint reporting helps analysts identify which users and accounts show the strongest compromise signals so they can prioritize containment: force password reset, revoke refresh tokens/sessions, remove malicious inbox rules and forwarding, disable suspicious OAuth grants, and validate MFA posture. While ransomware, insider risk, and BEC can be related outcomes, the Cloud Security Report's connected-environment emphasis is on identity compromise signals and cloud account misuse---core ATO detection and investigation drivers.
In which part of the SMTP conversation can threat actors spoof information to make the message look safe to the recipient?
Threat actors most commonly spoof what the recipient visually trusts---primarily fields displayed by mail clients---by manipulating message headers (D), especially From:, Reply-To:, and Return-Path-related presentation cues (even though some are derived from envelope, the client display is header-driven). While the SMTP envelope can be spoofed during transmission, the ''look safe to the recipient'' effect is achieved through header content because that is what appears in the inbox preview and open-message view. Proofpoint investigations validate this by comparing: RFC5322.From vs RFC5321.MailFrom (envelope), authentication results (SPF/DKIM/DMARC), and alignment. Spoofed headers are central to BEC, display-name spoofing, and executive impersonation, and Proofpoint's sender analysis and authentication panels help responders quickly identify mismatches and impersonation risk. In IR triage, analysts examine the full headers to reconstruct the true path (Received chain), identify forged identity indicators, and determine whether the message bypassed defenses due to weak DMARC enforcement, allow-listing, or trusted-partner misconfiguration.
Unlock All Questions for Proofpoint PPAN01 Exam
Full Exam Access, Actual Exam Questions, Validated Answers, Anytime Anywhere, No Download Limits, No Practice Limits
Get All 52 Questions & Answers