
Trusted Worldwide Questions & Answers
Proofpoint TPAD01 Dumps - Pass the Threat Protection Administrator Exam in 2026
The Proofpoint TPAD01 - Threat Protection Administrator Exam is part of the Proofpoint Cybersecurity Certifications track and is designed for professionals who manage and secure email threat protection environments. It focuses on the knowledge needed to administer key protection features, monitor traffic, and respond to threats effectively. This exam matters because it validates practical skills that support secure messaging operations and stronger email defense. Candidates who want to prove their ability with Proofpoint security tools can use focused exam preparation to build confidence and readiness.
Exam Topics and Approximate Weightage
| # | Exam Topics | Sub-Topics | Approximate Weightage (%) |
|---|---|---|---|
| 1 | Product Overview | Platform purpose, core components, admin roles | 7% |
| 2 | Mail Flow | Message routing, policy flow, delivery handling | 8% |
| 3 | Message Processing | Inspection steps, filtering logic, processing actions | 8% |
| 4 | Email Firewall | Gateway controls, policy enforcement, inbound protection | 8% |
| 5 | Quarantine | Message review, release actions, quarantine management | 7% |
| 6 | Smart Search & Logging | Search filters, audit logs, message tracking | 7% |
| 7 | Alerts & Reporting | Alert types, report views, monitoring output | 7% |
| 8 | Email Authentication | SPF, DKIM, DMARC validation, authentication results | 8% |
| 9 | User Management | Accounts, permissions, administrative settings | 7% |
| 10 | Spam Detection | Spam indicators, filtering behavior, tuning controls | 8% |
| 11 | Virus Protection | Malware scanning, threat blocking, attachment handling | 8% |
| 12 | User Notifications | Notification templates, delivery settings, user alerts | 6% |
| 13 | Targeted Attack Protection (TAP) | Attack detection, analysis workflows, malicious content review | 10% |
| 14 | Threat Response | Incident actions, remediation steps, response coordination | 9% |
| Total | 100% | ||
The exam tests how well candidates understand Proofpoint administration concepts and how those features work together in real email security workflows. It also checks practical decision-making, including message handling, threat detection, policy control, logging, and response actions. Strong candidates should be able to recognize feature behavior, interpret security outcomes, and apply administrative knowledge with confidence.
How QA4Exam.com Helps You Pass
QA4Exam.com offers the TPAD01 Exam PDF with actual questions and answers, giving you a focused way to review the exam style and essential concepts. The Online Practice Test helps you experience a real exam simulation so you can build speed, accuracy, and confidence before test day.
Both formats are designed to support effective preparation with up-to-date questions and verified answers. This makes it easier to identify weak areas, improve time management, and study with a clear target. If you want a practical path toward first-attempt success on the Proofpoint TPAD01 exam, these resources can help you prepare more efficiently.
Frequently Asked Questions
1. Who should take the Proofpoint TPAD01 Threat Protection Administrator Exam?
This exam is meant for candidates who work with Proofpoint threat protection administration and want to validate their knowledge of email security operations, policies, and response features.
2. Is the Proofpoint TPAD01 exam considered difficult?
It can be challenging because it covers multiple security functions such as mail flow, authentication, quarantine, TAP, and threat response. Candidates who study the exam topics carefully usually feel more prepared.
3. Can I pass TPAD01 with only braindumps?
Braindumps alone are not a complete preparation method. They are most effective when combined with topic review, practice, and a clear understanding of how the Proofpoint features work.
4. Do I need hands-on experience to pass the exam?
Hands-on experience is helpful because it can make the exam topics easier to understand, especially for message processing, logging, alerts, and threat response. However, focused study can still help you prepare well.
5. Are QA4Exam.com dumps enough, or should I use other resources too?
The QA4Exam.com Exam PDF and Online Practice Test are strong preparation tools, but many candidates also review the topic list carefully to reinforce understanding and improve retention.
6. How does the QA4Exam.com practice test help with first-attempt success?
The practice test simulates the exam environment, helps you manage time, and lets you check your readiness with verified answers. This can reduce surprises and improve confidence on exam day.
7. Do the QA4Exam.com materials include both PDF and online practice format?
Yes, the available preparation options include an Exam PDF with questions and answers and an Online Practice Test that supports interactive exam-style preparation.
The questions for TPAD01 were last updated on Sep 27, 2026.
- Viewing page 1 out of 14 pages.
- Viewing questions 1-5 out of 72 questions
Review the filter log exhibit.
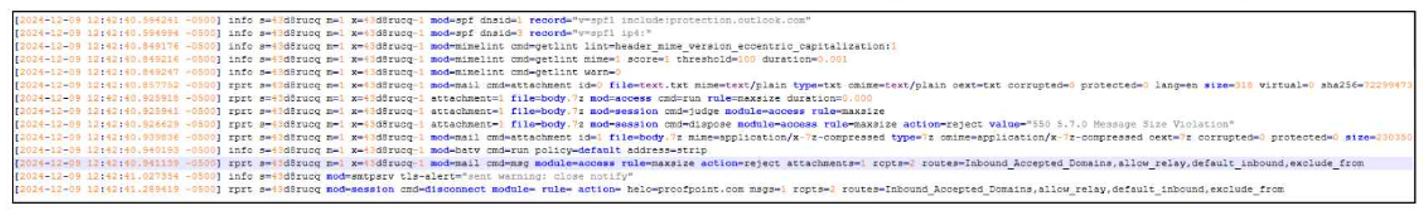
What is happening to this inbound email?
The correct answer is C. The email was rejected due to its excessive size.
From the filter-log exhibit, the key indicator is the rejection entry that shows a Message Size Violation response. That tells you the Protection Server accepted enough of the SMTP transaction to evaluate the message, but then rejected it because it exceeded the configured size threshold. In other words, this is not a transport drop, not a normal successful delivery, and not a timeout caused by lengthy processing. The decisive clue is the size-related rejection text in the log.
This kind of event belongs to the Mail Flow topic because it reflects SMTP-time handling and message acceptance controls. Proofpoint applies a series of processing steps as mail is received, including connection checks, MIME inspection, attachment evaluation, and policy enforcement. When the message exceeds the allowed size, the server returns a rejection tied to that violation instead of continuing with normal acceptance and delivery.
Why the other choices are incorrect:
A is wrong because the log does not indicate that the sender disconnected before the transaction could complete.
B is wrong because the message was not delivered successfully; it was explicitly rejected.
D is wrong because the evidence points to a size violation, not a processing-time threshold breach.
So the complete interpretation of the exhibit is that the inbound message was rejected because it was too large, which makes Answer C the verified course-aligned choice.
Which of the following is the correct order for SMTP message reception?
The correct answer is A. connection, helo, envelope sender, envelope recipient, message headers, message body. Proofpoint's SMTP relay reference explains the SMTP exchange in the expected sequence: the connection is established first, then the sending server identifies itself with HELO/EHLO, then MAIL FROM specifies the envelope sender, then recipient commands define the destination, and finally the message content is transmitted. Separate Proofpoint material on email structure also distinguishes the envelope, headers, and body as distinct parts of an email.
This is foundational mail-flow knowledge in the Threat Protection Administrator course because many connection-level and policy decisions occur before the full body is even processed. Recipient verification, SMTP rate controls, and some anti-spam or anti-spoofing logic rely on understanding where in the SMTP conversation each data element appears. The distractor options mix up that sequence by placing HELO before the connection, reversing sender and recipient order, or moving headers before the recipient stage, all of which are inconsistent with standard SMTP message reception. Therefore, the correct sequence is connection first, then HELO/EHLO, followed by envelope sender, envelope recipient, and finally the message headers and body. That makes A the verified answer.
Which of the following is a common port used for SMTP connectivity?
The correct answer is D. 25. SMTP is the standard protocol used for transferring email between mail servers, and TCP port 25 is the traditional and most common port used for SMTP relay and server-to-server email transport. Proofpoint's SMTP relay reference aligns with this standard mail-flow model, where SMTP is the protocol responsible for message transfer between mail systems.
The other ports listed are associated with different services. Port 22 is commonly used for SSH, port 443 for HTTPS, and port 80 for HTTP. Those are important network ports, but they are not the standard answer for SMTP connectivity in the context of mail flow and Proofpoint administration. In the Threat Protection Administrator course, understanding SMTP basics is essential because route configuration, TLS behavior, queue handling, and delivery troubleshooting all rely on knowing how SMTP sessions operate at the transport level.
Although modern mail submission can also involve other ports in certain client scenarios, this question asks for a common SMTP connectivity port, and the course-level expected answer is the standard server-to-server SMTP port. For mail transfer in the context of Proofpoint and SMTP routing, that port is 25. Therefore, the verified answer is D.
Smart Search has returned 13 results for a specific recipient address. You click on one of the messages in the Results list. Which of the following information is available for that message?
The correct answer is A. The Final Rule that gave the final disposition for the message. Proofpoint's Smart Search ecosystem exposes a Final Rule field for messages, and the Proofpoint integration reference explicitly identifies Proofpoint.SmartSearch.Final_Rule as the final rule of the email message. That matches the course wording exactly and confirms that this piece of information is available when examining a message record in Smart Search.
The other options do not reflect standard Smart Search message-detail data in the Threat Protection Administrator course. Smart Search is designed to show message-processing and disposition information, not endpoint-style telemetry such as the time a user opened and read a message or the client software version on the recipient device. Likewise, low-level SMTP port numbers for a session are not the key message-detail field being tested here. The course consistently teaches Smart Search as the place to determine what happened to a message, which rules fired, and what final action was taken.
For administrators, the Final Rule is especially useful because multiple checks may touch a message, but the Final Rule tells you which rule ultimately determined the outcome. That is why this is the correct answer to the question. Therefore, the verified answer is A.
Based on the message details shown, which two findings are true for this email?
The correct answer is A. URL Defense is blocking the message due to a malicious link, and the message has been flagged as spam. This answer is based on the message-status information shown in the screenshot prompt and aligns with TAP behavior in Proofpoint, where URL Defense is responsible for handling risky or malicious URLs and spam classification can be applied as a separate message assessment result.
Proofpoint's TAP capabilities include URL-focused protection that rewrites or evaluates links and can block user access when a link is determined to be dangerous. That makes a URL Defense block a standard TAP outcome for suspicious messages containing malicious destinations. At the same time, spam status can still be part of the overall message classification, reflecting layered analysis rather than a single-point decision. Proofpoint's public email-filtering and TAP materials support this layered approach: a message can be analyzed for malicious URLs, phishing indicators, and spam characteristics in parallel and then display multiple findings in the investigation view.
The alternative options do not fit what is shown in the question image. There is no indication the message fully passed, that the sender's internal status was the key cause, or that only attachment stripping occurred without spam or URL concerns. This is a classic TAP-style investigation question where the admin must read the findings displayed for the message. Based on those displayed results, the correct choice is A.
Unlock All Questions for Proofpoint TPAD01 Exam
Full Exam Access, Actual Exam Questions, Validated Answers, Anytime Anywhere, No Download Limits, No Practice Limits
Get All 72 Questions & Answers