
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

MuleSoft-Platform-Architect-I Exam Dumps and Practice Questions

Preview page 1 of 30 with real questions 1 to 5 from the full 152-question Salesforce set.

Salesforce MuleSoft-Platform-Architect-I Dumps - Pass Salesforce Certified MuleSoft Platform Architect Exam in 2026

The Salesforce MuleSoft-Platform-Architect-I exam, officially known as the Salesforce Certified MuleSoft Platform Architect exam, belongs to the MuleSoft Certified Architect certification track. It is designed for professionals who architect, govern, and deploy API solutions across the MuleSoft and Anypoint Platform ecosystem. This certification matters because it validates the ability to design scalable application networks and make sound platform-level architecture decisions.

Exam Topics and Approximate Weightage

# Exam Topics Sub-Topics Approximate Weightage (%)
1 Designing and sharing APIs API design principles, reuse and discoverability, consumer-friendly contracts 12%
2 Designing APIs using System, Process, and Experience Layers Layered API approach, separation of responsibilities, reusable services 12%
3 Governing web APIs on Anypoint Platform API governance policies, lifecycle control, standards and compliance 11%
4 Architecting and deploying API implementations Implementation patterns, deployment planning, integration design choices 12%
5 Deploying API implementations to CloudHub CloudHub deployment model, runtime configuration, environment readiness 10%
6 Meeting API quality goals Performance goals, reliability, maintainability and testing considerations 10%
7 Monitoring and analyzing application networks Observability, traffic analysis, issue detection and operational insight 11%
8 Explaining application network basics Application network concepts, connectivity model, reusable assets 10%
9 Establishing organizational and platform foundations Platform setup, governance foundation, organizational alignment 12%

Actual Salesforce MuleSoft-Platform-Architect-I Exam Questions

Question 1

A business process is being implemented within an organization's application network. The architecture group proposes using a more coarse-grained application

network design with relatively fewer APIs deployed to the application network compared to a more fine-grained design.

Overall, which factor typically increases with a more coarse-grained design for this business process implementation and deployment compared with using a more fine-grained

design?

Correct answer: A

Understanding Coarse-Grained vs. Fine-Grained API Design:

A coarse-grained design consolidates multiple operations within a single API, leading to fewer APIs but with more complex implementations. Conversely, a fine-grained design breaks down functionalities into smaller, more specific APIs, resulting in simpler implementations but a larger number of APIs.

Evaluating the Options:

Option A (Correct Answer): With a coarse-grained design, each API handles more functionalities, increasing the complexity of each API implementation as it needs to manage more use cases and logic.

Option B: A coarse-grained design typically reduces the number of APIs, so fewer discoverable assets are available.

Option C: Fewer APIs generally mean fewer connections between them in the application network.

Option D: Network infrastructure usage may actually decrease with fewer APIs, as there are fewer calls between APIs.

Conclusion:

Option A is the correct answer, as the complexity of each API implementation increases in a coarse-grained design due to the consolidation of multiple functionalities into single APIs.

Refer to MuleSoft's documentation on API design principles and best practices for coarse-grained vs. fine-grained API implementation.
Question 2

An API is protected with a Client ID Enforcement policy and uses the default configuration. Access is requested for the client application to the API, and an approved

contract now exists between the client application and the API

How can a consumer of this API avoid a 401 error "Unauthorized or invalid client application credentials"?

Correct answer: C

When using the Client ID Enforcement policy with default settings, MuleSoft expects the client_id and client_secret to be provided in the URI parameters of each request. This policy is typically used to control and monitor access by validating that each request has valid credentials. Here's how to avoid a 401 Unauthorized error:

URI Parameters Requirement:

The default configuration for the Client ID Enforcement policy requires the client_id and client_secret to be included in each request's URI parameters. This is a straightforward way to authenticate API requests without additional configurations.

Why Option C is Correct:

Providing client_id and client_secret in the URI parameters meets the policy's requirements for each request, ensuring authorized access and avoiding the 401 error.

of Incorrect Options:

Option A (sending a token in the header) would be applicable for token-based authentication (like OAuth 2.0), not Client ID Enforcement.

Option B (request body) and Option D (header) are not valid locations for client_id and client_secret under the default configuration of Client ID Enforcement, which expects them in the URI.

Reference For more details, consult MuleSoft's documentation on Client ID Enforcement policies and expected request configurations


Question 3

What is the most performant out-of-the-box solution in Anypoint Platform to track transaction state in an asynchronously executing long-running process implemented as a Mule application deployed to multiple CloudHub workers?

Correct answer: C

Correct Answe r: Persistent Object Store

*****************************************

>> Redis distributed cache is performant but NOT out-of-the-box solution in Anypoint Platform

>> File-storage is neither performant nor out-of-the-box solution in Anypoint Platform

>> java.util.WeakHashMap needs a completely custom implementation of cache from scratch using Java code and is limited to the JVM where it is running. Which means the state in the cache is not worker aware when running on multiple workers. This type of cache is local to the worker. So, this is neither out-of-the-box nor worker-aware among multiple workers on cloudhub. https://www.baeldung.com/java-weakhashmap

>> Persistent Object Store is an out-of-the-box solution provided by Anypoint Platform which is performant as well as worker aware among multiple workers running on CloudHub. https://docs.mulesoft.com/object-store/

So, Persistent Object Store is the right answer.


Question 4

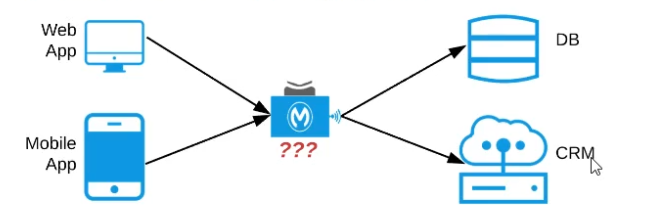
Refer to the exhibit. An organization needs to enable access to their customer data from both a mobile app and a web application, which each need access to common fields as well as certain unique fields.

The data is available partially in a database and partially in a 3rd-party CRM system.

What APIs should be created to best fit these design requirements?

A) A Process API that contains the data required by both the web and mobile apps, allowing these applications to invoke it directly and access the data they need thereby providing the flexibility to add more fields in the future without needing API changes

B) One set of APIs (Experience API, Process API, and System API) for the web app, and another set for the mobile app

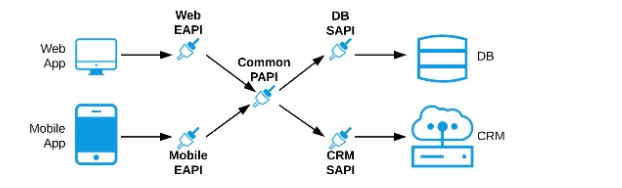
C) Separate Experience APIs for the mobile and web app, but a common Process API that invokes separate System APIs created for the database and CRM system

D) A common Experience API used by both the web and mobile apps, but separate Process APIs for the web and mobile apps that interact with the database and the CRM System

Correct answer: C

Correct Answe r: Separate Experience APIs for the mobile and web app, but a common Process API that invokes separate System APIs created for the database and CRM system

*****************************************

As per MuleSoft's API-led connectivity:

>> Experience APIs should be built as per each consumer needs and their experience.

>> Process APIs should contain all the orchestration logic to achieve the business functionality.

>> System APIs should be built for each backend system to unlock their data.


Question 5

An organization requires several APIs to be secured with OAuth 2.0, and PingFederate has been identified as the identity provider for API client authorization, The

PingFederate Client Provider is configured in access management, and the PingFederate OAuth 2.0 Token Enforcement policy is configured for the API instances required by the

organization. The API instances reside in two business groups (Group A and Group B) within the Master Organization (Master Org).

What should be done to allow API consumers to access the API instances?

Correct answer: C

OAuth 2.0 and PingFederate Setup:

The organization uses PingFederate as the identity provider, integrated with Anypoint Platform for OAuth 2.0 authentication and authorization.

The PingFederate OAuth 2.0 Token Enforcement policy is applied to the API instances, requiring clients to be registered and authenticated via PingFederate.

Accessing Secured APIs:

API consumers need to register their client applications in Anypoint Exchange to request access to the secured APIs.

The API administrator then reviews and approves the access request in API Manager. This grants the client application a contract, allowing it to access the API using OAuth 2.0 tokens issued by PingFederate.

Evaluating the Options:

Option A: Configuring the client discovery URL in child business groups is not relevant to granting access; this is part of setting up PingFederate, not managing consumer access.

Option B: While creating contracts in API Manager is necessary, this option lacks the detail about the process in Anypoint Exchange, where consumers request access.

Option C (Correct Answer): API consumers must create a client application in Anypoint Exchange to request access to the API, and the API administrator then approves the request in API Manager.

Option D: The access request and approval process happens within Anypoint Platform (Exchange and API Manager), not directly in Ping Identity.

Conclusion:

Option C is the correct answer as it accurately describes the process within Anypoint Platform where API consumers request access through Exchange, and the API administrator approves it.

Refer to MuleSoft's documentation on OAuth 2.0 setup with PingFederate and managing API client access in Exchange and API Manager.


Unlock all Salesforce MuleSoft-Platform-Architect-I questions

Full exam access, validated answers, and unlimited practice with no download limits.

This exam tests more than memorization. Candidates must understand architectural design, API governance, CloudHub deployment, monitoring, and platform foundations at a practical level. It also evaluates how well you can apply MuleSoft and Anypoint Platform concepts to real-world architecture decisions and operational goals.

How QA4Exam.com Helps You Pass

QA4Exam.com offers Exam PDF and Online Practice Test materials that are built to support focused preparation for the Salesforce MuleSoft-Platform-Architect-I exam. The PDF gives you actual questions and answers in a convenient study format, while the practice test helps you experience real exam simulation before test day. Both formats are designed to provide up-to-date questions, verified answers, and a better understanding of the exam style and timing. With repeated practice, you can improve time management, strengthen weak areas, and build confidence for a first-attempt pass.

If you want a practical way to prepare for the Salesforce Certified MuleSoft Platform Architect exam, these study resources can help you study smarter and stay exam-ready.

Frequently Asked Questions

1. What is the Salesforce Certified MuleSoft Platform Architect exam?

It is a certification exam in the MuleSoft Certified Architect track that focuses on API architecture, governance, deployment, monitoring, and platform foundations within the MuleSoft and Anypoint Platform ecosystem.

2. Who should take the MuleSoft-Platform-Architect-I exam?

It is intended for professionals who work with MuleSoft architecture, API design, application networks, and platform-level implementation decisions. It is best suited for candidates who want to validate advanced architectural knowledge.

3. Is the exam difficult?

Yes, it can be challenging because it tests architecture understanding, governance decisions, deployment knowledge, and monitoring concepts rather than simple memorization. Preparation should cover both theory and practical application.

4. Can I pass with only braindumps?

Braindumps alone are not enough for reliable preparation. You should combine the dumps and practice test with hands-on knowledge and review of the exam topics to understand the concepts behind the questions.

5. Do I need hands-on experience to pass?

Hands-on experience is strongly recommended because many questions are based on architectural judgment and platform behavior. Practical exposure helps you answer scenario-based questions more confidently.

6. Are the QA4Exam.com dumps and practice test enough for first-attempt success?

They are very helpful for first-attempt preparation because they provide actual questions and answers, realistic exam simulation, and time management practice. For best results, use them together with topic review and hands-on study.

7. Do the QA4Exam.com materials include verified answers?

Yes, the Exam PDF and Online Practice Test are presented as study tools with verified answers to help you check your understanding and prepare more effectively for the exam.

8. How do these resources help with time management?

The practice test format lets you work through questions in a timed environment, which helps you learn how to pace yourself and avoid spending too long on any single question during the real exam.