
Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

ARA-R01 Exam Dumps and Practice Questions

Preview page 1 of 32 with real questions 1 to 5 from the full 162-question Snowflake set.

Snowflake ARA-R01 Dumps - Pass SnowPro Advanced: Architect Recertification Exam in 2026

The Snowflake ARA-R01 - SnowPro Advanced: Architect Recertification exam is part of the SnowPro Certification track and is designed for experienced Snowflake professionals who want to validate their advanced architecture knowledge. It focuses on the skills needed to design, optimize, secure, and manage Snowflake environments effectively. This recertification exam matters because it helps confirm that your knowledge stays aligned with current Snowflake architecture and best practices. It is especially relevant for architects and technical professionals responsible for real-world Snowflake implementations.

# Exam Topics Sub-Topics Approximate Weightage (%)
1 Data Engineering Data loading patterns, transformation workflows, pipeline design, data organization 30%
2 Performance Optimization Query tuning, warehouse sizing, caching behavior, performance troubleshooting 30%
3 Accounts and Security Role-based access, account configuration, authentication controls, governance basics 20%
4 Snowflake Architecture Storage and compute separation, virtual warehouses, shared data architecture, workload design 20%

This exam tests how well candidates understand Snowflake architecture concepts and how to apply them in practical scenarios. It checks both conceptual depth and the ability to make sound decisions around engineering, performance, and security. Candidates should be ready to analyze situations, choose the best approach, and demonstrate knowledge that reflects real Snowflake work.

Actual Snowflake ARA-R01 Exam Questions

Question 1

A group of Data Analysts have been granted the role analyst role. They need a Snowflake database where they can create and modify tables, views, and other objects to load with their own dat

a. The Analysts should not have the ability to give other Snowflake users outside of their role access to this data.

How should these requirements be met?

Correct answer: C

The requirements state that the data analysts need to be able to create and modify database objects and load data, but should not be able to manage access for users outside of their role.

Option C: By making each schema within the database a managed access schema and having them owned by SYSADMIN, the ability to grant privileges on the schema's objects is strictly controlled. Managed access schemas limit the granting of privileges to the role specified as the owner of the schema, in this case, SYSADMIN. The ANALYST_ROLE can be granted the privileges necessary to create and modify objects within these schemas, satisfying the requirement for the analysts to perform their tasks without being able to extend access beyond their role.
Question 2

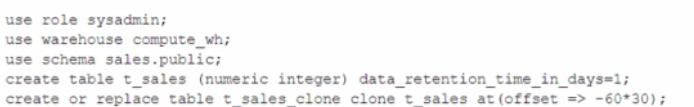
A user is executing the following command sequentially within a timeframe of 10 minutes from start to finish:

What would be the output of this query?

Correct answer: A

The query is executing a clone operation on an existing table t_sales with an offset to account for the retention time. The syntax used is correct for cloning a table in Snowflake, and the use of the at(offset => -60*30) clause is valid. This specifies that the clone should be based on the state of the table 30 minutes prior (60 seconds * 30). Assuming the table t_sales exists and has been modified within the last 30 minutes, and considering the data_retention_time_in_days is set to 1 day (which enables time travel queries for the past 24 hours), the table t_sales_clone would be successfully created based on the state of t_sales 30 minutes before the clone command was issued.


Question 3

Which of the following are characteristics of how row access policies can be applied to external tables? (Choose three.)

Correct answer: A, B, C

These three statements are true according to the Snowflake documentation and the web search results. A row access policy is a feature that allows filtering rows based on user-defined conditions. A row access policy can be applied to an external table, which is a table that reads data from external files in a stage. However, there are some limitations and considerations for using row access policies with external tables.

An external table can be created with a row access policy by using the WITH ROW ACCESS POLICY clause in the CREATE EXTERNAL TABLE statement.The policy can be applied to the VALUE column, which is the column that contains the raw data from the external files in a VARIANT data type1.

A row access policy can also be applied to the VALUE column of an existing external table by using the ALTER TABLE statement with the SET ROW ACCESS POLICY clause2.

A row access policy cannot be directly added to a virtual column of an external table. A virtual column is a column that is derived from the VALUE column using an expression.To apply a row access policy to a virtual column, the policy must be applied to the VALUE column and the expression must be repeated in the policy definition3.

External tables are not supported as mapping tables in a row access policy. A mapping table is a table that is used to determine the access rights of users or roles based on some criteria.Snowflake does not support using an external table as a mapping table because it may cause performance issues or errors4.

While cloning a database, Snowflake clones the row access policy, but not the external table. Therefore, the policy in the cloned database refers to a table that is not present in the cloned database.To avoid this issue, the external table must be manually cloned or recreated in the cloned database4.

A row access policy can be applied to a view created on top of an external table. The policy can be applied to the view itself or to the underlying external table.However, if the policy is applied to the view, the view must be a secure view, which is a view that hides the underlying data and the view definition from unauthorized users5.


CREATE EXTERNAL TABLE | Snowflake Documentation

ALTER EXTERNAL TABLE | Snowflake Documentation

Understanding Row Access Policies | Snowflake Documentation

Snowflake Data Governance: Row Access Policy Overview

Secure Views | Snowflake Documentation

Question 4

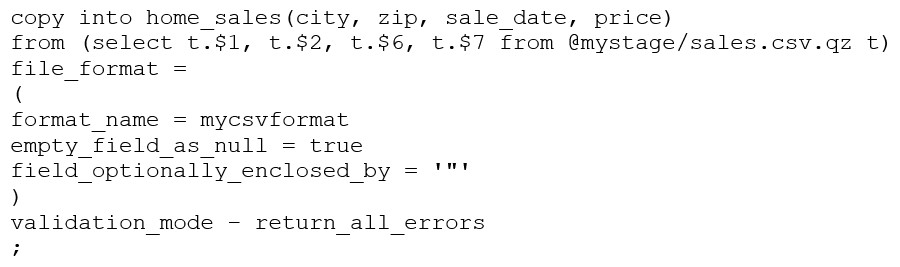
Consider the following COPY command which is loading data with CSV format into a Snowflake table from an internal stage through a data transformation query.

This command results in the following error:

SQL compilation error: invalid parameter 'validation_mode'

Assuming the syntax is correct, what is the cause of this error?

Question 5

A healthcare company is deploying a Snowflake account that may include Personal Health Information (PHI). The company must ensure compliance with all relevant privacy standards.

Which best practice recommendations will meet data protection and compliance requirements? (Choose three.)

Correct answer: A, B, D

A healthcare company that handles PHI data must ensure compliance with relevant privacy standards, such as HIPAA, HITRUST, and GDPR.Snowflake provides several features and best practices to help customers meet their data protection and compliance requirements1.

One best practice recommendation is to use, at minimum, the Business Critical edition of Snowflake.This edition provides the highest level of data protection and security, including end-to-end encryption with customer-managed keys, enhanced object-level security, and HIPAA and HITRUST compliance2. Therefore, option A is correct.

Another best practice recommendation is to create Dynamic Data Masking policies and apply them to columns that contain PHI. Dynamic Data Masking is a feature that allows masking or redacting sensitive data based on the current user's role.This way, only authorized users can view the unmasked data, while others will see masked values, such as NULL, asterisks, or random characters3. Therefore, option B is correct.

A third best practice recommendation is to use the External Tokenization feature to obfuscate sensitive data. External Tokenization is a feature that allows replacing sensitive data with tokens that are generated and stored by an external service, such as Protegrity.This way, the original data is never stored or processed by Snowflake, and only authorized users can access the tokenized data through the external service4. Therefore, option D is correct.

Option C is incorrect, because the Internal Tokenization feature is not available in Snowflake.Snowflake does not provide any native tokenization functionality, but only supports integration with external tokenization services4.

Option E is incorrect, because rewriting SQL queries to eliminate projections of PHI data based on current_role() is not a best practice. This approach is error-prone, inefficient, and hard to maintain.A better alternative is to use Dynamic Data Masking policies, which can automatically mask data based on the user's role without modifying the queries3.

Option F is incorrect, because avoiding sharing data with partner organizations is not a best practice. Snowflake enables secure and governed data sharing with internal and external consumers, such as business units, customers, or partners. Data sharing does not involve copying or moving data, but only granting access privileges to the shared objects.Data sharing can also leverage Dynamic Data Masking and External Tokenization features to protect sensitive data5.


Unlock all Snowflake ARA-R01 questions

Full exam access, validated answers, and unlimited practice with no download limits.

Frequently Asked Questions

1. Who should take the Snowflake ARA-R01 exam?

This recertification exam is intended for candidates in the SnowPro Certification track who already have advanced Snowflake architecture knowledge and need to validate it again.

2. Is the SnowPro Advanced: Architect Recertification exam difficult?

Yes, it can be challenging because it tests applied knowledge across data engineering, performance optimization, accounts and security, and Snowflake architecture.

3. Can I pass with only braindumps?

Braindumps alone are not the best approach. You should also understand the concepts and use practice tests to improve accuracy and confidence.

4. Do I need hands-on experience to pass ARA-R01?

Hands-on experience is very helpful because the exam focuses on practical Snowflake knowledge and architecture decisions, not just memorization.

5. Are the QA4Exam.com dumps enough, or should I use other resources too?

The QA4Exam.com Exam PDF and Online Practice Test are valuable tools, and combining them with your own review of Snowflake topics can strengthen preparation further.

6. How do the QA4Exam.com practice test and PDF help with first-attempt success?

They help you study actual questions and answers, practice under exam-like conditions, and improve time management so you can perform better on the first attempt.

7. What format do the QA4Exam.com dumps and practice test use?

QA4Exam.com provides an Exam PDF and an Online Practice Test format, giving you flexible ways to review questions, answers, and exam-style practice.