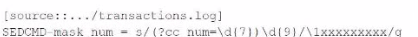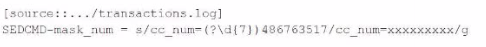Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam
Logo

- Trusted Worldwide Questions & Answers

Exam dumps demo

SPLK-1005 Exam Dumps and Practice Questions

Preview page 1 of 16 with real questions 1 to 5 from the full 80-question Splunk set.

Splunk SPLK-1005 Dumps - Pass Splunk Cloud Certified Admin Exam in First Attempt 2026

The Splunk SPLK-1005 exam is the certification exam for the Splunk Cloud Certified Admin credential. It is designed for professionals who manage Splunk Cloud environments and want to validate their knowledge of cloud administration tasks, data onboarding, configuration, and support processes. Passing this exam shows that you can work confidently with Splunk Cloud features and admin workflows in real-world environments. It is a valuable step for administrators who support data ingestion, user access, and app management in Splunk Cloud.

# Exam Topics Sub-Topics Approximate Weightage (%)
1 Splunk Cloud Overview Cloud platform concepts, admin responsibilities, service architecture, key features 8%
2 Index Management Creating and managing indexes, retention settings, storage behavior, index validation 9%
3 User Authentication and Authorization Roles and capabilities, user access, authentication methods, permission control 8%
4 Splunk Configuration Files Basic file structure, configuration precedence, managing settings, troubleshooting configs 8%
5 Getting Data in Cloud Data onboarding methods, source types, ingestion workflow, cloud data intake basics 10%
6 Forwarder Management Forwarder setup, deployment approach, communication with cloud, forwarder monitoring 8%
7 Monitor Inputs File monitoring, input settings, source tracking, input behavior 6%
8 Network and Other Inputs TCP and UDP inputs, syslog-style data, scripted or custom inputs, input selection 8%
9 Fine-tuning Inputs Input filtering, performance considerations, source handling, ingestion refinement 7%
10 Parsing Phase and Data Preview Timestamp handling, event breaking, field preview, parsing validation 8%
11 Manipulating Raw Data Transforms, line merging, data normalization, raw event adjustments 7%
12 Installing and Managing Apps App deployment, app updates, app permissions, managing app behavior 6%
13 Working with Splunk Cloud Support Support cases, escalation flow, issue reporting, cloud support coordination 7%

This exam tests practical Splunk Cloud administration knowledge, not just memorization. Candidates should understand how to manage indexes, control user access, configure inputs, and troubleshoot data onboarding in a cloud environment. It also checks how well you can apply Splunk configuration and support processes to common administrative scenarios. Strong hands-on familiarity with Splunk Cloud tasks can make a major difference in performance.

Actual Splunk SPLK-1005 Exam Questions

Question 1

Which of the following is not considered a best practice for the deployment server?

Correct answer: D

In Splunk, it's considered best practice to create small, single-purpose deployment apps rather than large, multi-purpose ones. This approach ensures better manageability, easier updates, and clearer version control. Option D, which suggests creating large, multi-purpose deployment apps, is not a best practice.

Splunk Documentation Reference: Deployment Server Best Practices
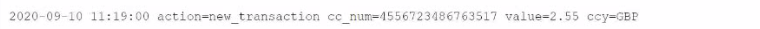

Question 2

Which of the following are features of a managed Splunk Cloud environment?

Correct answer: C

In a managed Splunk Cloud environment, several features are available to ensure that the platform is secure, scalable, and meets enterprise requirements. The key features include:

Availability of premium apps: Splunk Cloud supports the installation and use of premium apps such as Splunk Enterprise Security, IT Service Intelligence, etc.

SSO Integration: Single Sign-On (SSO) integration is supported, allowing organizations to leverage their existing identity providers for authentication.

IP address whitelisting and blacklisting: To enhance security, managed Splunk Cloud environments allow for IP address whitelisting and blacklisting to control access.

Given the options:

Option C correctly lists these features, making it the accurate choice.

Option A incorrectly states 'no IP address whitelisting or blacklisting,' which is indeed available.

Option B mentions 'no SSO integration' and 'no availability of premium apps,' both of which are inaccurate.

Option D talks about a 'maximum concurrent search limit of 20,' which does not represent the standard limit settings and may vary based on the subscription level.

Splunk Documentation Reference:

Splunk Cloud Features and Capabilities

Single Sign-On (SSO) in Splunk Cloud

Security and Access Control in Splunk Cloud


Question 3

The following sample log event shows evidence of credit card numbers being present in the transactions. loc file.

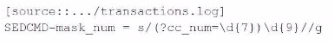
Which of these SEDCM3 settings will mask this and other suspected credit card numbers with an Y character for each character being masked? The indexed event should be formatted as follows:

A)

B)

C)

D)

Correct answer: A

The correct SEDCMD setting to mask the credit card numbers, ensuring that the masked version replaces each digit with an 'x' character, is Option A.

The SEDCMD syntax works as follows:

s/ starts the substitute command.

(?cc_num=\d{7})\d{9}/ matches the specific pattern of the credit card number in the logs.

\1xxxxxxxxx replaces the matched portion with the first captured group (the first 7 digits of the cc_num), followed by 9 'x' characters to mask the remaining digits.

/g ensures that the substitution is applied globally, throughout the string.

Thus, Option A correctly implements this requirement.

Splunk Documentation Reference: SEDCMD for Masking Data


Question 4

In what scenarios would transforms.conf be used?

Correct answer: B

transforms.conf is used for various advanced data processing tasks in Splunk, including:

Per-Event Sourcetype: Dynamically assigning a sourcetype based on event content.

Per-Event Host Name: Dynamically setting the host field based on event content.

Per-Event Index Routing: Directing specific events to different indexes based on their content.

Option B correctly identifies these common uses of transforms.conf.

Splunk Documentation Reference: transforms.conf - Configuration


Question 5

Where can an administrator download the Splunk Cloud Universal Forwarder credentials package?

Correct answer: C

The Universal Forwarder credentials package is available in the Splunk Cloud search head's Universal Forwarder app for secure, managed deployment. [Reference: Splunk Docs on Universal Forwarder credentials package]


Unlock all Splunk SPLK-1005 questions

Full exam access, validated answers, and unlimited practice with no download limits.

How QA4Exam.com Helps You Pass

QA4Exam.com offers the SPLK-1005 Exam PDF and Online Practice Test to help you prepare with confidence. The PDF gives you actual questions and answers in a convenient study format, while the practice test helps you experience a real exam-style environment. Both resources are updated to reflect current exam needs, so you can study with verified answers and relevant content. The practice test also helps you improve time management and identify weak areas before exam day. With focused preparation, you can approach the Splunk Cloud Certified Admin exam with greater confidence and a stronger chance of passing on the first attempt.

FAQ

Who should take the Splunk SPLK-1005 exam?

This exam is for candidates who want the Splunk Cloud Certified Admin certification and work with Splunk Cloud administration tasks such as data onboarding, access control, and configuration management.

Is the SPLK-1005 exam difficult?

It can be challenging if you only study theory. The exam focuses on practical admin knowledge, so understanding Splunk Cloud concepts and workflows is important.

Can I pass SPLK-1005 with only braindumps?

Braindumps alone are not the best approach. They can help you review question patterns, but you should also understand the topics and practice with exam-style questions.

Do I need hands-on experience with Splunk Cloud?

Yes, hands-on experience is strongly recommended. The exam covers real administrative tasks, and practical familiarity helps you answer scenario-based questions more confidently.

How can QA4Exam.com help me pass on the first attempt?

QA4Exam.com provides updated questions and answers, a realistic practice test, and exam-focused study material that helps you review the most relevant areas before test day.

What is included in the QA4Exam.com dumps and practice test format?

The Exam PDF is designed for quick review of actual questions and answers, while the online practice test simulates the exam environment and helps you practice under time pressure.

Do I need other study resources besides dumps and practice tests?

Using additional study resources can improve your understanding, especially if you want deeper knowledge of Splunk Cloud administration. Dumps and practice tests are useful for focused exam preparation, but concept review is still valuable.