Limited-Time Offer: Enjoy 50% Savings! - Ends In 0d 00h 00m 00s Coupon code: 50OFF
Welcome to QA4Exam

Practice questions demo

3V0-24.25 Exam Dumps and Practice Questions

Questions 1 to 5 of the 83-question 3V0-24.25 bank, each with its correct answer and an explanation. 2 of 5 ask for more than one answer. This is page 1 of 17.

1 / 17

Actual VMware 3V0-24.25 Exam Questions

Question 1

What is the function ofContourin a VMware vSphere Kubernetes Service (VKS) cluster?

Correct answer: A

In VCF 9.0, ingress is described as part ofVKS cluster networking. The documentation's VKS Cluster Networking table lists''Cluster ingress''and identifies its role asrouting inbound pod traffic. It further clarifies that this function is delivered by athird-party ingress controller, and explicitly namesContouras an example (''you can use any third-party ingress controller, such as Contour'').

That mapping is exactly what optionAdescribes: Contour is deployed to provideingresscapabilities so that inbound requests from outside the cluster can be routed to Kubernetes services and pods according to ingress rules. In other words, Contour is not a storage component (that would align to CSI/CNS/pvCSI), not a node lifecycle manager (that is handled by VKS/Cluster API/VM Service), and not an infrastructure health monitoring tool (that would be metrics/observability tooling). VCF 9.0 positions Contour specifically within theingresspart of the networking feature set, makingAthe correct answer.

Question 2

A company standardized on the following configurations:

* vSphere Kubernetes Service (VKS) upgrade is separate from vCenter upgrades.

* A private registry will be utilized.

How should an administrator adhere to these standards?

Correct answer: C

VCF 9.0 documentation explicitly indicates thatvCenter upgrades and the Supervisor/cluster (Workload Management) upgrade are distinct, noting that ''if you have only upgraded vCenter and not the cluster'' then DevOps engineers have reduced permissions until the cluster is upgraded. This supports the stated standard that VKS/Workload Management lifecycle can be treated separately from vCenter. For the private registry requirement, VCF 9.0 provides an operational mechanism to authenticate and pull artifacts from private registries: ''Registry secrets allow package and repository consumers to authenticate to and pull images from private registries,'' implemented via a standard Kubernetes Secret of type kubernetes.io/dockerconfigjson.

Taken together, the standard implies (1)asynchronoushandling (separate lifecycle from vCenter) and (2)privatesourcing (images pulled from an internal registry with registry secrets). Therefore, selectingAsynchronous Privatebest matches both requirements in a single configuration choice, aligning with the documented separation of upgrades and the documented need to use authenticated access to private registries.


Question 3

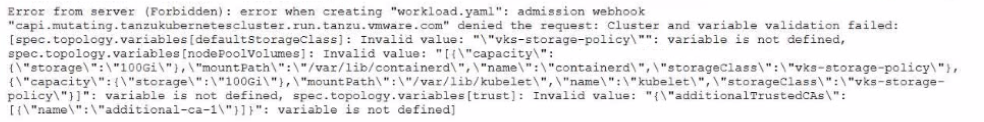
An administrator is upgrading to VKS 3.4 and encounters the following error during cluster creation using workload, yami:

How should the administrator resolve this issue to successfully complete the upgrade"?

Correct answer: B

The error shows an admission webhook denial wherevariable validation failedand multiple entries under spec.topology.variables3...] are reported as''variable is not defined''. That message indicates the manifest is supplying variables that arenot part of the current Cluster API / topology schemaenforced by the Supervisor during cluster creation. In VKS, cluster provisioning isdeclarative: you invoke the VKS API withkubectl + a YAML file, and ''after the cluster is created, you update the YAML to update the cluster.'' When the API/schema changes between releases, older manifests can contain fields/variables that are no longer recognized, and the admission webhook blocks them to prevent creating an invalid cluster spec.

This aligns with VMware's broader direction that the olderTanzuKubernetesCluster (TKC) API was deprecatedand customers are encouraged to useCluster APIfor bootstrap/config/lifecycle management. In practice, to complete the upgrade/creation successfully, you must update the cluster manifest to match the supported schema:remove the deprecated/unknown topology variablesshown in the error (for example, the undefined storage-policy and trust variables) and re-apply the correctedworkload.yaml.


Question 4

Which two capabilities are standard within a service mesh? (Choose two.)

Correct answer: B, C

Service mesh technology, such as Istio integrated within VMware Cloud Foundation (VCF) 9.0 and vSphere Kubernetes Service (VKS), is designed to solve the complexities of microservices communication. Two of the most fundamental capabilities provided by a service mesh are Service discovery and Connection encryption. In a dynamic Kubernetes environment where pods are frequently created and destroyed, Service discovery allows microservices to locate and communicate with each other automatically without requiring hardcoded IP addresses or manual configuration changes. The service mesh control plane maintains a real-time registry of all active service instances and their locations.


Question 5

What three controllers maintain the lifecycle of VMware vSphere Kubernetes Service (VKS) clusters? (Choose three.)

Correct answer: B, C, E

The VCF 9.0 documentation explicitly states that''the VKS exposes three layers of controllers to manage the lifecycle of a VKS cluster.''Those three controller layers map directly to the answer choices:

Cloud Provider Plug-in: VKS-provisioned clusters include components needed to integrate with vSphere Namespace resources, including aCloud Provider Plug-inthat integrates with the Supervisor and supports infrastructure-integrated functions (for example, passing persistent volume requests to the Supervisor which integrates with Cloud Native Storage).

Cluster API: The documentation describesCluster APIas providing declarative APIs for ''cluster creation, configuration, and management,'' including resources for the VMs and cluster add-ons.

Virtual Machine Service: TheVirtual Machine Serviceprovides declarative APIs to manage VMs and associated vSphere resources, and is used to manage the lifecycle of the control plane and worker node VMs that host a VKS cluster.

CNI and CSI are important cluster components, but the document distinguishes these from thethree controller layersresponsible for lifecycle management.


Unlock all VMware 3V0-24.25 questions

Full exam access, validated answers, and unlimited practice with no download limits.